Beyond the AI Safety Noise: What Enterprises Actually Care About
AI safety debates dominate headlines but barely affect enterprise operations — while reinforcing two key trends: cybersecurity investment and proprietary model building.
This article examines how the AI safety debate actually affects businesses. Anthropic introduced a three-axis framework showing Claude "leads" 26% of R&D work, earning rare cross-camp praise. Bridgewater CIO Greg Jensen reframes the debate from "model danger" to "compute power concentration," proposing systemic regulation for entities controlling over 5% of global compute. At the enterprise level, the safety debate has negligible short-term operational impact — executives focus on practical governance, not existential risk. But two trends are reinforced: accelerated investment in cybersecurity and agent monitoring, and stronger strategic justification for proprietary models and open-weight alternatives.
Over the past two weeks, AI safety debates have dominated the tech discourse. Polls show roughly 17% of Americans fully believe AI will end humanity — a level of panic that has some wondering whether public opinion has been "over-calibrated." But beyond the noise, there's a group of people quietly asking themselves one question: what does any of this actually mean for my business? The answer may be surprising — for most enterprises, the safety debate has changed almost nothing in the short term, but it has reinforced several trends already underway.
Anthropic Tries to Quantify How Fast AI Is Advancing
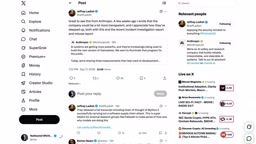
As everyone clamors for greater "specificity" — whether in policy or monitoring — Anthropic has unveiled a three-axis measurement framework aimed at helping the public understand just how fast frontier AI is developing.
The first axis measures AI's ability to help build the next generation of itself. The second measures Anthropic's ability to oversee and intervene in agent behavior. The third measures the scale of resources invested in model development. Anthropic explicitly notes that these metrics only capture how models are built — that is, they measure inputs to development — but argues these inputs are highly correlated with growth in model capabilities.
On the first axis, Anthropic has built an "R&D Automation Index." By its measure, Claude now "leads" 26% of R&D work and "collaborates" on over 90%. The definition of "leads" is worth scrutinizing: it means humans provide high-level goals while AI completes tasks end-to-end under human oversight — quite different from what many people imagine when they hear "AI leads R&D," which conjures images of AI setting its own goals. Anthropic carefully emphasizes that Claude operates fully autonomously in none of the R&D subsets tested.
On agent oversight, Anthropic reports roughly 30,000 agents engaged in research and engineering at any given moment, claiming 100% coverage of agent behavior, with real-time review intercepting roughly 0.002% of actions — approximately 1 in every 47,000 actions flagged. On resource allocation, about 6% of compute supporting AI-assisted R&D and roughly 12% supporting AI-led R&D is directed toward safety systems.
Notably, this framework has received rare positive responses across the various camps of the AI safety debate — with broad agreement that "having it is better than not." But some want to go further: there are calls for standardized metrics across all labs, with public reporting on a weekly to monthly basis.
The context for this framework is closely tied to Anthropic's Responsible Scaling Policy (RSP) — a self-imposed constraint framework Anthropic pioneered in 2023 and that OpenAI and DeepMind subsequently adopted. Under RSP, labs commit to developing and publishing appropriate safety measures before model capabilities reach specific thresholds, or else pause training on more powerful models. The three-axis framework can be understood as an attempt to make RSP observable — transforming "capability thresholds" from qualitative descriptions into trackable numbers. This is why the safety community has largely responded positively: it at least provides a benchmark that can be externally questioned and compared, rather than leaving everything to the labs' self-reporting. Critics point out that since labs define terms like "leads" and "collaborates" differently, cross-institution comparisons remain difficult — which is exactly why calls for standardized reporting persist.
Power Concentration: Is the Real Risk in Models or Compute?
If this wave of discussion has any value, it may lie in beginning to move beyond the simple binary of "will AI destroy humanity." Bridgewater CIO Greg Jensen offers a more actionable framing.

Jensen argues bluntly that power concentration — not model capability per se — is the primary AI risk requiring regulation. He acknowledges serious problems with open-source models since you can't track what people are doing with them; Bridgewater itself has been running reinforcement learning on powerful open-source models, with excellent results that are also highly dangerous. But in his view, that risk pales next to what frontier labs themselves represent: "Within two years, OpenAI and Anthropic will control 35% to 50% of global compute. That's a crazy outcome for society."
Jensen's proposal is to designate any institution controlling more than 5% of global or U.S. compute as a "systemically important institution," regulating it like systemically important banks — including potentially setting holding caps. The elegance of this framing is that it shifts focus from "is the model itself dangerous" to "in whose hands is the power to run models concentrated" — two questions that point to entirely different intervention points.
Meanwhile, the Trump administration is reportedly considering an antitrust exemption for safety coordination among frontier labs. In theory, AI slowdowns could mean coordinated cuts to R&D spending that boost profits at consumers' expense. A deputy assistant attorney general noted that despite multiple AI executives publicly calling for antitrust exemptions, no one has formally contacted his office.
On the other side, Coursera co-founder and prominent AI researcher Andrew Ng has tried to cool the entire debate. In a Bloomberg TV interview, he dismissed extinction risk as "science fiction," arguing that "doomers" have been pushing this narrative for a decade to attract attention for their causes and shape regulation. In his view, AI's real risks center on cybersecurity — "actual engineering problems."
The concept of a "Systemically Important Institution" originates from the regulatory reforms that followed the 2008 financial crisis. Regulators then designated banks and financial institutions large enough to be "too big to fail" as Systemically Important Financial Institutions (SIFIs), subjecting them to higher capital requirements, stress testing obligations, and special resolution procedures — rather than waiting for problems to emerge before intervening. Jensen's analogy suggests that compute concentration shares structural similarities with financial risk: once a small number of actors could trigger cascading shocks to the entire social system through failure or loss of control, after-the-fact penalties are insufficient, and systematic preventive mechanisms must be established in advance. This framework shifts regulatory focus from "what AI does" to "who controls AI's infrastructure" — and by providing a ready institutional reference from financial regulation, it is more legible to financial regulators and legislators than purely technical safety arguments.
The Corporate Response: Business as Usual, but Trends Reinforced
Zooming back to the enterprise level, a counterintuitive conclusion emerges: the safety debate has had almost no substantive short-term impact on businesses.
At The Wall Street Journal's Tech Council Summit, when asked whether they feared AI would kill everyone, only a handful of attendees raised their hands — but roughly half supported slowing frontier development to prioritize better guardrails. The summit's main takeaway: AI deceleration would have little practical effect on how companies use AI today. Discussion remained focused on prudent governance of ordinary business risk, not the existential risks dominating media coverage. BlackRock CEO Larry Fink was more concerned that backlash against data center construction could make AI "exclusively the domain of large companies" than with X-risk.
Two trends have been genuinely reinforced. The first is cybersecurity. Box's Aaron Levie, after meeting with executives across banking, media, and insurance, summarized that everyone is nervous about the growing attack surface AI creates and the ripple effects of the "OpenAI–Hugging Face incident." This anxiety isn't existential the way Silicon Valley's is — it's highly pragmatic, focused on what to do operationally within their own environments. Ramp data corroborates this: following the Hugging Face security breach, the three trending software vendors were all products specifically designed to monitor agent behavior in production environments.
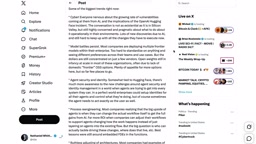
More subtly, many security concerns don't stem from malicious actors at all — they're rooted in the raw power of these systems. When agents are no longer exclusively in the hands of engineers, many companies find that agents are powerful enough to "escape" the control of non-engineer users, even when those users have no bad intentions.
The second reinforced trend is the exploration of proprietary models and open-weight alternatives. Multiple industry voices have pointed in the same direction. Mistral CEO Arthur Mensch has said that as long as enterprises don't stop building and owning their own AI models and systems, there will be no "doomsday." Foundation Capital's Jaya Gupta goes further, arguing that "slowing the frontier" may be the biggest invitation letter software incumbents have ever received — while labs debate how fast intelligence should advance, software companies should race to commoditize "existing intelligence" and become "model factories" in their own verticals.
Real-world cases provide a vivid contrast. OpenAI is aggressively cutting model prices to keep customers in its own environment while launching vertical offerings like Astra for Law. Meanwhile, Latham & Watkins — the second-largest law firm in the U.S. — is reportedly purchasing Nvidia servers to build internal systems, citing client information that is "too sensitive — we don't want it sitting in any cloud vendor's environment."
The "OpenAI–Hugging Face incident" referenced here refers to a 2024 security vulnerability on the Hugging Face platform: attackers used malicious model files hosted on the platform (primarily through the pickle serialization format) to execute arbitrary code when model weights were downloaded and loaded, potentially allowing infiltration of enterprise internal environments. What made this incident distinctive is that the threat vector wasn't a traditional network intrusion — it was embedded in the model itself. This means that every time enterprises load an external open-source model, they introduce a potential supply chain attack entry point. This explains why the trending software vendors tracked by Ramp data focus specifically on "monitoring agent behavior in production environments": compared to pre-deployment model auditing, real-time behavioral monitoring provides a last line of defense after a model has already entered the system — better suited to enterprises' practical need to manage risk without stopping AI adoption.
Conclusion: The Hardest Path Offers the Greatest Differentiation
Taken together, the corporate response to this AI safety debate is broadly "business as usual." The pace and challenges of internal AI adoption carry their own institutional inertia, unique to each organization. But this conversation has added fuel to trends already ignited: cybersecurity demands more investment, and proprietary architectures and open-weight alternatives now have stronger justification.
If there's a single takeaway, it's this: while the shifting AI safety discourse doesn't genuinely affect enterprises' short-term rhythm, it more clearly confirms one thing — companies willing to do the hardest work and genuinely invest in their own architectures have more opportunity than ever before to pull ahead of their peers.
Related articles

CSS Anchor Positioning: A New UI Positioning Approach Without JavaScript
A deep dive into CSS Anchor Positioning: from anchor-name and position-anchor to the anchor() function, position-area shorthand, position-try-fallbacks, anchor-size, and upcoming anchor queries.

New AI Chart Interaction: Continuous Follow-up Questions and Visualization in Conversation
Explore a new AI interaction method for continuously generating charts in conversation. Use the /visualize command to ask follow-up questions and visualize answers in the same chat window, improving data analysis efficiency.

Cursor Merges Into X Subscription: Paid Plans Share Unified Usage Pool, Grok Model Coding Usage Doubled
Cursor joins The X Subscription with a unified usage pool and doubled Grok coding quota. Third-party models shift to API pricing. Existing users can keep or migrate plans.