Claude Extension Backdoored for Nearly 12 Hours, Cursor Users Should Be Alert

Cursor extension 2.1.313 was implanted with malicious code for nearly 12 hours, putting about 5,000 developers at risk of SSH backdoors and cloud credential theft.
Version 2.1.313 of the official Cursor extension was implanted with malicious code by an attacker through a verified Anthropic account and persisted for nearly 12 hours, potentially affecting up to about 5,000 users. The malicious code attempted to install an SSH backdoor on Windows, macOS, and Linux, and collected environment variables to steal cloud service credentials and send them back to the attacker's server. Fortunately, the malicious code had flaws, and the SSH backdoor failed to install in most cases, but whether the data exfiltration succeeded remains unclear. Cursor has removed the malicious version, pushed fixed version 2.1.314, and rotated the related keys. The incident exposed the fragility of the extension marketplace's automatic update mechanism and account security. Developers need to immediately investigate abnormal SSH configurations and cloud credential usage records, and consider disabling automatic updates or strengthening manual confirmation.
Incident Overview: A Supply Chain Attack Targeting Developers
According to the YouTube channel "Athensino Club," their officially published Cursor extension (version 2.1.313) was implanted with malicious code for nearly 12 hours, with an estimated maximum of about 5,000 users potentially affected. The extension is related to Claude, and the attacker pushed the malicious version through a verified Anthropic account. Because Cursor enables automatic updates by default, many developers upgraded without knowing it.
This incident once again sounds the alarm on the security of the developer toolchain. Although the auto-update mechanism in extension marketplaces is convenient, it also gives attackers an opportunity—once an account is compromised, malicious code can spread rapidly.
Supply chain attack refers to an attack in which the attacker does not directly target the end goal, but instead indirectly achieves the objective by compromising trusted third-party components, tools, or services. In the developer ecosystem, common vectors include software package repositories (such as npm and PyPI), IDE extension marketplaces, CI/CD pipelines, and code dependencies. Such attacks are dangerous because malicious code spreads through legitimate distribution channels and automatic update mechanisms, bypassing users' trust judgment of "official sources." Defending against supply chain attacks requires platforms to strengthen release review and account security, while developers should perform integrity verification and abnormal behavior monitoring on dependencies.
What the Malicious Code Did: SSH Backdoor and Credential Theft
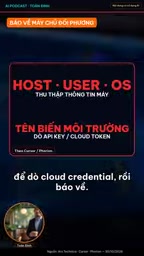
According to the disclosed information, the malicious code attempted to install a long-term SSH backdoor on three platforms: Windows, macOS, and Linux. In addition, it collected machine information and environment variable names in order to read cloud service credentials (Cloud Credential) and transmit these data back to a server controlled by the attacker.
This technique combines persistent access and credential theft, posing a major threat to developers who use cloud services. Once the SSH backdoor is successfully installed, the attacker can remotely control the victim's development machine over the long term; and leakage of cloud credentials may lead to abuse of cloud resources or data breaches.
SSH backdoor refers to a persistent access channel implanted by an attacker in the target system that can bypass normal authentication mechanisms and allow remote login. Common implementations include appending an attacker-controlled public key to the ~/.ssh/authorized_keys file, or modifying the SSH service configuration to allow password login, listen on non-standard ports, and so on. Once the backdoor takes effect, the attacker can control the development machine over the long term through the SSH protocol without the user's password, and then steal code, move laterally, or deploy further payloads. Because developer machines usually store source code, cloud platform keys, and internal network access permissions, SSH backdoors are especially serious threats to the software supply chain.
Cloud Credential usually exists in the development environment in the form of environment variables, such as AWS_ACCESS_KEY_ID, AWS_SECRET_ACCESS_KEY, AZURE_CLIENT_SECRET, and so on. The malicious code collected environment variable names and sent them back in order to locate these high-value credentials, and then call cloud APIs to create resources, steal data, or escalate privileges. Developers should use short-term tokens, the principle of least privilege, and key management services to reduce such risks.
A Silver Lining: The Malicious Code Had Flaws
The good news is that the malicious code itself contained errors, causing the SSH backdoor installation to fail in most cases. This may have been an oversight by the attacker when writing the code, or it may have been caused by compatibility issues across different platforms. Nevertheless, whether the data collection and exfiltration portion was successfully executed remains unclear, so affected users should still not let their guard down.
Official Response and User Recommendations
After the incident was exposed, Cursor removed the malicious version, pushed a fixed version 2.1.314, and rotated the related keys. For users who updated the extension during the affected period, it is recommended to take the following measures immediately:
- Check whether there are abnormal SSH authorized keys or configuration file changes on the development machine;
- Review usage records of cloud service credentials and rotate all potentially exposed keys if necessary;
- Follow official announcements from Cursor and Anthropic for the latest developments;
- Consider disabling automatic updates in extension management, or at least manually confirming updates for critical extensions.
Implications for the Developer Ecosystem
This incident exposed the fragility of extension marketplaces in terms of account security and release processes. A verified account was enough to push a malicious version, and the automatic update mechanism allowed malicious code to reach a large number of users in a short time. For developers who rely on AI programming tools, in addition to paying attention to feature updates, they also need to incorporate supply chain security into their daily considerations.
From a broader perspective, AI-assisted development tools are rapidly becoming widespread, but their security governance systems are not yet mature. Platforms need to strengthen release review and introduce multi-factor authentication and code signing mechanisms; developers should remain vigilant and regularly review abnormal behavior in their development environments.
One-line Summary
Cursor extension 2.1.313 was implanted with malicious code for nearly 12 hours, and about 5,000 developers faced risks of SSH backdoors and cloud credential theft.
Paragraph Summary
Version 2.1.313 of the official Cursor extension was implanted with malicious code by an attacker through a verified Anthropic account and persisted for nearly 12 hours, potentially affecting up to about 5,000 users. The malicious code attempted to install an SSH backdoor on Windows, macOS, and Linux, and collected environment variables to steal cloud service credentials and send them back to the attacker's server. Fortunately, the malicious code had flaws, and the SSH backdoor failed to install in most cases, but whether the data exfiltration succeeded remains unclear. Cursor has removed the malicious version, pushed fixed version 2.1.314, and rotated the related keys. The incident exposed the fragility of the extension marketplace's automatic update mechanism and account security. Developers need to immediately investigate abnormal SSH configurations and cloud credential usage records, and consider disabling automatic updates or strengthening manual confirmation.
Related articles

VERS: Editing Activation Explanations to Halve Reasoning Model Tokens
VERS guides reasoning models by editing activation explanations, cutting 45.8% of tokens on GSM8K with only a 0.82 pp accuracy drop and transferring to larger models, but losing accuracy on competition problems.

Finding Errors Is Not Enough: Selective Model Escalation for Entity-Targeted Sentiment Analysis
This study explores selective model escalation for entity-targeted sentiment analysis, comparing data collection ordering, uncertainty-driven re-examination, and model routing—finding that minority-class priority only helps at very small data volumes, the oracle upper bound far exceeds actual gains, and escalation must be tailored to each dataset.

WAS-PO: Using Whitened Advantages to Solve the Correlation Trap in Multi-Reward Reinforcement Learning
WAS-PO paper proposes whitening advantages to correct correlation bias in multi-reward RL: when rewards are correlated, naive weighted summation effectively applies Σ^{1/2}w instead of w. Experiments show training reward improves steadily, but held-out accuracy does not improve in sync, and under two rewards it actually falls behind.