CLI v3.0.73 Released: The Tool Iteration Logic Behind a Minor Version Update

cli-v3.0.73 is a patch release without detailed notes, reflecting the small-step, rapid-iteration rhythm and upgrade strategy of open source CLI tools.
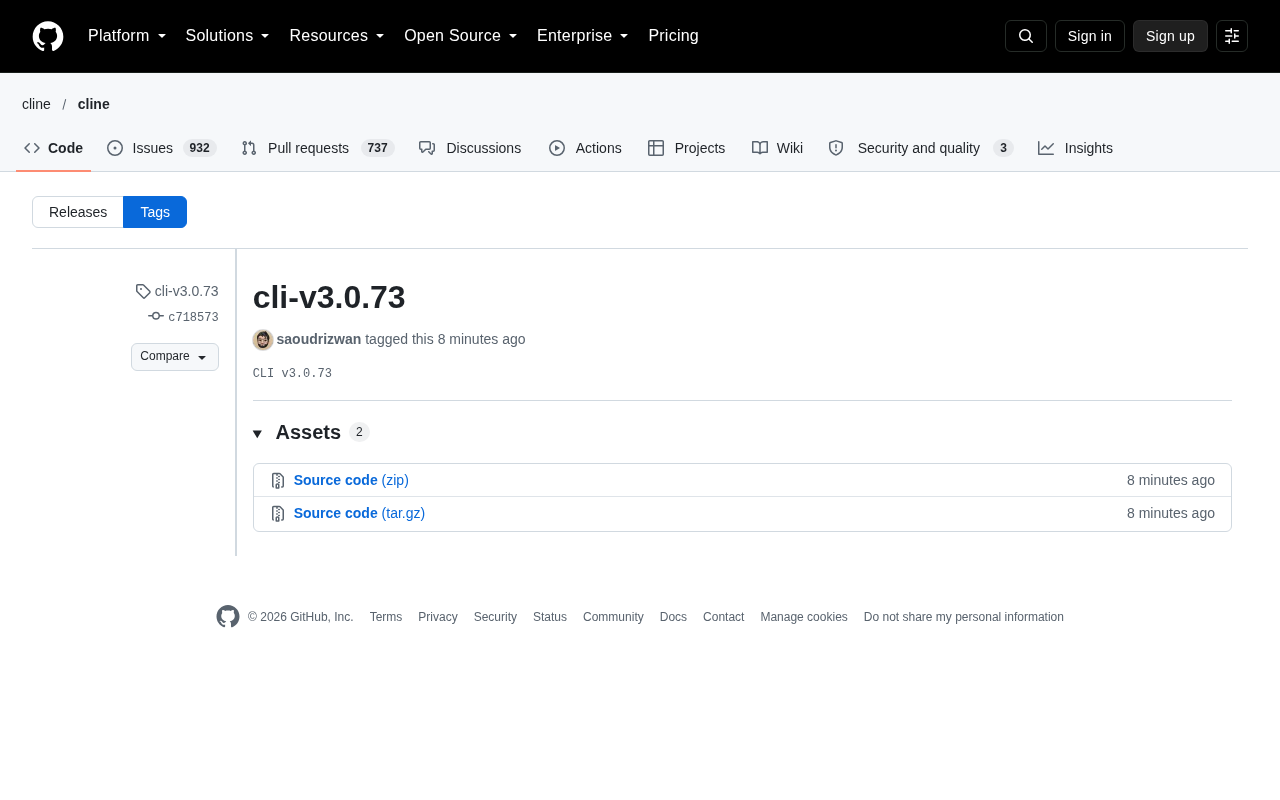
This article analyzes the release information for cli-v3.0.73: the version was tagged by saoudrizwan on October 17, has no detailed release notes, and includes only 2 build artifacts. The article notes that patch versions usually focus on bug fixes, dependency upgrades, and cross-platform compatibility improvements. High-frequency releases may reflect active maintenance or a larger number of legacy issues. It advises users to check diffs or commit records before upgrading, perform regression testing in CI/CD scenarios, and calls on maintainers to add release notes to improve version transparency.
Introduction: The Signal Behind the Version Number
The release information for cli-v3.0.73 comes from the GitHub repository's tag record, tagged by maintainer saoudrizwan on October 17. Judging from the public page, this release did not include detailed release notes and only provided build artifacts (2 Assets in total). For developers accustomed to reading changelogs, this is clearly not enough information. But the version number itself conveys an important signal: this command-line tool is still iterating at high frequency, and the patch release cadence of the 3.0.x series has not slowed down.
Common Drivers of Patch Version Iteration
Fixes Take Priority Over Features
Under semantic versioning conventions, an increment in the third digit usually means backward-compatible bug fixes. Compared with the previous version, v3.0.73 most likely focuses on defect fixes, dependency upgrades, or edge-case handling. For CLI tools, such updates often involve compatibility in argument parsing, cross-platform behavioral differences (such as path handling on Windows versus Unix), and improvements to the readability of error messages. Individually, these changes may seem unremarkable, but cumulatively they directly affect the daily user experience.
Semantic Versioning (SemVer) was proposed by Tom Preston-Werner and follows the format MAJOR.MINOR.PATCH. A MAJOR version increment indicates incompatible API changes, MINOR indicates backward-compatible feature additions, and PATCH indicates backward-compatible bug fixes. Therefore, the “73” in v3.0.73 indicates that this is the 73rd patch release after 3.0.0, usually containing only bug fixes and security patches, without introducing new features or breaking changes. Following SemVer helps users judge upgrade risk: patch version upgrades generally do not require concern about interface changes.
The Meaning of Build Artifacts
This release includes 2 Assets, indicating that the project still provides precompiled binaries for different platforms or architectures. For end users, this means they can download and use the tool directly without local compilation; for maintainers, the stability of a multi-artifact release process is itself an engineering problem that requires continuous maintenance.
Build artifacts (Assets) are downloadable files attached to GitHub Releases, typically including precompiled binaries, archives, checksum files, and more. For CLI tools, providing multi-platform binaries (such as different architectures for Linux, macOS, and Windows) can greatly lower the barrier to use, allowing users to run the tool directly without installing a build environment. At the same time, the publication of build artifacts is often automated through CI/CD pipelines, and its stability and consistency also reflect the project's level of engineering maturity.
Project Health as Seen Through Release Cadence
High-frequency patch releases usually reflect one of two possibilities: first, the project is active and maintainers respond promptly, quickly fixing issues once they are discovered; second, the 3.0 series still has many legacy issues and requires constant patching. A single version alone cannot determine which case applies, but given page states such as loading errors and filtering returning no results that have appeared on the tag page, the repository's release process may rely on automation tools and occasionally have rendering anomalies.
For users, a pragmatic approach is to pay attention to the frequency of version number changes: if 3.0.x releases are密集 in a short period, it is advisable to check commit history or diffs before upgrading rather than blindly following the latest tag.
In open source projects, the absence of release notes is not uncommon, especially when the release process is highly automated. Maintainers may rely on Git commit history or automatically generated changelogs, but user-facing release notes still have irreplaceable value: they help users quickly understand the highlights of a version, assess the necessity of upgrading, and reduce the burden of consulting commit records. The lack of release notes increases users' decision-making costs and may, over time, affect project transparency and community trust.
How to Reasonably Approach Such Minor Version Releases
Users of CLI tools generally fall into two categories: one seeks stability and locks in a validated version; the other chases new releases and wants fixes as soon as possible. For a patch version like v3.0.73, it is recommended to first verify in a test environment whether core commands behave consistently, and then decide whether to upgrade. Especially when the tool is integrated into a CI/CD pipeline, any version change should go through regression testing to avoid pipeline interruptions caused by subtle changes in argument parsing or output formatting.
If you are a contributor to the project, this version also reminds us: the absence of release notes increases users' decision-making costs. Even simply listing the issue numbers fixed can significantly improve version transparency.
Regression testing is a testing strategy in which existing test cases are rerun after software modifications to ensure that original functionality has not been broken. For CLI tools, regression testing should cover argument parsing, output formatting, exit codes, and cross-platform behavior of core commands. Integrating regression testing into CI/CD pipelines can automatically verify compatibility when upgrading dependencies or tool versions, avoiding pipeline interruptions caused by subtle behavioral changes. It is recommended to run a regression test suite for key commands in at least a test environment before upgrading a patch version.
Conclusion
cli-v3.0.73 is not a version that deserves extensive coverage, but it truthfully reflects the daily rhythm of open source CLI tools—small, rapid steps and continuous patching. Understanding this rhythm is more valuable than chasing every version number.
Related articles

Chain of Thought Isn't Just for AI: How Humans Can Use CoT to Improve Thinking Quality
Chain of Thought isn't just a prompt trick for large models. Starting from a Hacker News discussion, this article analyzes why CoT works for human thinking too, breaks down actionable ways to transfer it, and highlights the key differences between human CoT and machine CoT.
Cloudflare Teams Up with OpenAI: Closi…
Cloudflare Teams Up with OpenAI: Closing the Loop from Vulnerability Discovery to Defense with AI
Cloudflare uses OpenAI Daybreak to investigate security vulnerabilities and generate reviewable remediation plans, while developers use Codex to boost coding efficiency and quality.

Orca Multi-Agent Orchestration in Practice: A Guide to Parallel Collaboration with Claude and Codex
Orca is Stable AI's free open-source agent workbench supporting 34 agents like Claude Code and Codex in parallel. Learn its Git worktree isolation, multi-model orchestration, and mobile management.