How to Prevent Leaks in AI Chat Logs: A Developer's Practice and Reflections
AI chat logs are prone to key leaks; shape scrubbing plus a dedicated secure channel provides double protection.
The article discusses the risk of key leaks in AI coding agent chat logs and introduces a two-layer defense design using the open source application Styx as an example. The first layer is shape scrubbing: pattern matching removes content that looks like a secret before storage and rejects suspicious attachments, but the author admits this is only "a net, not a wall," and short passwords or internal URLs with tokens can still slip through. The second layer is a path that never touches the log: when the agent requests a secret, it uses a masked field, the answer is excluded from the conversation record, real credentials are stored in the operating system keychain, and everything else is referenced by ID. The article emphasizes that scrubbing cannot prevent information from being sent to the agent provider, and input should be treated as already shared; security is an ongoing process, not a one-time solution.
In an era where AI coding assistants are increasingly widespread, chat logs have become a new channel for sensitive information leaks. A developer shares how his application Styx protects secrets through shape scrubbing and a dedicated secure channel, while honestly acknowledging its limitations.
Chat Logs: A Breeding Ground for Key Leaks
The chat with a coding agent is essentially a log, and logs are exactly where secrets end up: a token pasted "just to try it out," a connection string in a stack trace, a key in an attached file. In the Styx application, everything stored first passes through a scrubber.
The first layer of this scrubber is shape-based scrubbing. Message text is stored with anything that looks like a secret removed, and content provided and saved by the agent goes through the same redaction. Attachments that look like keys or credentials are rejected outright.
Shape Matching: A Net, Not a Wall
The lesson of shape matching is that it is a net, not a wall. A secret that doesn't look like a secret—such as a short password or an internal URL with a token—will still slip through. This means pattern matching alone cannot provide an absolute security guarantee.
Shape-based matching relies on regular expressions or heuristic rules to identify the typical structure of keys, such as the AKIA prefix of AWS access keys, the ghp_ prefix of GitHub tokens, and the three-segment base64 structure of JWTs. The advantage of this approach is zero configuration and low latency, making it suitable as the first line of filtering on the storage path. But its fundamental flaw is that it can only recognize known formats with distinctive features: high-entropy random strings without a fixed prefix are hard to distinguish from ordinary text, and URLs with tokens often escape the rules because parameter names are non-standard. Common complementary measures in the industry include entropy-based detection (Shannon entropy) and machine learning classifiers, but the former has a high false positive rate, and the latter requires training data and is hard to explain. Therefore, shape matching should be regarded as one layer in defense in depth, not as a boundary.
The Second Layer of Defense: A Path That Never Touches the Log
Thus, the second layer is a path that never touches the log. When the agent needs to obtain a secret from the user, its question receives a masked field, and the answer is excluded from the conversation record. The actual credentials are stored in the operating system keychain, and everything else references them by ID.
The core recommendation of this design is: scrub by pattern as much as possible, but don't let patterns be your only defense. Give people a place to put secrets that is designed to never be recorded, and make it the easiest option.
The operating system keychain is the collective term for system-level credential stores such as macOS Keychain, Windows Credential Manager, and Linux Secret Service. They are protected by operating system encryption, access requires user session authorization, and applications read and write entries through APIs without directly touching plaintext. Storing keys in the keychain and keeping only ID references in the conversation essentially decouples the lifecycle of secrets from the chat log: even if the log is fully exported or leaked, it contains only meaningless identifiers. This pattern is consistent with OAuth refresh token storage and the secret manager approach in CI/CD, with the core principle being "secrets must not land on media reachable by logs." The cost is that the agent needs to resolve credentials by ID at runtime, increasing implementation complexity, but what it gains is a structural security guarantee.
Limitations: Risks That Still Exist
This method is of no help in the following situations: secrets entered into ordinary messages are still protected only by patterns. Moreover, scrubbing logs does not prevent anything from being sent to the agent's own provider, so treat anything you type into any agent as already shared with it.
It is necessary to distinguish between two levels: "log scrubbing" and "transmission security." The scrubber works at the local storage stage, while every request from the agent sends the conversation content to the model provider (such as OpenAI, Anthropic, or a self-hosted endpoint), a process that is not controlled by local scrubbing. In other words, even if the user never actively shares secrets, the model may still see sensitive information in the context during inference, and the provider's data retention policies, logging, and abuse monitoring may all constitute secondary exposure surfaces. Common mitigation measures in enterprise scenarios include zero data retention agreements, private deployment, and outbound traffic auditing, but none of these can replace the fundamental principle of "do not enter secrets."
Open Source Practice: Styx's Exploration
These lessons come from building Styx, an open source application that can run multiple coding agents side by side. It demonstrates a pragmatic approach to protecting sensitive information in AI tools, while also reminding us that security is an ongoing process, not a one-time solution.
For developers, the key takeaway is: in AI chats, never assume secrets are safe. Use shape scrubbing as a baseline defense, but more importantly, design a channel that never records secrets and educate users to use it correctly.
One-line Summary
AI chat logs are prone to key leaks; shape scrubbing plus a dedicated secure channel provides double protection.
Paragraph Summary
The article explores the risk of key leaks in AI coding agent chat logs and uses the open source application Styx as an example to introduce a two-layer defense design. The first layer is shape scrubbing: before storage, pattern matching removes content that looks like a secret and rejects suspicious attachments, but the author admits this is only "a net, not a wall," and short passwords or internal URLs with tokens can still slip through. The second layer is a path that never touches the log: when the agent asks for a secret, it uses a masked field, the answer is excluded from the conversation record, real credentials are stored in the operating system keychain, and everything else is referenced by ID. The article emphasizes that scrubbing cannot prevent information from being sent to the agent provider, and input should be treated as already shared; security is an ongoing process, not a one-time solution.
Related articles
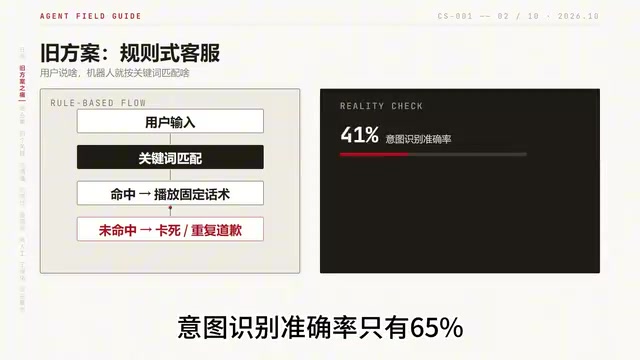
Building an AI Customer Service Agent from Scratch: A 92% Intent Recognition Case Study
A Bilibili case study: building an AI customer service agent from scratch with BERT intent recognition, dialogue state tracking, hybrid vector retrieval, and a weighted handoff model—raising intent accuracy from 65% to 92%, 78% conversation completion, handling 100K conversations daily.
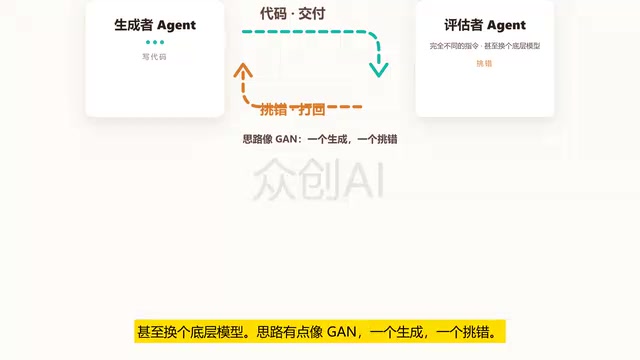
Loop Engineering: An Engineering Paradigm for AI That Writes Code and Merges PRs Autonomously
Loop Engineering is transforming AI development pipelines: Stripe's Minions system merges over 1,300 machine-generated PRs weekly. This article breaks down Loop Engineering's five core actions, six components, five failure modes, and three safety disciplines, explaining why independent evaluators, state files, and budget caps matter more than full automation.
Two Weeks of Spare Time: I Used AI to Build an Android "Book of Life" for My Parents
Inspired by the "Book of Life" AI Historian app, I took on a two-week challenge—one hour a day after work—using AI coding to build an Android Book of Life agent that turns ordinary people's stories into books.