Micron Launches 512GB DDR5 DIMM: The Eye-Watering Upgrade for Data Centers
Micron's $45K 512GB DDR5 DIMM, AI data center gas concerns, and a critical Cisco email gateway exploit.
Craft Computing episode 450 covers three major tech stories: Micron's industry-first 512GB DDR5-9200 RDIMM (16W, 60% more efficient, but ~$45–50K per stick), U.S. AI data centers projected to consume 15 billion cubic feet of natural gas daily by 2035 (a 117% spike), and a CVSS 9.8 vulnerability in Cisco's Secure Email Gateway that lets attackers gain root access by simply sending an email — with virtual appliances requiring full rebuilds and SMBs facing the greatest risk.
In episode 450 of Craft Computing's Talking Heads, hosts Jeff and Rhett covered three major tech stories: Micron's release of the industry's first 512GB DDR5 memory module, the energy and environmental concerns surrounding U.S. AI data centers, and a critical vulnerability in Cisco's Secure Email Gateway. Together, these topics paint a complete picture spanning hardware breakthroughs, infrastructure controversies, and cybersecurity.
Micron 512GB DDR5: Unprecedented Memory Density
Micron has announced the industry's first 512GB RDIMM module, running at DDR5-9200. Worth emphasizing: this is not an MRDIMM — it's a standard registered DIMM with full bit-for-bit ECC error correction, with no compromises whatsoever.
According to the hosts, the most striking aspect of this module is its power efficiency. Each module consumes just 16 watts — which may sound high for a memory stick, but represents a 60% efficiency improvement over conventional approaches needed to reach equivalent capacity. For context, a typical 128GB DIMM draws around 9 watts; four of them together consume 36 watts, while this single 512GB module needs only 16 watts.

From a system-level perspective, this density is a natural match for today's rapidly growing CPU core counts. Intel has already launched the 144-core Xeon 6E and is approaching the 288-core Clearwater Forest (Xeon 7x2); AMD currently offers 192-core processors with the next generation targeting 256 cores. In a dual-socket 256-core system with all 24 DIMM slots filled with 512GB modules, total capacity would reach 12TB, with memory bandwidth of approximately 12TB/s and an average of 24GB per core — in that context, 512GB per DIMM suddenly doesn't seem so excessive.
Price Is the Real Barrier
The hosts were blunt: this product is pure "unobtainium" from the moment it launches. Using the roughly $19,000 market price of 256GB modules as a reference, and factoring in the higher process complexity and density costs, a 512GB module is expected to land somewhere between $45,000 and $50,000 per stick. "If you fill a server with four of these, you could buy my house" — a quip that neatly captures the absurdity of today's memory market, where high-density enterprise DIMMs have become a pure capital game against a backdrop of broadly rising DRAM prices.
The core distinction between RDIMM (Registered DIMM) and standard UDIMM lies in an additional register chip placed between the memory controller and the DRAM chips. This register forwards command and address signals, reducing the electrical load on the memory controller and allowing more DIMMs per channel without sacrificing stability — which is why server platforms almost universally rely on RDIMMs.
ECC (Error Correcting Code) is the other defining feature that separates server memory from consumer-grade alternatives: it detects and corrects single-bit errors in real time, detects double-bit errors, and dramatically reduces the risk of bit flips caused by cosmic rays or electrical noise. "Bit-for-bit ECC" means every data bit is fully protected, without sacrificing any error-correction precision for performance or density — unlike some high-bandwidth memory approaches.
MRDIMM (Multiplexed Rank DIMM) is a new DDR5 specification that boosts bandwidth through multiplexing, at the cost of slightly higher latency and stricter requirements for motherboard and controller compatibility. By sticking with standard RDIMM, Micron ensures this module is compatible with existing DDR5 platforms without waiting for a new generation of board ecosystem support.
The Energy and Environmental Controversy Around U.S. AI Data Centers
The most emotionally charged segment of the episode was a critique of the energy mix powering U.S. AI data centers. According to data cited by Tom's Hardware from Bloomberg, by 2035, U.S. AI data centers are projected to become the world's fifth-largest consumer of natural gas — trailing only China, Russia, Iran, and other domestic U.S. uses.
The specific numbers are staggering: daily natural gas consumption by data centers is expected to reach 15 billion cubic feet by 2035, a 117% increase over the previous estimate of 6.9 billion cubic feet — effectively doubling current natural gas power generation consumption.
The hosts' central question was: why fossil fuels instead of cleaner alternatives? The answer is painfully pragmatic — natural gas turbines are the cheapest and fastest option to deploy. Solar, while renewable, costs roughly 15% more to build out and can't be brought online today. AI data centers need power now, not six months from now.
On the argument that "natural gas is just a bridge, and solar will come eventually," the hosts were sharply skeptical — pointing to Elon Musk's claim that natural gas would "support and guide solar within a few years" as an example of the kind of promise that often means "never," comparing it to long-delayed projects like Hyperloop and full self-driving.
The Communities Being Left Behind
The deeper critique was about who benefits. The hosts argued that if any AI data center developer were willing to invest in local power infrastructure and cut surrounding communities' electricity bills by 50%, they would get near-universal local support — because that would represent a genuine net benefit. Instead, data centers often pay no local taxes, consume vast amounts of land, and simply burn fossil fuels. "We're just begging for scraps and being told to get lost."
The tension between data centers and local communities is well-documented across the United States. Some states and counties have offered tax abatement agreements lasting ten to twenty years to attract data center investment, effectively shrinking budgets for public services like education and road maintenance — while the data centers themselves often employ only dozens to a few hundred local workers, far fewer than an industrial park of comparable size.
The energy dimension is equally concrete: when large-scale data centers connect to the grid, their peak demand can force grid operators to activate additional peaker plants (typically natural gas or even oil-fired), indirectly driving up retail electricity prices for nearby residents. This directly contradicts the official narrative of "data centers boosting the local economy" — and provides the policy context for the hosts' criticism that data centers neither pay taxes, nor share the land value, nor use anything but fossil fuels.
Cisco Secure Email Gateway: A Vulnerability You Can Trigger by Sending an Email
The most ironic story of the episode came from Cisco. According to The Register, Cisco disclosed a critical vulnerability with a CVSS score of 9.8 affecting its Secure Email Gateway appliances — both physical and virtual.
These devices act as mail server proxies or edge threat detectors, filtering malicious emails and attachments — essentially next-generation spam filters. The irony: a security device specifically designed to read all email content in plaintext failed to sanitize its inputs, meaning an attacker could send a single email and have its text execute as code. "Cisco's email security appliance can be rooted by sending it an email."
The vulnerability exists in how Cisco AsyncOS processes inbound email. An attacker can not only execute code but gain root access, tamper with logs, cover their tracks, and plant a backdoor — which is precisely why the score is so high. According to the report, criminals had already been actively exploiting the vulnerability for an unknown period of time.
No Workarounds — Just Patch
Cisco says it only became aware of the vulnerability this month but cannot determine how long it had been exploited. There are no temporary mitigations; the only fix is to apply the patch. The remediation process depends on how the device is deployed:
- Physical appliances: Can be updated directly, but logs and firewall records should be checked for anomalous traffic or suspicious running services.
- Virtual appliances: Cisco recommends rebuilding from scratch — export the configuration, spin up a fresh server, import the configuration, and verify it again. This is because virtual environments cannot use checksums to verify the integrity of a running configuration.
The hosts specifically flagged that large enterprises have sufficient IT and security staff to recover quickly even if compromised. The real danger is small and medium-sized businesses that have outsourced their Cisco deployments and lack dedicated operations expertise — they may never know they were breached. Cisco's stock dropped approximately 2.12% on the day the news broke.
CVSS (Common Vulnerability Scoring System) is the industry-standard framework for quantifying vulnerability severity, scored out of 10. The score is calculated across multiple dimensions: attack vector, attack complexity, required privileges, user interaction, and the impact on confidentiality, integrity, and availability. A score of 9.8 falls in the highest tier of the "Critical" rating, indicating the vulnerability can be triggered remotely over the network, requires virtually no user interaction, and has an extremely broad impact.
"Input sanitization" refers to the process of filtering, escaping, or validating external data before a program processes it, preventing that data from being interpreted as executable instructions. Lack of sanitization is the root cause of injection-class vulnerabilities — including SQL injection, command injection, and code injection. For a security appliance specifically designed to parse third-party email content, feeding arbitrary external input into an execution environment without validation is a fundamental design failure — made all the more ironic given that identifying and blocking malicious content is this device's core purpose.
Final Thoughts
This episode weaves together hardware frontiers, infrastructure controversies, and cybersecurity into a portrait of three defining tensions in today's tech industry: the relentless push past physical limits in compute density, the fierce conflict between AI expansion and energy sustainability, and the dark irony of security defenses becoming attack surfaces themselves. From a memory module priced like a luxury car, to data centers doubling their natural gas footprint, to a Cisco appliance that can be compromised by reading its own mail — these seemingly disparate stories all point toward the same reality: a technology ecosystem expanding at breakneck speed, riddled with hidden risks at every layer.
Related articles
Transitioning from Traditional Development to LLM Application Development: Avoiding the Three Hurdles 90% of Courses Don't Teach
Traditional backend developers transitioning to LLM application development face three real hurdles—model capability boundaries, requirement judgment, and effect evaluation—not math. This article breaks down the core engineering skills 90% of courses don't teach and offers a practical transition path.
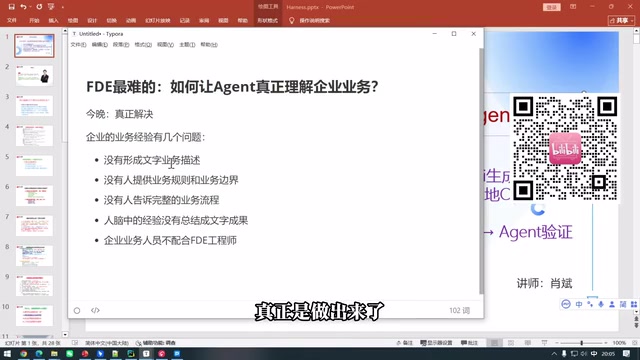
LLM WIKI in Practice: Making Agents Truly Understand Enterprise Business — Building a Troubleshooting Agent from Scratch
Inaccurate agent responses stem from a lack of business understanding. Based on a real order customer service troubleshooting agent case, this article explains how LLM WIKI builds a business knowledge base from codebases, uses incremental updates, and connects to agents via MCP server to achieve business understanding and troubleshooting with zero documentation.
A Computer Science PhD's Take: AI Career Planning for New Graduates — Algorithm vs. Application Development
A CS PhD advises new graduates on AI careers: try algorithm roles first but don't fixate; application development has more openings. Focus on LLM fine-tuning/deployment and agent frameworks (MetaGPT, LangChain), and watch AI + industry implementation to broaden job paths.