Apple Tightens macOS Disk Access Controls — and Exposes a Deeper AI Agent Security Problem
Apple's macOS permission tightening is a warning shot — the real problem is unchecked AI agent access inside enterprise systems.
Apple is tightening macOS Full Disk Access controls after AI agents began broadly requesting and obtaining file system permissions across devices. This platform-level move exposes a deeper issue: in enterprise environments, agents can gain persistent access to databases, internal APIs, and sensitive document stores simply by registering a tool — with no per-invocation contextual approval. The core flaw in current security models is "run first, log later" — agents act, data moves, and audit logs fill after the fact, often after exfiltration has already occurred. For enterprise teams, the priority is shifting permission logic from registration-based standing access to runtime contextual control, while first establishing full visibility into what systems agents can actually reach.
Why Apple Is Changing System Permissions for AI Agents
Apple has confirmed it will tighten macOS Full Disk Access controls. The trigger isn't traditional malware — it's the growing prevalence of AI agents requesting, and actually receiving, broad access to the entire file system across a device.
This is a meaningful signal. When a platform vendor pushes a system-level change to address a specific class of problem, it means that problem has graduated from edge case to mainstream risk. Apple is making it clear: how AI agents access data is now a problem worth solving at the operating system level.
The Blind Spot Beyond Endpoint Protection
Apple's system-level guardrail protects endpoints. It does not protect enterprise infrastructure. That distinction is critical.
In enterprise environments, agent behavior is far more complex than on a personal machine. Agents invoke databases, hit internal APIs, and read sensitive document repositories at runtime. The issue lies in how access gets granted — access is permitted because a tool has been registered in the system, not because a specific person approved a specific call in a specific context.
In other words, once a tool is registered, the agent holds a standing pass to invoke it. It doesn't need to ask each time, and no one is in a position to judge in real time whether any given invocation is actually appropriate.
Full Disk Access is a fine-grained permission control mechanism introduced in macOS Mojave (10.14). It requires applications to obtain explicit user authorization — via System Settings → Privacy & Security — before accessing sensitive locations such as the Desktop, Documents, Downloads, and third-party cloud storage. It was designed to prevent malware from silently reading local data. However, its protection boundary ends at the local file system. It has no visibility into cross-system access initiated through network protocols such as REST APIs, gRPC, or JDBC — which happen to be the primary data access paths for AI agents in enterprise environments. The macOS-level tightening is meaningful protection for individual users, but for enterprise IT administrators it reads more like a prompt: the access chain beyond the local endpoint requires an entirely different control framework.
The "Run First, Log Later" Risk Chain
The original reporting captures the problem in one concise line: The agent runs. The data moves. The log fills afterward.
This cuts to the fundamental flaw in current agent security models. Traditional audit logs are a post-hoc mechanism — they record what already happened, but cannot intercept or approve actions before they occur. For conventional software, this is an acceptable tradeoff. For AI agents capable of making autonomous decisions and invoking large volumes of system resources, it means:
- Agents gradually accumulate access privileges with no explicit authorization from any administrator;
- By the time someone reviews the logs, the data has often already been read, moved, or exfiltrated;
- Permission expansion is silent — it compounds quietly across enterprise deployments until an incident finally surfaces it.
Apple's adjustment brings this slow-burn, accumulative problem into plain view.
This dynamic is classified in security as Permission Creep — the gradual accumulation of access rights beyond what is actually needed, typically without periodic review or revocation. In traditional software contexts, permission creep tends to be the result of human error and evolves slowly. AI agents' autonomy dramatically accelerates the process: as agents traverse task chains, they actively discover and invoke new tools and interfaces, and each successful invocation can become hardcoded as "available by default" within the runtime environment. Prompt Injection attacks amplify the risk further: adversaries can embed malicious instructions in external content the agent processes — emails, web pages, documents — and direct the agent to perform unintended actions using its existing permissions. Together, these two risks transform the "run first, log later" model from inefficient to genuinely dangerous in agentic contexts.
What This Means for Enterprise Agent Deployments
For teams already running agents against internal systems in production, this is a moment worth pausing to examine. Several core questions come into focus.
Permission Grants Should Be Context-Driven, Not Registration-Driven
The fundamental problem with the current model is treating "tool is available" as equivalent to "invocation is approved." A more defensible direction is introducing runtime contextual judgment — should the same database tool receive the same level of access across different tasks and different data sensitivity levels?
Shift from Post-Hoc Auditing to Real-Time Control
Logs should not exist solely as forensic artifacts. They need to connect to real-time access decisions. In an ideal state, high-sensitivity invocations should trigger human approval or policy-based interception — not leave a trace in a log after the data has already moved.
One emerging architectural approach for runtime access control is the introduction of an Agent Gateway or Policy Enforcement Point (PEP) — an interception layer inserted between an agent's tool call and the actual system response, which dynamically decides whether to allow, downgrade, or route for human approval based on predefined policies (data classification level, call frequency, task context, user identity). This aligns closely with the core principles of Zero Trust Network Access (ZTNA): never trust by default, verify every access. Some AI security vendors and internal engineering teams are beginning to build this kind of interception logic on top of the tool-calling layer in frameworks like LangChain and AutoGen — but standardization remains low, and mature enterprise-grade products are still some distance away. For teams operating today, even adding a single human confirmation step before high-sensitivity tool invocations is meaningfully more effective at compressing the risk window than relying purely on after-the-fact logs.
Visibility Before Governance
Many enterprises cannot fully answer the question: "What systems can our agents actually access right now?" Before any governance conversation can happen, establishing complete visibility into the agent access surface is a prerequisite that cannot be skipped.
Closing: The Platform Change Is Just the Beginning
Apple tightening macOS disk access permissions is a warning signal, not a complete solution. It protects individual endpoints while leaving a much larger problem in sharp relief — the unchecked expansion of agent permissions inside enterprise infrastructure.
For organizations running agents against internal systems, the real question isn't "what did Apple do?" It's "what is the actual state of our own access controls, and which gaps have we still not closed?" As agents push deeper into production environments, permission governance is going to become one of the unavoidable hard problems in AI deployment.
Related articles
Anthropic IPO Countdown: The Compute Cost Ledger Behind a $2 Trillion Valuation
Anthropic's IPO targets up to $2 trillion — double its Series H valuation. We break down the timeline, compute cost logic, and the key question investor day must answer.
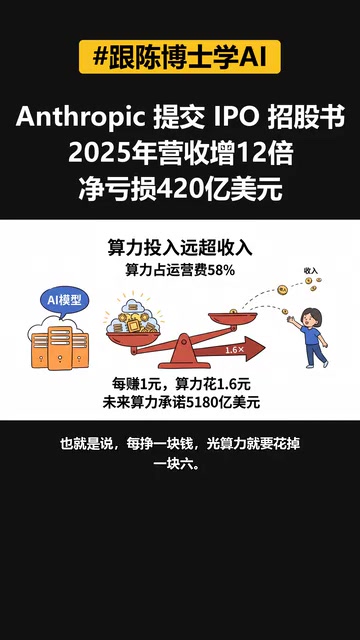
Anthropic IPO Prospectus Revealed: Behind 12x Revenue Growth, the Twin Tests of Compute Costs and Customer Concentration
Anthropic filed its IPO prospectus: 2025 revenue up 12x to $4.6B, net loss $42B including $34B non-cash. Breaking down compute costs, $2T valuation logic, customer concentration risks, and founder control.
Xteink X4 Pro Review: A Mini E-Reader That Fits in Your Pocket, Now More Affordable
Xteink X4 Pro is a 4.26-inch mini e-reader, smaller and thinner than a 6-inch Kindle, magnetically attachable to phones, and cheaper than ever. We analyze its screen, design, use cases, and value.