Build a Commercial App with Stripe Payments for Free Using Google AI Studio + Firebase

A free AI app framework that standardizes Firebase backend, role permissions, and Stripe payments for non-technical builders.
A developer has wrapped Google AI Studio and Firebase into a free template framework that addresses three common pain points of AI low-code tools: missing backends, permission vulnerabilities, and complex payment integration. The framework guides users through Firebase initialization, auto-generated Firestore security rules, multiple login methods, and one-click Stripe payment setup. Its role permission system supports granular control, and a linked pages feature keeps store and product data in real-time sync. The core breakthrough is standardizing security rules, permissions, and payments — the highest technical barriers — so non-technical founders can launch real commercial apps fast.
Google AI Studio combined with Firebase makes it possible for anyone — even without a technical background — to build a fully functional commercial application. The catch, however, is that without understanding the technical details, you'll often end up with a half-finished product full of errors, no real backend, and no security mechanisms. One developer tackled this pain point by wrapping Google AI Studio into an AI application-building framework that anyone can use, released as a free template. This article walks through the complete workflow and core capabilities of this solution.
What This Framework Can Do
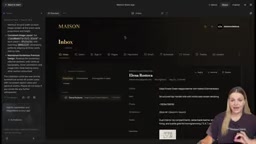
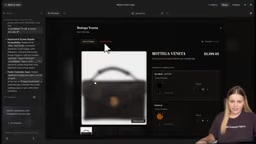
This is no simple toy demo. The developer built a complete example — a "luxury goods online store + order fulfillment center" — to showcase it: customers can browse products, fill out custom order forms, add items to a cart, and check out via Stripe. The admin side includes product management, inventory sync, transaction records, and order fulfillment capabilities.
The system covers the major modules any real commercial application needs:
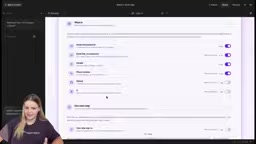
- Multiple login methods: Email/password, Magic Link, Google, GitHub, X, phone number, anonymous login, and even multi-factor authentication (MFA) — all toggled on with a switch.
- Theme and brand customization: Upload a logo and favicon, describe your desired visual style in natural language, and get a design prompt for Gemini to execute.
- User and role management: Assign users as team members, admins, or custom roles (e.g., customers, suppliers), and precisely control which tabs each role can see and what actions they can perform.
- Forms and notification system: Customize forms to collect customer information; when submitted, a notification bell in the admin dashboard alerts you in real time, with all data viewable in an inbox.
Complete Firebase Configuration in Five Minutes
The critical hurdle in the entire setup is initializing the Firebase project — and this framework breaks it down into a step-by-step guide anyone can follow.
The process goes roughly like this: create a new project in Firebase and add a Web App, grab the Firebase SDK configuration, then enter values like API Key, Auth Domain, Project ID, App ID, and Messaging Sender ID one by one into the environment variables (Secrets) in Google AI Studio. The Storage Bucket field gets filled in after the storage service is set up.
Next comes database and security rules configuration. Create a Firestore database in Firebase, keeping the default production mode settings; then go back to the framework's setup page, enter your admin email, and generate security rules with one click. Copy and paste them into Firestore's Rules tab and publish. This step is essentially configuring the entire application's backend permission system — for non-technical users, this is usually the most error-prone and most dangerous step, and the framework simplifies it by auto-generating the rules.
Finally, create Cloud Storage (requires linking a Google Cloud billing account), paste in the generated storage rules and publish them, then paste the Storage Bucket address back into the AI Studio variable and click Apply. That completes the full configuration.
Firebase is Google's Backend-as-a-Service (BaaS) platform, providing developers with a complete backend infrastructure: a database (Firestore), user authentication, file storage (Cloud Storage), cloud functions, and more. For non-technical users, its biggest advantage is that you don't need to build or maintain your own servers — all data reads/writes and user authentication are hosted by Google. Firestore is its core database, using a document-collection structure and defining read/write permissions through "Security Rules" — this rules file is essentially the entire application's permission firewall. Misconfigured security rules (for example, the default test mode allows anyone to freely read and write all data) can lead to data leaks or, worse, malicious writes that rack up huge bills. This is precisely the core value of the framework's auto-generated security rules.
Authentication and Role Permissions: The Heart of a Real Backend
Login method configuration is quite flexible. The developer specifically demonstrated phone number login, which has been highly requested: after enabling the Phone provider in Firebase Authentication, you must go into SMS policy and individually check each country you want to allow logins from — otherwise it won't work. Once enabled, a "Continue with phone number" option appears on the registration page, and users can sign up after receiving a verification code.
Role management is where this framework really shines. Any logged-in user is a Member by default, and admins can promote them to team member, admin, or a custom role. Roles directly determine which tabs a user can access. When creating a page, the system asks three key questions: who can access this page, what access mode to use (a shared page where everyone collaborates / a private page where each person only sees their own data / a mix of both), and "who can do what" — granular enough that team members can only add and edit while only admins can delete records, with an automatic operation history log tracking every change and who made it.
This level of granular permission control is exactly what separates "a usable commercial application" from "a half-finished product full of security holes."
Page Generation and Stripe Payment Integration
Page creation uses a "describe to generate" model. Users describe the landing page structure they want under the pages tab (e.g., a Hero section, product display area, custom order form, CTA section), upload any needed images and files, and the framework generates a complete prompt to paste into a Gemini conversation for automatic page construction.
The "Linked Pages" feature is worth highlighting: by linking the store page to the product page, Gemini ensures both stay in sync in real time — when products are added, removed, or have their inventory modified on the product page, the store page updates automatically; when a purchase is completed on the store page, inventory on the product page is decremented accordingly. This avoids the common AI generation problems of duplicate pages and data inconsistencies.
Payment integration is simplified to just one key. Switch to Sandbox (test mode) in the Stripe dashboard, create a sandbox account, and copy the Secret Key into AI Studio's Secrets variable (name it stripe secret key, making sure the key contains the word test to avoid charging real money). The framework supports three payment types: dynamic payments (automatically calculates the total from the cart and generates a payment link, ideal for checkout), one-time fixed payments, and subscriptions.
In the example, after a buyer adds items to the cart the system automatically calculates the total, the buyer fills in shipping information (with address autocomplete), is redirected to Stripe to complete payment using test card number 4242 4242 4242 4242, and is then directed back to the dashboard where they need to verify their email. The developer specifically built in "automatic account creation upon payment" to prevent order data loss, and the admin side also receives a notification for each new transaction.
Stripe is the most widely used online payment infrastructure in the developer ecosystem, supporting credit cards, debit cards, and a variety of local payment methods. Its Sandbox mode provides a complete testing environment: test card number
4242 4242 4242 4242is Stripe's standard test card from their official documentation — fill in any future expiration date and CVC to simulate a successful payment, with no real charges at any point. Secret Keys come in two forms: test keys (starting withsk_test_) and live keys (starting withsk_live_) — these must never be mixed up, which is why the framework requires the key to contain the wordtest. Before going live, you'll also need to complete business verification and link a bank account in the Stripe dashboard to receive real payments.
Assessment and Limitations
The value of this solution lies in turning Firebase's backend complexity, permission security, and Stripe payment integration into a replicable workflow, allowing small merchants or independent entrepreneurs to launch an application with a real backend in a short amount of time. With the Debugging Log feature, users can also copy any AI-generated errors directly to Gemini for fixes.
A few things to keep in mind: the preview feature currently only works reliably in Chrome; pages often need a hard refresh after changes; the Storage service requires linking a Google Cloud billing account; and the entire workflow is heavily dependent on the Firebase and Google AI Studio ecosystem, creating platform lock-in risk. For applications truly going to production, you'll also need to swap test keys for live keys, update authorized domains, and more.
Overall, this is an attempt to push "AI low-code" from the demo level to something genuinely practical. The core breakthrough isn't that AI can generate pages — it's that the hardest parts, security rules, role permissions, and payments, have been standardized.
Related articles

Gaussian Process Bandit Optimization: Exploration Strategies and Inference Regret Guarantees
Cumulative regret guarantees in Bayesian optimization fail to reflect final recommendation quality. This article examines a new study that provides inference regret guarantees for Gaussian process bandit optimization through exploration query strategies and fill distance analysis, validated on hyperparameter optimization and control tasks.

The Most Detailed Codex Guide on Bilibili: From Installation to Real-World Practice
The most detailed Codex guide on Bilibili: from app store installation to daily work mode configuration, with a real coffee shop project demonstrating file organization, data extraction, dashboard creation, and other practical tasks. Learn to use Plan Mode and desktop pets to leverage Codex efficiently.

Appearance Compensation in Volume Rendering: Why RGB Accuracy Cannot Guarantee Density Correctness
Volume rendering research reveals that volumetric data perfectly reproducing external RGB views may still contain density errors: appearance compensation can double central density and keep external rays unchanged even when L2 error exceeds 14.52%. Density recovery depends on appearance capacity, spatial resolution, and measurement design.