Claude Compliance API Launch: Integrating 28 Security Vendors for Comprehensive Enterprise AI Compliance Management

Claude launches Compliance API integrating 28 security vendors for enterprise AI governance.
In May 2025, Anthropic released the Claude Compliance API, integrating with 28 leading security and compliance vendors to enable enterprises to govern Claude like any other application. The API provides two core capabilities—conversation content access and activity event auditing—supporting DLP policy extension and compliance framework requirements including SOC 2, GDPR, and HIPAA, covering full-stack security scenarios from data loss prevention to network security and security operations.
Overview
On May 21, 2025, Anthropic announced that Claude now officially offers integrations with 28 well-known security and compliance tools. This means enterprise IT and security teams can now govern and manage Claude's compliance just like any other enterprise application.
As AI tools become deeply embedded in enterprise workflows, how to incorporate them into existing security management frameworks has become one of the top concerns for CIOs and CISOs. The Claude Compliance API released by Anthropic is a direct response to this need.
Core Capabilities of the Claude Compliance API
All 28 integrations are built on the Claude Compliance API. From a technical architecture perspective, the core challenge of enterprise AI governance lies in the fact that traditional security tools are designed around structured data flows and deterministic behaviors, while AI conversational systems generate unstructured, highly dynamic data streams. The Claude Compliance API addresses this by providing standardized programmatic interfaces that transform AI system behavioral data into formats that security tools can understand and process—typically using RESTful architecture while supporting both real-time streaming and batch historical queries to accommodate the latency requirements of different security scenarios. The API provides enterprise security and compliance teams with programmatic access to two categories of data.
Conversation Content Access and DLP Policy Extension
Security teams can access conversation content within Claude Enterprise, including chat histories, uploaded files, and project data. Administrators can seamlessly extend their existing security monitoring and Data Loss Prevention (DLP) policies to cover Claude usage scenarios.
Data Loss Prevention (DLP) is a category of security technology that prevents unauthorized leakage of sensitive data through content detection and policy enforcement. Traditional DLP systems identify sensitive content using regular expressions, keyword matching, file fingerprinting, and machine learning classifiers, implementing controls at three stages: data in transit, at rest, and in use. However, AI conversation scenarios present entirely new challenges for DLP: users may bypass pattern-matching-based detection through natural language descriptions, segmented inputs, or semantic transformations; AI model outputs may also inadvertently synthesize information from multiple sources, creating new sensitive content. Therefore, connecting Claude conversation data to modern DLP platforms requires these platforms to have the ability to understand conversational context, not merely scan individual messages. SASE (Secure Access Service Edge) architecture further integrates DLP capabilities with network access control, enforcing policies uniformly in the cloud—particularly important for enterprises with distributed workforces.
The data security policies that enterprises apply to email, instant messaging, and other tools can now equally cover AI conversations—this is critical for industries with stringent data compliance requirements such as finance, healthcare, and legal.
Activity Event Auditing and Compliance Reporting
The API also provides activity event data from Claude Enterprise and Claude Platform, covering user logins, administrator actions, and configuration changes. Security teams gain a unified view for comprehensive visibility into how Claude is being used across the organization.
This audit capability is indispensable for meeting compliance framework requirements such as SOC 2, GDPR, and HIPAA. Each of these three frameworks has specific requirements for AI tools: SOC 2 requires demonstrating the integrity of audit logs and the effectiveness of access controls; GDPR requires enterprises to track personal data processing activities and notify regulators within 72 hours of a data breach; HIPAA requires maintaining complete logs of all access to Protected Health Information (PHI) and signing dedicated agreements with business associates. The audit data provided by the Claude Compliance API is the critical technical foundation for meeting all three framework requirements, and also provides the foundational data support for security incident investigation and traceability.
28 Partners Covering Full-Stack Security Scenarios
The 28 integrated security and compliance vendors cover all critical areas of enterprise security.
Data Loss Prevention and Network Security
- DLP/SASE: Zscaler, Netskope, Forcepoint, Fortinet, Palo Alto Networks
- Data Security: Cyera, Varonis, Microsoft Purview, IBM Guardium
- Network Security Platforms: Cloudflare, CrowdStrike, Trellix
Security Operations and Observability
Security Information and Event Management (SIEM) systems are the core infrastructure of modern enterprise Security Operations Centers (SOC). SIEM aggregates log data from network devices, servers, applications, and security tools, using correlation rules and machine learning algorithms to identify anomalous behavior.
Related articles
Meta Muse Hits 900K Downloads in Six D…
Meta Muse Hits 900K Downloads in Six Days: The AI Agent Era Has Officially Arrived
Meta's AI agent Muse hit 902K downloads in 6 days, topping US App Store and Google Play charts above ChatGPT and Claude. A deep dive into Muse's capabilities and the AI Agent race.
 Industry Insights
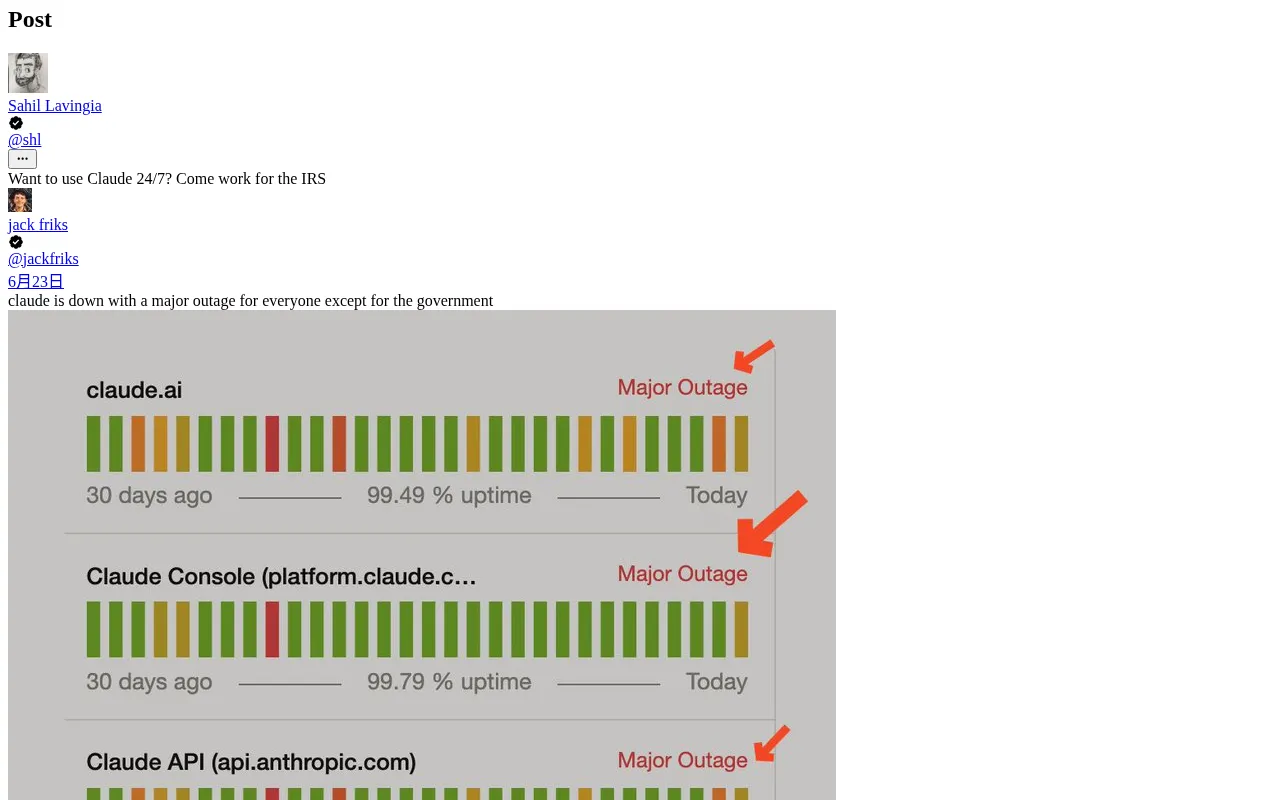
IRS Fully Embraces Claude AI, Accelerating Federal Government's AI Adoption
The IRS is recruiting staff with 24/7 Claude AI access, marking Anthropic's breakthrough into the federal government. Explore the strategic implications and tax use cases.
 Industry Insights
The IRS Mobile App Debate: A Trust Crisis in Government Digital Transformation
The IRS's proposed mobile app has sparked heated debate. This article analyzes the core arguments, exploring data security, privacy, and the trust crisis in government digital transformation.