Cursor Official Plugin Swapped: Claude Code Extension Hid an SSH Backdoor

Cursor's marketplace Claude Code plugin was swapped for a malicious version for about 11 hours, affecting up to 5,000 developers.
The article reviews a supply chain attack in Cursor's extension marketplace: a Claude Code extension with a credible publisher name was replaced by a tampered version for about 11 hours, potentially affecting up to 5,000 developers. The malicious code executed automatically on editor load, harvesting host info and secrets, planting an SSH public key disguised as SBC Telemetry, and attempting a reverse tunnel with persistence. Uninstalling is not enough, and real publisher names defeat traditional trust checks.
The security boundary of AI coding tools may be more fragile than we imagine. A recent supply chain attack in the Cursor editor extension marketplace has sounded an alarm for all developers who rely on AI-assisted coding: a Claude Code extension distributed by the official store, with an impeccable publisher name, was replaced with a malicious version in just about 11 hours, quietly planting an SSH backdoor on developers' machines and potentially affecting as many as 5,000 people.
Incident Recap: A "Fake Auntie" Supply Chain Attack
According to a breakdown by a Bilibili creator in a video, the incident occurred from just after 2 AM to 1:30 PM Pacific Time on October 29, when the Claude Code extension in Cursor's own extension marketplace was replaced with a tampered version for about 11 hours. Cursor's official notice confirmed that this malicious version was not developed by Anthropic.
The creator used a vivid analogy to explain the attack logic: you book a highly rated auntie on a housekeeping platform, her badge, company, and photo all check out, and you let her in—she can then move around your home, look through files, and run commands. That is how a normal plugin works. But during those 11 hours, the platform sent a fake auntie wearing a real badge, and she did not wait for your instructions—she started acting the moment she entered.
Security firm Foreign (mentioned in the article) found that the code executes automatically as soon as the editor loads the malicious file, with no interaction with Claude required from the user.
What the Malicious Code Did: Copy the Inventory, Cut a Key, Dig a Tunnel
According to the creator's analysis, the fake extension performed three steps, each aimed at long-term control.
Step 1: Environmental Reconnaissance and Data Exfiltration
After starting, the malicious code first "copies the inventory": it collects the hostname, username, OS type, Gate email, public IP, and other information and sends it out. More covertly, it scans up to more than 40 tags in the user's environment variables, specifically filtering entries with names resembling keys, tokens, passwords, and cloud accounts. The cabinet was not opened and the money was not taken, but the attacker now knows exactly which drawer holds the passbook.
Step 2: Planting an SSH Authorization Backdoor
Next, it adds an attacker's public key to the user's SSH authorization list—equivalent to secretly cutting a copy of a key on your key rack. This key even carries a disguised label—SBC Telemetry, meaning "service telemetry," which sounds no different from legitimate software.
SSH (Secure Shell) is the most commonly used encrypted protocol for developers to log in to servers remotely and transfer code. Its authentication relies on key pairs: the public key is stored in the server's ~/.ssh/authorized_keys file, while the private key stays local. As long as a public key appears in the authorization list, whoever holds the corresponding private key can log in as that user without entering a password. Therefore, writing an attacker's public key into authorized_keys is equivalent to opening a permanent passwordless entry for the attacker, and it will not trigger any login alert. Attackers often disguise the comment field of a public key as a system component name (such as SBC Telemetry in this case), so that victims mistake it for a normal configuration when viewing the file. When investigating, check the comments and fingerprints one by one rather than just looking at the file name.
Step 3: Establishing a Reverse Tunnel and Persistence
The malicious code also attempts to open a reverse tunnel from the user's machine to the attacker's server. If it fails, it retries every 60 seconds. At the same time, it sets up persistence mechanisms: on Mac it uses a name similar to a built-in Apple system service, and on Windows it creates a scheduled task named Sysmon, ensuring survival after a computer restart.
The creator pointed out that the good news is that in most cases this tunnel failed to open, because enabling the SSH service requires administrator privileges, and the malicious code itself contained coding errors, so this step got stuck. But the key has been hung, the alarm has been set, and the inventory has been mailed out—the risk is not eliminated.
A reverse tunnel is a channel in which an internal machine actively initiates a connection to an external server and then turns that connection into a bidirectional forwarding channel (commonly implemented with SSH's -R parameter or similar tools). Unlike direct inbound connections from outside, reverse tunnels exploit the almost never-blocked characteristic that internal machines are "allowed to make outbound connections," so malicious code often uses them to bypass perimeter defenses and expose internal services to attackers. In this case, the tunnel required the target machine to enable the SSH service, which usually requires administrator privileges, and the code itself had flaws, so in most cases it failed to open—one of the key reasons the damage in this incident was relatively limited.
Persistence is a standard part of the attack chain, intended to keep malicious code alive after the process ends, the machine restarts, or the user uninstalls the original carrier. Common methods include writing system scheduled tasks (Windows Task Scheduler, Linux cron), registering as a system service (macOS launchd, Windows Service), and modifying startup items or shell configuration files. In this case, on macOS it borrowed a name similar to a built-in system service, and on Windows it created a scheduled task named Sysmon—Sysmon is a common name for Microsoft's official system monitoring tool, which reduces the chance of manual detection. This also explains why "uninstalling the extension" does not equal cleaning it up: scheduled tasks exist independently of the extension and must be deleted separately.
Cleanup Challenges and Official Response
One easily overlooked detail: uninstalling the extension does not mean it is cleaned up. Cursor's official wording was that uninstalling the extension alone may not be enough, because the scripts it leaves behind may continue to run after uninstallation. The scheduled task was set before the malicious code left; the person is gone, but the alarm still rings.
After the incident was discovered, Cursor first took down the malicious extension, then shut down the entire extension marketplace, replaced keys, and rebuilt before going back online. The attacker's server was also taken down. Anthropic said its systems were not hacked and that versions from official channels are unaffected, with only Cursor users impacted. But how the fake got into the platform has still not been explained by either company.
What Is Truly Alarming: The Publisher Name Is Real
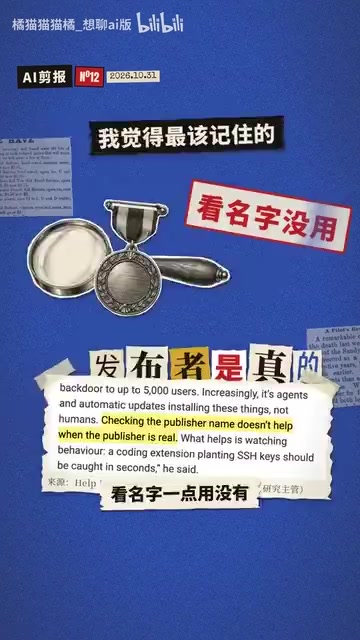
The creator particularly emphasized a security researcher's view: this time there was no "impersonation" at all—the publisher was real, and looking at the name was completely useless. This means the traditional security intuition of "check whether the publisher is trustworthy" fails in the face of supply chain attacks.
The deeper hidden danger lies in the shift in distribution methods. Installing and updating plugins now increasingly relies on automatic updates and AI agents, with no one watching. A coding plugin suddenly inserting an SSH key into a computer should have been caught within seconds, but the reality is that it survived for 11 hours.
What to Do If You Have Used Cursor
The creator gave specific advice: if you installed or updated the Claude Code extension around October 29, check whether the name SBC Telemetry exists in your SSH authorization list. Cursor's official website provides a one-line check command and a cleanup script. If anomalies are found, besides cleaning up, you should use another clean computer to change every password and token you can.
Developers who have not used Cursor should also self-check: how many extensions are installed in the editor, and how many have automatic updates enabled. Today, as AI tools are deeply embedded in development workflows, supply chain security is no longer a distant topic.
One-line Summary
Curson's extension marketplace Claude Code plugin was replaced with a malicious version for about 11 hours, affecting up to 5,000 developers.
Paragraph Summary
The article reviews a supply chain attack in the Cursor extension marketplace: from early morning to afternoon Pacific Time on October 29, a Claude Code extension with a credible publisher name was replaced with a tampered version for about 11 hours, potentially affecting as many as 5,000 developers. The malicious code executes automatically when the editor loads, first collecting host information and scanning environment variables for keys and tokens, then planting a public key disguised as SBC Telemetry into the SSH authorization list, and finally attempting to establish a reverse tunnel and set up persistence. Because the tunnel required administrator privileges and the code had flaws, it mostly failed to open, but credentials had already leaked and a backdoor had been planted. The article emphasizes that uninstalling the extension is not enough to clean up, that real publisher names defeat traditional judgment, and that automatic updates and AI agent distribution further amplify the risk, and it provides inspection and cleanup recommendations.
Related articles

Former Plaid CTO Shut Down a Profitable Business to Bet on an AI New Species in One Month
Former Plaid CTO Glez shut down his $1M+ tax filing company and pivoted in one month to Town, an email and calendar agent. This article breaks down his views on customers vs. users, model neutrality, data ownership, and agent traffic.

AI Automated Vulnerability Discovery Tutorial: A Beginner's Path from Agent Building to SRC Practice
A beginner-friendly breakdown of an AI automated vulnerability discovery course: from Agent building and vulnerability principles to CVE reproduction and SRC hunting practice, with a four-stage learning path.

WorkBuddy in Practice: Your Advancement Map from AI Agents to FDE
What is WorkBuddy? Based on the first lesson of a 256-episode Bilibili tutorial, this article breaks down the four-layer relationship among large models, Harness, agents, and WorkBuddy, outlines the path from basic operations to FDE engineer, and analyzes monetization logic and learning resources.