Deutsche Bank Internal Platform Exposed: A Technical Architecture and Digital Strategy Analysis

Deutsche Bank's internal website was accidentally made public, sparking discussion about security and digitalization in financial enterprises.
Deutsche Bank's internal information portal Inside Deutsche Bank (inside-db.com) was accidentally made publicly accessible, gaining 345 points and 126 comments on Hacker News. Starting from the incident, the article analyzes the knowledge management and collaboration functions that internal platforms may carry, as well as potential vulnerabilities in the financial industry regarding access control, authentication and authorization, and security audits. It also points out that such internal platforms are important tools for banks' digital transformation, but open collaboration must advance in tandem with information security. The heated discussion in the tech community reflects both concern about security vulnerabilities and curiosity about the technical practices of large enterprises, providing an external reference for enterprises to improve their security strategies.
Introduction: The Accidental Exposure of a Bank's Internal Website
Recently, a website called Inside Deutsche Bank (inside-db.com) sparked widespread discussion on Hacker News, garnering 345 upvotes and 126 comments. The site appears to be Deutsche Bank's internal information portal, yet it was accidentally made publicly accessible. For tech professionals, this is not only a cautionary tale about corporate security but also a window into how traditional financial institutions build their technical architecture and advance their digital transformation.
Hacker News is a tech community operated by the venture capital firm Y Combinator, organizing content through user-submitted links and community-voted rankings, with a discussion section known for its technical depth and high density of industry practitioners. The number of upvotes a post receives reflects community interest, while the comment count often indicates controversy or informational value. For enterprises, having an internal system publicly discussed on Hacker News usually means two things: first, the exposure surface has entered public view; second, community members with security backgrounds may be conducting passive or active probing of the system. Therefore, the appearance of such posts can itself be regarded as an external security signal, and enterprise security teams should incorporate it into their threat intelligence monitoring scope.
Website Content: Internal Information Made Publicly Visible
Although the specific content of the website was not fully captured, judging from the discussion heat on Hacker News, Inside DB likely contains Deutsche Bank's internal news, technical documentation, organizational structure, or employee resources. Such internal platforms typically carry the enterprise's knowledge management and collaboration functions, and their accidental exposure may involve sensitive information leakage. In the financial industry, data security and compliance are of paramount importance, and any external exposure of internal systems may trigger regulatory scrutiny.
Speculation on Technical Architecture and Takeaways
Judging from the public URL structure, Inside DB may be built on a common web technology stack, such as a content management system or a custom portal. The technical architecture of the financial industry often emphasizes security, high availability, and compliance, but this incident exposed potential vulnerabilities in the enterprise's access control. For developers, this is a reminder that strict authentication and authorization mechanisms must be implemented when designing internal systems, along with regular security audits.
Authentication and authorization mechanisms are the two core lines of defense for internal system security. Authentication addresses the question of "who you are," with common methods including passwords, multi-factor authentication (MFA), and single sign-on (SSO); authorization addresses the question of "what you can do," typically implemented through role-based access control (RBAC) or attribute-based access control (ABAC) models. A common mistake in enterprise internal portals is that authentication mechanisms are deployed only at the application layer, while backend APIs, static resource directories, or backup files are not equally protected, allowing attackers to bypass frontend pages and access data directly. In addition, the principle of least privilege requires that each account have only the minimum access scope needed to fulfill its responsibilities, which is especially critical in financial institutions, as unauthorized access may directly reach customer data and trading systems.
Security audits are regular checks of a system's access control, logging, and configuration state, aimed at discovering and fixing vulnerabilities before they are exploited. Common practices include penetration testing, vulnerability scanning, access log review, and configuration baseline comparison. For portals serving internal employees, audits should pay particular attention to unauthorized public exposure surfaces, expired accounts, default passwords, and the enumerability of sensitive paths. Financial institutions typically must also meet regulatory requirements (such as operational risk management under the Basel Accords and data protection regulations like GDPR), so audit results often need to be archived and subject to internal and external compliance checks. Making audits routine and automated—rather than one-off campaign-style checks—is an effective way to reduce the probability of such exposure incidents.
The Tip of the Iceberg of Digital Transformation
As a major global financial institution, Deutsche Bank's digital transformation has always been a focus of industry attention. Internal platforms like Inside DB may be one of the core tools for employee collaboration and knowledge sharing. Through such platforms, the bank can integrate internal resources, improve communication efficiency, and foster a culture of innovation. However, this exposure also highlights that in the digitalization process, security culture and technical measures must be strengthened in tandem.
Community Reaction and Industry Impact
The comments on Hacker News (126) reflect the tech community's typical attitude toward such incidents: concern about security vulnerabilities on the one hand, and curiosity about the internal technical practices of large enterprises on the other. The discussion may involve speculation about the bank's technology stack, criticism of security practices, and suggestions for designing similar internal platforms. Such community feedback has reference value for enterprises looking to improve their security strategies.
Conclusion: Balancing Security and Openness
The exposure of Inside Deutsche Bank once again reminds us that in the wave of digital transformation, enterprises need to find a balance between open collaboration and information security. For financial institutions, the design of internal platforms should not only focus on functionality and user experience but also prioritize security protection. At the same time, the heated discussion in the tech community reflects continued attention to the technical practices of large enterprises, which helps drive the overall security level of the industry upward.
One-line Summary
Deutsche Bank's internal website was accidentally made public, sparking discussion about security and digitalization in financial enterprises.
Paragraph Summary
Deutsche Bank's internal information portal Inside Deutsche Bank (inside-db.com) was accidentally made publicly accessible, gaining 345 points and 126 comments on Hacker News. Starting from the incident, the article analyzes the knowledge management and collaboration functions that internal platforms may carry, as well as potential vulnerabilities in the financial industry regarding access control, authentication and authorization, and security audits. It also points out that such internal platforms are important tools for banks' digital transformation, but open collaboration must advance in tandem with information security. The heated discussion in the tech community reflects both concern about security vulnerabilities and curiosity about the technical practices of large enterprises, providing an external reference for enterprises to improve their security strategies.
Related articles
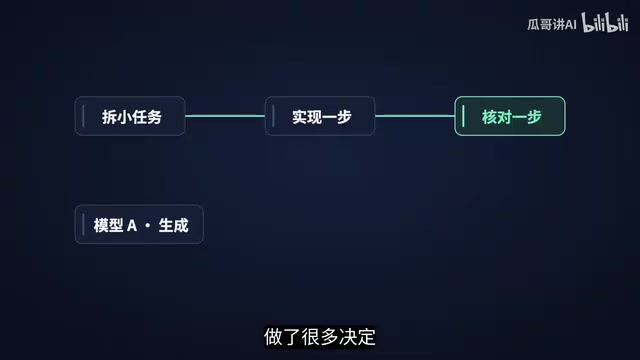
AI Code Generation Is Getting Cheaper—Validation Is the Real Challenge
Code generation is getting cheaper, and the bottleneck is shifting to validation. Drawing on Satya Nadella's interview, this piece analyzes coding agents' specifications, multi-model review, separation of permissions, organizational changes, and how engineers can turn a single fix into reusable team capability.
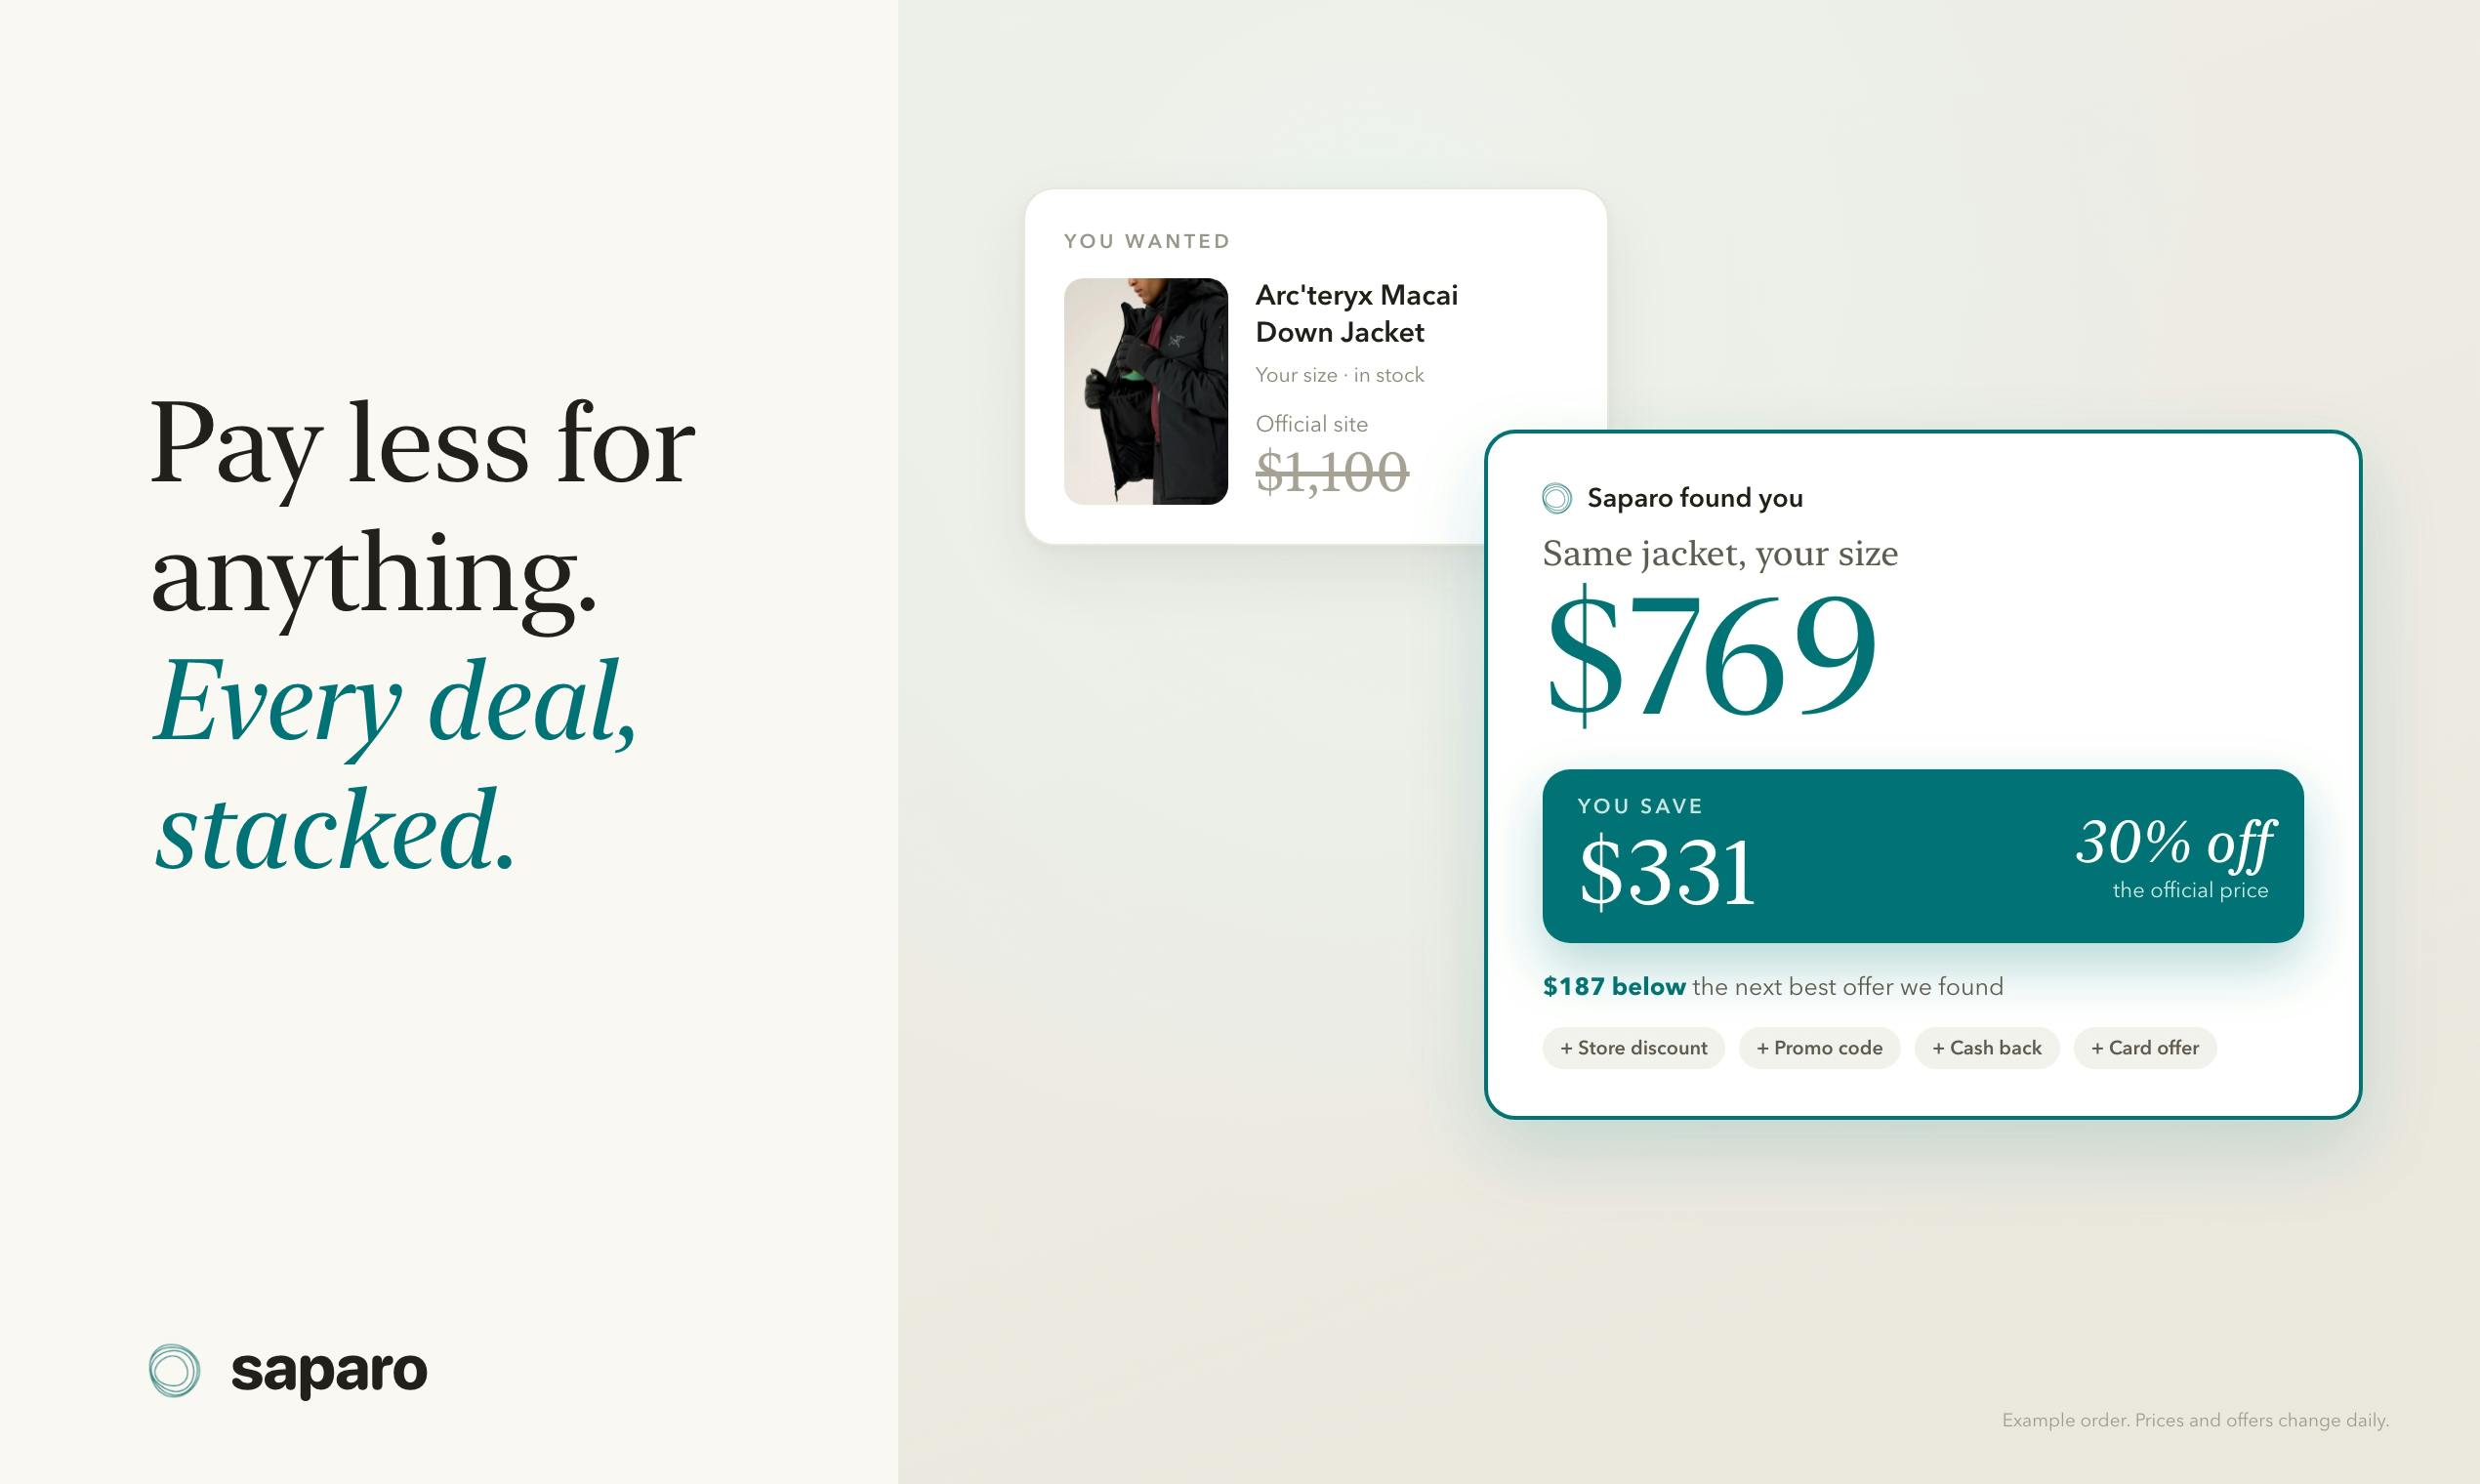
Saparo: The Shopping AI Agent That Stacks Discounts Automatically, Topping Product Hunt
Saparo is an AI shopping agent that automatically stacks discounts, topping Product Hunt. It finds the same item, matches sizes, combines promo codes and cashback, ranks by total cost including shipping and taxes, and leaves final payment to the user.

Tripmojo: The AI Travel Agent That Checks You In
Tripmojo is the #2 AI travel agent on Product Hunt: it syncs booking emails into a shared itinerary and lets Mojo attempt check-in, save boarding passes, and flag delays.