Free Interactive Course Launches: How to Learn AI Agent Governance

A free interactive course on Hacker News highlights the urgent need for AI Agent governance and its key implementation points.
The article begins with a free interactive AI agent governance course on Hacker News, noting that as agents move from demos to production, governance has become an unavoidable threshold. As agent capabilities expand from Q&A to multi-step planning, API calls, file modifications, and even transactions, the cost of loss of control rises significantly. External constraints such as least privilege, auditable operations, rollback on failure, and traceable responsibility are needed to make probabilistic systems predictable. The interactive course turns abstract governance principles into branching decision exercises and is suitable as a starting point for internal team training, though the post itself provides limited information and the course depth must be verified independently. The article also outlines three high-frequency gaps: overly broad permission grants, lack of human confirmation points, and logs that cannot reconstruct decision chains, noting that discussion on this topic is not very active, which indicates agent governance is still in an early stage.
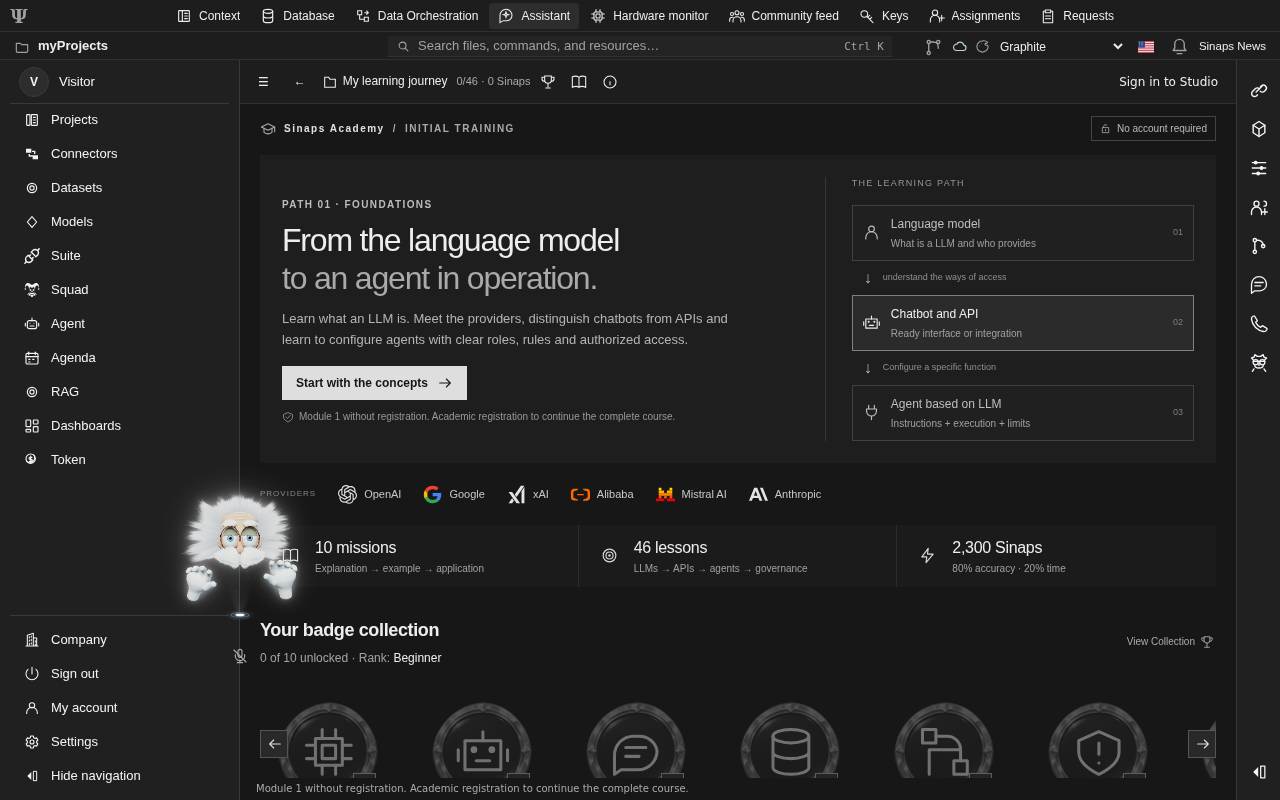
AI agents are moving from demos to production environments, and governance is becoming an unavoidable threshold. A Show HN post on Hacker News introduced a free interactive course on the topic of AI agent governance. The post itself contains very little information, but it points to a very real need: when agents begin autonomously calling tools, accessing data, and executing multi-step tasks, who defines the boundaries, and who bears the ultimate responsibility?
Why AI Agent Governance Has Suddenly Become a Necessity
Over the past year, the capability boundaries of agents have expanded rapidly: from single-turn Q&A to multi-step planning, from read-only information access to calling external APIs, modifying files, and initiating transactions. The stronger the capability, the higher the cost of loss of control. If an agent that can write code, deploy it, and roll it back on its own lacks properly scoped permissions, the impact of an error is far greater than that of a chatbot.
The core of governance is not to restrict capability, but to make capability predictable. This includes least privilege, auditable operations, rollback on failure, and traceable responsibility. These terms are not new in traditional IT governance, but applying them to models with probabilistic outputs is a completely different challenge—you cannot expect a system based on probabilistic generation to naturally follow rules; you can only frame it with external constraints.
This course chooses to take an interactive approach, indicating that the author believes this field requires hands-on practice rather than yet another white paper.
Least Privilege is a core principle in traditional information security, meaning that a subject should only possess the minimum set of permissions necessary to complete the current task, and permissions should be dynamically adjusted as tasks change. In AI agent scenarios, this principle is typically implemented by: defining clear role boundaries for each agent instance, restricting accessible resources through scoped credentials (such as short-lived tokens and fine-grained API keys), and triggering approval and logging each time permissions are expanded. Unlike traditional applications, agent behavior paths are probabilistic and not fully predictable, so permission design cannot be based solely on static configuration of "expected behavior"; it needs to combine runtime monitoring and automatic revocation mechanisms to form a "grant—monitor—revoke" loop.
Auditability refers to the system's ability to completely and credibly record who performed what operation on what resource and when, and to support post-hoc tracing and accountability. For AI agents, the difficulty of auditability lies in the multi-step nature of decision chains and the non-determinism of model outputs: recording only the final result is insufficient to reconstruct the root cause of a problem. It is usually necessary to simultaneously capture the sequence of tool calls, the input parameters and return results of each call, and the model's reasoning summary or confidence information. These records must also meet requirements for tamper resistance, long-term retention, and easy retrieval in order to support compliance reviews and incident post-mortems.
What the Interactive Course Format Solves
Governance topics are inherently dry; piling up rules, processes, and compliance clauses makes them hard to digest. The value of an interactive course lies in turning abstract principles into actionable branching decisions: given an agent scenario, you choose which permissions to grant, which checkpoints to set, and at which stage to introduce human review, and then immediately see the consequences.
According to the Hacker News post, this course is freely available and positioned as introductory learning material. For engineering teams building agent applications, such material is suitable as a starting point for internal training, enabling product or operations colleagues to understand the basic governance framework as well, rather than concentrating all judgment in the hands of a few architects.
It should be noted that the post only provides a basic introduction to the course and does not disclose the specific chapter structure, governance frameworks covered, or exercise formats. The actual depth of the content still needs to be verified by learners themselves.
Several Aspects Most Easily Overlooked in Governance Implementation
Based on industry discussions of agent systems, there are several high-frequency gaps in governance practice.
Overly Broad Permission Grants
To make agents "able to get work done," many teams tend to grant full permissions at once and add auditing afterward. The correct order should be reversed: by default, grant only the minimum permissions required to complete the current task, expand on demand, and leave a record for every expansion.
Lack of Human Confirmation Points
Not all operations require human intervention, but high-risk actions—sending externally, deleting data, incurring costs—should have clear confirmation gates. One of the values of course-style materials is helping you determine which actions are high-risk.
Human-in-the-Loop Checkpoint refers to preset nodes in an agent's execution flow that require explicit human approval before proceeding. The key to its design is risk tiering: low-risk operations can be automatically allowed, while high-risk operations (such as sending external messages, deleting or overwriting data, incurring actual costs, or changing production configurations) must be blocked and require confirmation. An effective confirmation checkpoint should also provide sufficient context—allowing the confirmer to see the specific action the agent is about to perform, the scope of data involved, and the potential impact, rather than just popping up an abstract "continue?" question.
Unusable Logs
An agent's decision chain is harder to reconstruct than that of a traditional program. If logs record only the final output, it is nearly impossible to locate the problem when something goes wrong. Governance requires recording intermediate steps, tool call parameters, and model reasoning summaries so that post-mortem reviews become possible.
Who Should Take This Course
This course is likely aimed at developers, technical leads, and compliance-related roles who are new to agent governance. If you are already running agents in production, the course may only provide a framework-level reference, and specific strategies still need to be designed in conjunction with your own system.
For teams still in the evaluation stage, this kind of free interactive material is a low-cost way to build consensus: first give the team a shared understanding of "what governance needs to manage," then discuss technical solutions. This is more efficient than arguing directly about implementation details.
The discussion on Hacker News is not very active, indicating that this topic is still in its early stages—few people are paying attention, but the problems that need to be solved are already accumulating.
One-line Summary
A free interactive course on Hacker News highlights the urgent need for AI Agent governance and its key implementation points.
Paragraph Summary
The article begins with a free interactive AI agent governance course on Hacker News and points out that as agents move from demos to production environments, governance has become an unavoidable threshold. Agent capabilities have expanded from single-turn Q&A to multi-step planning, API calls, file modifications, and even initiating transactions, significantly increasing the cost of loss of control. Therefore, external constraints such as least privilege, auditable operations, rollback on failure, and traceable responsibility are needed to make probabilistic systems predictable. The interactive course turns abstract governance principles into branching decision exercises and is suitable as a starting point for internal team training, but the post itself provides limited information, and the course depth needs to be verified independently. The article also outlines three high-frequency gaps: overly broad permission grants, lack of human confirmation points, and logs that cannot reconstruct decision chains. It notes that discussion on this topic is not very active, indicating that agent governance is still in an early stage.
Related articles

AI-Assisted React Development in Practice: Optimizing a Video App and Handling Errors
A 14-year veteran developer demonstrates AI-assisted React video app optimization: compressing video from 80MB to 5MB (~94%) via ImageKit, plus reliable error handling and retry mechanisms. Includes planning, code understanding, and verification methods for working with AI.

Incident Response in the Age of AI Attackers: A 6-Month Retrospective and the Four Pillars
AI attackers are making attacks on AI infrastructure more frequent. This article explains MarkTechPost's four-pillar incident response playbook based on a 6-month retrospective, with Fireworks AI and Klue case studies on implementation.

Abnormal Error Rate Spike in Claude Mythos 5.2 and Fable 5.2
Claude Mythos 5.2 and Claude Fable 5.2 show an abnormal spike in request error rates, marked as investigating on the official status page. This article covers the incident overview, practical impact on developers, and recommended responses.