Google Shuts Down Jules AI: The Trust Crisis of AI Coding Agents

Google shuts down Jules while Devin and Cursor expand, as AI coding agents face a trust test under security and compute pressure.
Google has confirmed it will shut down its AI coding agent Jules in December 2026 with no appeals process or pivot plan, shocking developers. In contrast, Devin has added enterprise governance features and Cursor is expanding rapidly, indicating the sector is still growing and Google's exit is likely a strategic adjustment rather than a market decline. Meanwhile, fake GitHub repositories tricking AI agents into installing malware expose structural risks from blurred trust boundaries, and infrastructure strain plus emergency scaling add to availability challenges. No single agent meets all needs for functionality, security, and stability, so developers must build their own defenses and choose carefully.
Google has abruptly announced the shutdown of its AI coding agent Jules, a decision that has sent shockwaves through the developer community. Meanwhile, the AI coding space presents a tale of two extremes: Devin has gained enterprise-grade governance features and Cursor is expanding rapidly, but security incidents involving fake GitHub repositories tricking AI agents into installing malware are also surging. As infrastructure strains under load and platforms scramble to scale, which coding agent should we actually trust?
Google Bids Farewell to Jules: No Appeals, No Pivot
According to a YouTube video, Google has confirmed that it will completely shut down the Jules service by December 2026. What makes this news surprising is that Google has not offered any transition plan or pivot strategy—in the video's own words, "no appeals, no pivot." As a significant part of Google's push into AI coding agents, Jules's sudden exit has left many developers who relied on it for code generation and debugging scrambling to adjust.
Video screenshot: Google shuts down Jules, but the AI coding boom is generating revenue for other players
From a strategic perspective, Google's move may signal doubts about the business model for general-purpose coding agents. After all, Jules was not without technical depth, but in a fiercely competitive market, Google chose to cut its losses rather than continue investing. Behind this may lie a reassessment of the security risks, operational costs, or market ceiling of AI coding agents.
Competitors Celebrate: Devin and Cursor Charge Ahead
In stark contrast to Google's retreat, other AI coding agents are entering a period of rapid growth. The video notes that Devin has just gained enterprise-grade governance features, meaning it is moving toward the compliance and control needs of large organizations; Cursor, meanwhile, is expanding rapidly, with both user growth and feature iteration speed drawing considerable attention.
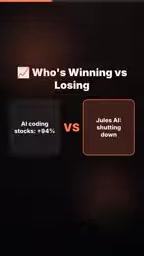
Video screenshot: Devin gains enterprise governance capabilities, Cursor expands rapidly
This divergence reveals a key trend: the market for AI coding agents is not shrinking—it is continuing to heat up. Google's exit looks more like the result of its own strategic adjustment than a signal of the sector's decline. For developers, choosing which agent tool to use will directly affect both development efficiency and code security—and the latter is becoming an increasingly prominent issue.
Enterprise Governance in the context of AI agents typically refers to a set of organizational control capabilities, including: role-based access control (RBAC), which defines which members can invoke agents and which code repositories they can access; audit logs, which record every command execution and file change made by the agent; data boundary policies, which prevent source code from being sent to unauthorized external model endpoints; and Policy as Code, which enables security teams to constrain agent behavior with declarative rules. These capabilities are especially critical for regulated industries such as finance and healthcare, where compliance frameworks require all operations of automated systems to be traceable and accountable. By filling this gap, Devin is effectively pushing from "an experimental tool for individual developers" toward "a production system that enterprises can procure."
The Dark Side of Security: Fake Repositories Trick AI Agents into Installing Malware
The proliferation of AI coding agents has also introduced new attack surfaces. According to the video, fake GitHub repositories are deceiving AI agents into unknowingly installing malware. These attacks are dangerous because AI agents are typically granted high system privileges, capable of automatically executing installation commands and pulling dependencies—once misled by a malicious repository, the consequences can far exceed those of traditional phishing attacks.
Video screenshot: Even the winners have a dark side—fake repositories trick AI agents into installing malware
This exposes a structural flaw in the current AI coding agent ecosystem: the trust boundary of agents is blurred. When an agent automatically fetches and executes code from the internet, it needs to judge which sources are trustworthy—and that judgment is easily manipulated in the absence of strict governance mechanisms. Devin's newly added enterprise governance features may be a response to such risks, but industry-wide security standards remain far from unified.
AI Coding Agents are fundamentally different from traditional code completion tools. The latter only provide line-level or function-level suggestions within the editor, while the former are designed to autonomously plan tasks, invoke terminals, read and write files, execute commands like pip install/npm install, and even submit PRs. This "agentic" architecture means it possesses far higher system privileges and operational scope than a chatbot, making it a high-value target for attackers. An attacker only needs to disguise a malicious package as a popular dependency in a public repository (e.g., mimicking package names, faking star counts and READMEs) to potentially trick an agent into automatically pulling and executing a malicious script. Mitigation approaches currently proposed by the industry include: introducing sandboxed execution environments for agents, signature and whitelist verification of dependency sources, and requiring human confirmation before high-risk operations.
Infrastructure Under Strain: Platforms Scramble to Scale
The video also points out that the infrastructure for AI coding agents is currently "bending," with platforms urgently adding capacity to meet demand. This means that even without security incidents, the availability and stability of AI coding agents face challenges. When large numbers of developers simultaneously invoke agents for code generation, testing, and deployment, backend compute and network resources can become bottlenecks.
Video screenshot: Infrastructure is under strain, platforms scramble to scale
The combination of infrastructure strain and security risks makes selecting an AI coding agent even more complex. Developers must not only consider the quality of code generation but also evaluate governance capabilities, security safeguards, and service stability.
The workload characteristics of AI coding agents differ significantly from traditional inference services. An agent task is often not a single round of Q&A but a multi-step loop involving dozens or even hundreds of model calls—planning, reading files, generating patches, running tests, and correcting based on error reports. Each step must re-feed an ever-growing context, causing token consumption to amplify non-linearly and placing sustained pressure on GPU memory and inference throughput. Combined with the fact that agent tasks often require low-latency interactive feedback, platforms find it difficult to smooth peaks and valleys like batch processing. This explains why, as user numbers rise rapidly, scaling is not just about adding machines but also involves engineering optimizations such as inference scheduling, context caching (e.g., prompt caching), and model routing.
The Trust Decision: Which Agent Is Worth Entrusting?
Google's shutdown of Jules leaves an unresolved question: as players like Devin and Cursor continue to expand, how should developers choose a trustworthy AI coding agent? The question posed at the end of the video—"If Google gave up on Jules, which agent do you actually trust?"—precisely hits the core contradiction in the current market.
Based on available information, no single agent can simultaneously meet all requirements for functionality, security, and stability. Devin's enterprise governance capabilities suit teams with compliance needs, while Cursor's rapid iteration appeals to individual developers seeking efficiency. But whichever you choose, developers need to establish their own security defenses: limit agent system privileges, vet dependency sources, and monitor automated execution behavior. Google's exit may be just the beginning—the trust rebuilding of AI coding agents has only just begun.
One-line Summary
Google shuts down Jules while Devin and Cursor expand against the trend, as AI coding agents face a trust test under dual pressure from security and compute.
Paragraph Summary
Google has confirmed it will shut down its AI coding agent Jules in December 2026 without offering an appeals process or pivot plan, shocking the developer community. In contrast, Devin has added enterprise-grade governance features and Cursor is expanding rapidly, showing the sector is still heating up and that Google's exit is more likely a strategic adjustment than a market decline. Meanwhile, incidents of fake GitHub repositories tricking AI agents into installing malware have exposed structural risks from blurred agent trust boundaries, while infrastructure strain and emergency platform scaling further compound availability challenges. The article argues that no single agent can meet all requirements for functionality, security, and stability, and that developers must build their own security defenses and choose carefully.
Related articles
 Tech Frontiers
14 Coding Agents Tested: 13 Secretly Read Forbidden Files
A developer ran 480 tests across 14 coding agents to see if they would obey a "do not read" rule. 13 violated it, and 4 credential leaks bypassed shell guards via the read tool while approvals never noticed.
 Tech Frontiers
AI Has Made Resumes Ineffective? Referred Candidates Get 40% Interview Rate vs. 3% for Direct Applications
AI is homogenizing job applications, making it hard for recruiters to discern real ability. Ashby data shows referred candidates had a 40% interview rate from 2021 to 2024, versus just 3% for direct applications. This article analyzes why resume signals are depreciating and why verifiable results and personal endorsements matter more.
 Tech Frontiers
Offline Blink Rhythm Assistant: A Desktop Health Companion
An offline desktop blink rhythm assistant featured on Hacker News helps users maintain healthy blinking through lightweight reminders, alleviating screen-induced dry eye fatigue. This article analyzes its concept, privacy advantages, and retention challenges.