Local Deployment Sparks Debate Again: User Banned and Warned for Testing Own Plugin

User threatened with ban for red-teaming self-developed plugin, sparking debate on hosted risk control vs. localization.
The article discusses a Reddit user who was threatened with a ban for red-teaming their self-developed plugin. The appeal was instantly rejected without any details, resonating widely with the community. It notes that red-teaming is standard security practice but its traffic patterns are hard to distinguish from real attacks, causing automated risk control misjudgments. The incident highlights the power asymmetry between hosting platforms and developers: misjudgment costs fall on users, and appeal channels are ineffective. Community discussion points to local deployment as an alternative for behavioral autonomy, advising developers in security testing or high-frequency experiments to prioritize local environments or keep local backups.
Introduction: A Ban Storm Triggered by Red-Teaming
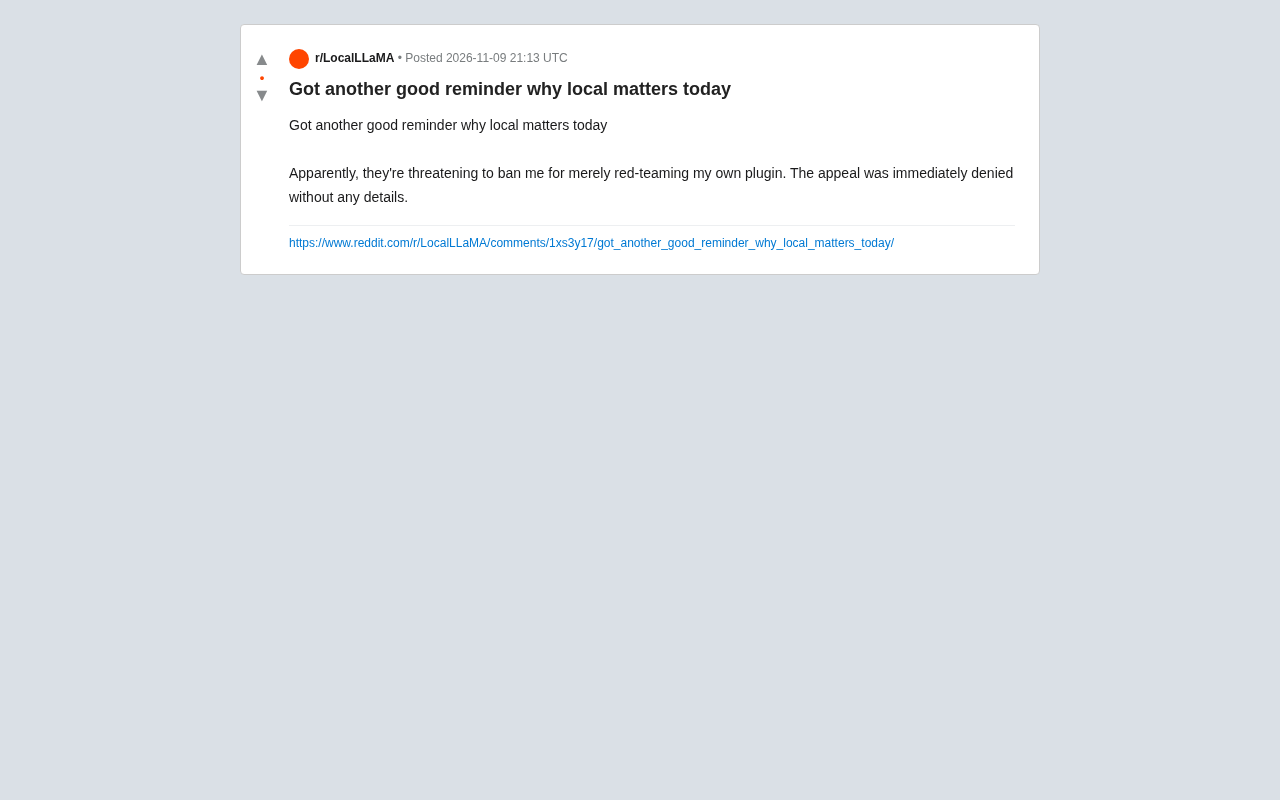
Recently, a Reddit user posted that they received a ban threat from the platform simply for conducting red-teaming on their self-developed plugin, and their appeal was immediately rejected without any details provided. The user summarized their experience as "another good reminder why local matters today," and the post quickly resonated with the community.
This is not an isolated incident. As AI services increasingly intervene in developers' daily workflows, the boundary of what platforms deem "abnormal behavior" is becoming a Sword of Damocles hanging over users' heads.
Red-teaming originates from the practice of simulating enemy attacks in military exercises. In the information security field, it refers to an independent team playing the role of attacker to conduct adversarial testing on systems to discover vulnerabilities and defense weaknesses. In the context of AI and plugin development, red-teaming typically includes constructing malicious inputs, simulating jailbreak prompts, injecting anomalous data, and other operations, with the goal of exposing problems before real attacks occur. Such testing is highly similar in behavioral characteristics (e.g., high-frequency requests, anomalous input patterns) to real attacks, making it easily misjudged by automated risk control systems on platforms. For developers, red-teaming is a standard part of security engineering; but for hosting platforms, it is just a string of suspicious signals in traffic logs—this difference in perspective is precisely the root cause of this ban storm.
Event Recap: Just Testing My Own Plugin
According to the original post, the user's plugin was entirely self-developed, and the target of red-teaming was their own work. In conventional security engineering practice, red-teaming is a standard action for discovering vulnerabilities and verifying defense capabilities. However, on the hosting platform, this testing behavior was identified by the system as suspicious activity, directly triggering the ban mechanism.
What frustrated the user even more was the appeal process—no trace of manual review, no specific violation explanation, and the rejection was almost "instant." This meant the user didn't even have a chance to explain "I'm testing my own stuff," and account security depended entirely on the judgment of automated risk control.
Why "Local" Is Once Again a Keyword
The "local matters" in the original post's title points to the core of the community sentiment. When cloud services hold the power of life and death, local deployment provides not only data sovereignty but also behavioral autonomy.
Running plugins and conducting tests in a local environment means there is no third-party platform adjudicating "whether you should do this." Developers can freely simulate attacks, inject anomalous inputs, and observe boundary behavior without worrying about triggering some invisible red line. This freedom is precisely the infrastructure for security research and plugin development.
The direction of discussion under the post also confirms this: many users shared their experiences of being mistakenly penalized by platforms for normal development activities, and localization solutions were repeatedly mentioned as a path to avoid risks.
The core difference between local deployment and cloud hosting lies in where control resides. In the cloud hosting model, the platform controls the infrastructure, runtime environment, and risk control rules, and user behavior must be filtered and adjudicated by platform policies; local deployment places the runtime environment entirely on the user's own device or server, with no third-party real-time review of operational behavior. For developers, a local environment means not only that data doesn't leave the machine (data sovereignty) but also that they can freely execute high-frequency tests, simulate attack traffic, and modify runtime parameters without worrying about triggering platform red lines. This is the technical reason why the community repeatedly emphasizes "local matters" in discussions: localization provides an experimental space free from external rule constraints, which is precisely the foundational condition that security research and plugin iteration depend on.
The Tension Between Platform Risk Control and Developer Freedom
From the platform's perspective, red-teaming behavior and real attacks are indeed difficult to distinguish in terms of traffic characteristics, and automated risk control choosing to "err on the side of caution" has its operational logic. But the problem is that the cost of misjudgment is entirely borne by the user, while the appeal channel exists in name only.
This asymmetrical power relationship is pushing some developers toward self-hosted solutions. When "testing your own code" can become grounds for a ban, the hidden costs of cloud services are no longer just subscription fees.
Automated risk control systems are typically based on rule engines and machine learning models, performing real-time scoring and interception of user behavior. Their design goal is to maximize recall—better to mistakenly ban a normal user than to let a potential attacker slip through. This "err on the side of caution" strategy is understandable at the platform operations level, but it brings a structural problem: the cost of misjudgment is almost entirely borne by the user. When the appeal channel lacks manual review and rejections provide no specific reasons, users effectively lose their ability to defend themselves, and account security depends entirely on the judgment of a black-box model. This power asymmetry between platform and user is precisely the deep-seated reason why the hosting model is criticized—users relinquish control over the runtime environment but do not receive equivalent procedural justice guarantees.
Implications for Developers
This incident provides a concrete reference for decision-making: if your work involves security testing, reverse engineering, or high-frequency experimental operations, a local environment is worth prioritizing. Even when using cloud services, you should maintain local backup solutions for critical workflows, avoiding putting all your eggs in a basket managed by automated rules.
The community's reaction shows that this is not an occasional technical glitch but a public demonstration of the inherent risks of the hosting model. Whether localization is "better" is debatable, but the point of "more controllable" has been repeatedly validated in similar incidents.
One-line Summary
A user received a ban threat from the platform for red-teaming their self-developed plugin, sparking discussion about hosted risk control and localization solutions.
Paragraph Summary
The article centers on an incident where a Reddit user was threatened with a ban by the platform for conducting red-teaming on their self-developed plugin. The user's appeal was instantly rejected without any details, sparking widespread resonance in the community. The article points out that red-teaming is a standard practice in security engineering, but its traffic characteristics are difficult to distinguish from real attacks, leading to misjudgment by automated risk control. The incident highlights the power asymmetry between hosting platforms and developers: the cost of misjudgment is borne by users, and the appeal channel exists in name only. Community discussion thus points to local deployment as an alternative for preserving behavioral autonomy, and suggests that developers involved in security testing or high-frequency experiments should prioritize local environments or maintain local backups.
Related articles

RePlan-VLA: Progress-Aware Replanning Breakthrough for Long-Horizon Robotic Manipulation
The RePlan-VLA framework converts VLA models' short-horizon capabilities into reliable long-horizon execution through progress-aware adaptive replanning, improving success rates by 21.9% and 10.4% on RoboCasa365 and CALVIN, and validating real-world deployment on a Franka Research 3 robot.

Geometric Bridge Flow Matching: A New Breakthrough in Blind Rigid Motion Correction
Geometric bridge flow matching enables blind rigid motion correction in head CBCT, achieving 37.1 dB PSNR and 0.27 mm RPE on simulated data in ~9.1 minutes, outperforming existing methods.

Google Releases Gemini 4 Hydrogen: 2.5x Faster Without Sacrificing Intelligence
Google releases the lightweight Gemini 4 Hydrogen: 2.5x faster task completion, AA Intelligence Index of 54 beating its flagship sibling, 7.3s single-step on Agent Arena faster than Claude and GPT rivals, four thinking levels with pay-as-you-need pricing, now available across AI Studio and more.