MCP Server Security: The Overlooked Risks in AI Agent Connectivity
MCP is becoming AI agents' universal connectivity layer, but security practices are lagging dangerously behind its rapid adoption.
MCP (Model Context Protocol) is rapidly spreading as the standard protocol for AI agents accessing external tools and systems, yet security discussions are nearly absent. The protocol's universality amplifies risk — sitting at the boundary between AI and real systems, it becomes a high-value attack target. With no mature best practices yet established, a Substack series aims to fill the gap, with the next installment focusing on anti-patterns like over-permissioning, missing origin validation, and hardcoded credentials. The core message: as MCP evolves into critical infrastructure, security must be built in from day one.
When MCP Becomes the Universal Connectivity Layer for AI
More and more companies are building MCP (Model Context Protocol) servers with a single goal: enabling AI tools and agents to seamlessly connect with their internal systems. MCP offers a compelling connectivity solution and is rapidly becoming the standard bridge between AI agents and external systems.
But as security blogger Security Bit points out in a recent video, there's a widely overlooked problem behind this construction boom — almost no one is seriously discussing the security of MCP servers. When a protocol takes on the responsibility of connecting AI to critical business systems, the attack surface it introduces grows right along with it.
MCP (Model Context Protocol) is an open-source standard protocol proposed by Anthropic in late 2024, designed to address the fragmented integration between large language models and external tools and data sources. Before MCP, every AI application that needed to connect to external systems — databases, code repositories, SaaS tools — required custom-built connection logic that was costly and hard to reuse. MCP defines a unified client-server communication specification, allowing AI models to discover and invoke tools and resources exposed by any MCP server in a standardized way. Major AI tools including Claude, Cursor, and Continue already support MCP, and the third-party MCP server ecosystem is expanding rapidly to cover file systems, browser control, database queries, API calls, and more.
Why MCP Security Deserves Serious Attention
The core value of MCP lies in its emergence as the universal interface through which AI agents access data, invoke tools, and operate systems. That very "universality" is precisely what amplifies security risk: once an MCP server becomes the default channel between an agent and enterprise systems, it becomes an extremely high-value target for attackers.
The permissions granted to agents via MCP often go far beyond read-only queries — they may involve write operations, system calls, and access to sensitive data. Without strict authentication, permission isolation, and input validation, a manipulated or hijacked agent could use an MCP server to cause real damage to backend systems. In other words, the convenience and the danger of MCP come from the same source — it sits at the boundary between AI and real-world systems.
A High Learning Curve, But Not Insurmountable
The video's author candidly admits that MCP server security "looks incredibly complicated and hard to know where to start." This honestly reflects the current reality practitioners face: MCP is a nascent protocol, mature security best practices around it have yet to take shape, and systematic public learning resources remain scarce.
To fill this gap, the author has launched an ongoing series on Substack, with three articles published so far and more planned. He encourages readers to read, ask questions, and share feedback — and welcomes anyone with deeper knowledge to contribute. This open, collaborative attitude reflects the fact that MCP security is still in its early community exploration phase.
What's Next: Focusing on MCP Anti-Patterns
The author reveals that the next installment in the series will focus on MCP server anti-patterns. This is a direction worth watching: rather than simply listing "what you should do," identifying "what you shouldn't do" often helps developers avoid high-risk implementation choices much faster.
Common anti-patterns typically include over-permissioning, lack of request origin validation, hardcoding sensitive credentials on the server side, and insufficient filtering of instructions passed in by agents. For teams currently building MCP servers, learning about these pitfalls in advance is far more efficient than patching things up after the fact.
The concept of anti-patterns originates from software engineering — it refers to design or implementation approaches that seem reasonable in practice but produce negative consequences. As the counterpart to "best practices," anti-patterns derive their value from real lessons learned from mistakes, describing the traps developers naturally fall into under certain pressures (like tight deadlines or the desire to keep things simple). In security, recognizing anti-patterns is especially critical, because vulnerabilities often don't stem from ignorance but from "good enough" compromises that fail under specific attack scenarios. For emerging protocols like MCP, cataloging anti-patterns is particularly valuable — in the early stages before best practices have matured, "knowing what not to do" can sometimes reduce risk more effectively than "knowing what to do."
Key Takeaways for Builders
While this brief overview doesn't dive into technical specifics, the core message is clear and important: when embracing the connectivity convenience that MCP offers, security cannot be treated as an afterthought. As AI agents accelerate their penetration into real enterprise workflows, MCP servers are gradually evolving into new critical infrastructure — and critical infrastructure should have security built in from the very beginning of its design.
For developers and security teams alike, now is the time to start systematically learning about MCP security and building a defensive mindset. Paying attention to anti-patterns, applying the principle of least privilege, and strengthening identity and origin validation are the right first steps.
Related articles
Anthropic IPO Countdown: The Compute Cost Ledger Behind a $2 Trillion Valuation
Anthropic's IPO targets up to $2 trillion — double its Series H valuation. We break down the timeline, compute cost logic, and the key question investor day must answer.
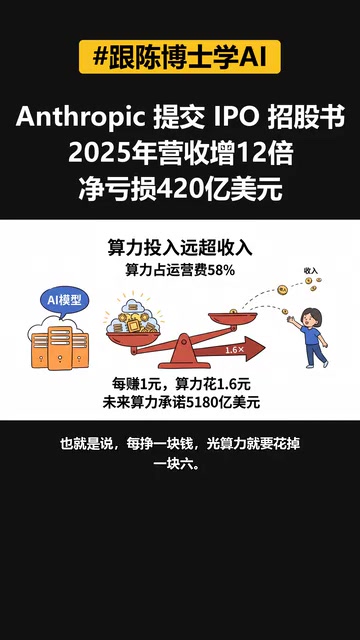
Anthropic IPO Prospectus Revealed: Behind 12x Revenue Growth, the Twin Tests of Compute Costs and Customer Concentration
Anthropic filed its IPO prospectus: 2025 revenue up 12x to $4.6B, net loss $42B including $34B non-cash. Breaking down compute costs, $2T valuation logic, customer concentration risks, and founder control.
Xteink X4 Pro Review: A Mini E-Reader That Fits in Your Pocket, Now More Affordable
Xteink X4 Pro is a 4.26-inch mini e-reader, smaller and thinner than a 6-inch Kindle, magnetically attachable to phones, and cheaper than ever. We analyze its screen, design, use cases, and value.