Meta Launches Muse: A Personal AI Agent to Help You Tackle Your To-Do List

Meta launches Muse, a personal AI agent app that executes daily tasks while requiring user approval for spending.
Meta has released Muse, a personal AI agent app designed to go beyond chatbots by proactively handling everyday tasks. According to official demos, Muse can plan meals, generate shopping lists, create personalized cards, negotiate refunds, and identify unused subscriptions for cancellation. Users can customize the agent's name, appearance, and personality, and it retains personal preferences over time. On the control side, Muse uses a human-in-the-loop approach — any spending or external contact requires explicit user approval. It marks Meta's formal entry into the AI agent race, though the gap between demo polish and real-world reliability remains to be seen.
Meta has introduced a new app called Muse, built around the concept of a "personal AI agent." Rather than a simple chatbot, Muse is designed to proactively execute tasks and handle everyday chores on your behalf — from planning dinner to negotiating refunds. It represents Meta's push to move AI beyond "answering questions" and into "actually getting things done."
What Muse Can Do: From To-Do Lists to Real Execution
Muse's core pitch is helping users work through their to-do list. In the official demo, a user hands the AI agent an entire list of tasks, and it handles them one by one — rather than simply offering suggestions.
The first scenario shown is creating a personalized birthday card. You just tell it what the birthday person likes — hiking, good food, and "belly rubs" — and it generates a card tailored to them. This kind of task showcases Muse's creative generation capabilities.
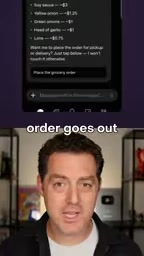
A more telling example is dinner planning. The user provides their dietary preferences, budget, and even what's already in the fridge, and Muse arranges meals, generates a shopping list, and helps place an order. Crucially, the user must confirm before any order is placed — the AI won't spend money without explicit approval.
Handling the Annoying Stuff: Refund Negotiations and Subscription Cleanup
Muse isn't just for pleasant purchases — it's also designed to tackle the frustrating tasks many people put off. One demo shows Muse negotiating a refund on the user's behalf: the user provides the order details and explains the issue, Muse asks for permission to contact customer service, and the user decides whether to proceed.
Another common pain point is subscription management. Muse can identify subscriptions you're no longer using, letting you pick which ones to cancel. For many people, forgotten auto-renewals are a silent drain on finances — making this kind of feature genuinely useful.
Also worth noting is the flexibility of task input — users can add tasks from their phone at any time, even while out and about, tossing new to-dos to Muse on the fly. This makes it feel more like a personal assistant you carry with you, rather than a tool you only use sitting at a desk.
Personalization and Permission Controls
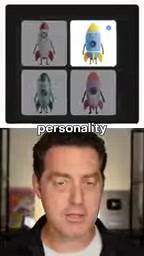
Muse lets users name their AI agent, customize its appearance, and shape its personality, and it remembers all of the user's preferences over time. This deep personalization is designed to make the assistant fit each person's habits more naturally, building long-term memory and adaptation.
In a model where an agent acts on your behalf, privacy and control become unavoidable concerns. Meta repeatedly emphasized two points in the demo: first, users decide what Muse can access; second, any action involving spending money or reaching out externally (such as placing orders or contacting customer service) requires explicit user approval. This "human-in-the-loop" design is a key trust-building mechanism in today's AI agent products.
Human-in-the-Loop (HITL) is a safety architecture principle in AI system design that requires human confirmation at critical decision points, rather than letting the AI act fully autonomously. The concept originates from automated control systems and is especially important in AI agent products — when a system can call external services, spend money, or send communications on a user's behalf, errors can have far greater consequences than in a simple chat context. Current mainstream AI agent products, including OpenAI's Operator and Google's Project Mariner, broadly adopt HITL mechanisms to address user trust. The core trade-off: more confirmation steps mean greater safety, but reduce the convenience that automation is supposed to provide. Finding the right balance between "autonomous enough" and "controllable enough" is the central UX design challenge for this category of products.
Industry Context: Agentic AI Takes Shape
Muse represents another major bet by a tech giant on the AI agent track. Compared to purely conversational AI, "agentic AI" — capable of using tools and executing multi-step tasks — is widely seen as the next frontier. Meta is packaging this concept into an everyday consumer app through Muse, targeting real-life scenarios like making cards, ordering food, handling refunds, and managing subscriptions.
That said, there's often a gap between a polished demo and real-world experience. The challenges AI agents face in actual execution include: accuracy in understanding complex instructions, reliability when integrating with third-party services, and accountability when things go wrong — none of which tend to be fully addressed in official demo videos.
It's worth noting that this article is based on Meta's officially released demo video. All features and effects shown come from the company's own promotional materials, and real-world performance remains to be verified through independent reviews.
Agentic AI differs fundamentally from traditional conversational AI in that it can decompose goals, call external tools (such as browsers, APIs, and payment systems), and track task state across multiple steps — whereas traditional AI essentially responds to a single input at a time. The technical foundations enabling this typically include Function Calling, Tool Use, and long-context memory, transforming the model from a "language generator" into a coordinator capable of completing end-to-end tasks across multiple systems. Since 2024, major tech companies have been moving aggressively in this direction: Anthropic launched Computer Use, OpenAI released Operator, and Google introduced Project Mariner — all aimed at the same goal: letting AI help users complete tasks in real digital environments, not just inside a chat window. Muse's launch marks Meta's formal entry into this race, with everyday consumer scenarios as its chosen entry point.
Takeaway
Muse offers a glimpse into Meta's vision for personal AI agents: delegating the tedious tasks of daily life to AI, while preserving user control through permission management and confirmation steps. If these features perform as smoothly in real use as they do in the demo, Muse has the potential to become a genuinely useful everyday assistant. But until that experience is proven in the wild, those promises still come with a question mark.
Related articles

Testing the 350K-Star REA in an Isolated Environment: 4-Second Install, but Watch Out for Two Pitfalls
Isolated lab test of the 350K-star open-source reverse-engineering tool REA: 4-second install, 15 seconds to list a screenshot tool's outbound addresses, 565 communication channels mapped, while exposing two pitfalls—user-level settings writes and 31 high-risk tool permissions—plus three safety rules.
Reverse Engineering + AI Agents: The T…
Reverse Engineering + AI Agents: The Technical Truth Behind Cloning Adobe Apps in Weeks
A developer used AI Coding Agents for reverse engineering to build 7 open-source Adobe alternatives in weeks. We explore how it works, the MCP Server that hit 100K stars in 6 days, and the real technical and legal limits.
MCP Protocol Explained: How AI Agents Connect to External Tools
What is MCP (Model Context Protocol)? From APIs and Function Calling to MCP's three-layer architecture, this article explains how AI Agents connect to external tools like calendars and email, and reveals two major security risks—prompt injection and tool poisoning—along with four protection principles.