Tata Motors App Reportedly Has Hardcoded Credentials, Sounding Another Alarm for Mobile Security

Tata Motors App was reported to have security issues such as hardcoded credentials, warning that mobile credential management must be part of DevSecOps.
A Hacker News discussion about hardcoded credentials and other security issues in the Tata Motors App, though not widely noticed, highlights a long-neglected pain point in mobile development: credential management. Hardcoded credentials let attackers extract passwords and API keys by decompiling APKs or IPAs, risking backend services and user data. The article examines why the problem persists and why automaker apps face physical-world risks, and recommends secret scanning in CI/CD, secret management services, code obfuscation, and certificate pinning to move from after-the-fact fixes to security by design.
In the field of mobile application security, a seemingly basic mistake can often trigger a chain reaction. Recently, a discussion appeared on Hacker News about hardcoded credentials and other security issues in the Tata Motors App. Although the post did not gain much traction (only 3 points and no comments at the time), the topic touches on a long-neglected pain point in mobile development: lax credential management.
Hardcoded Credentials: High Risk Behind Convenience
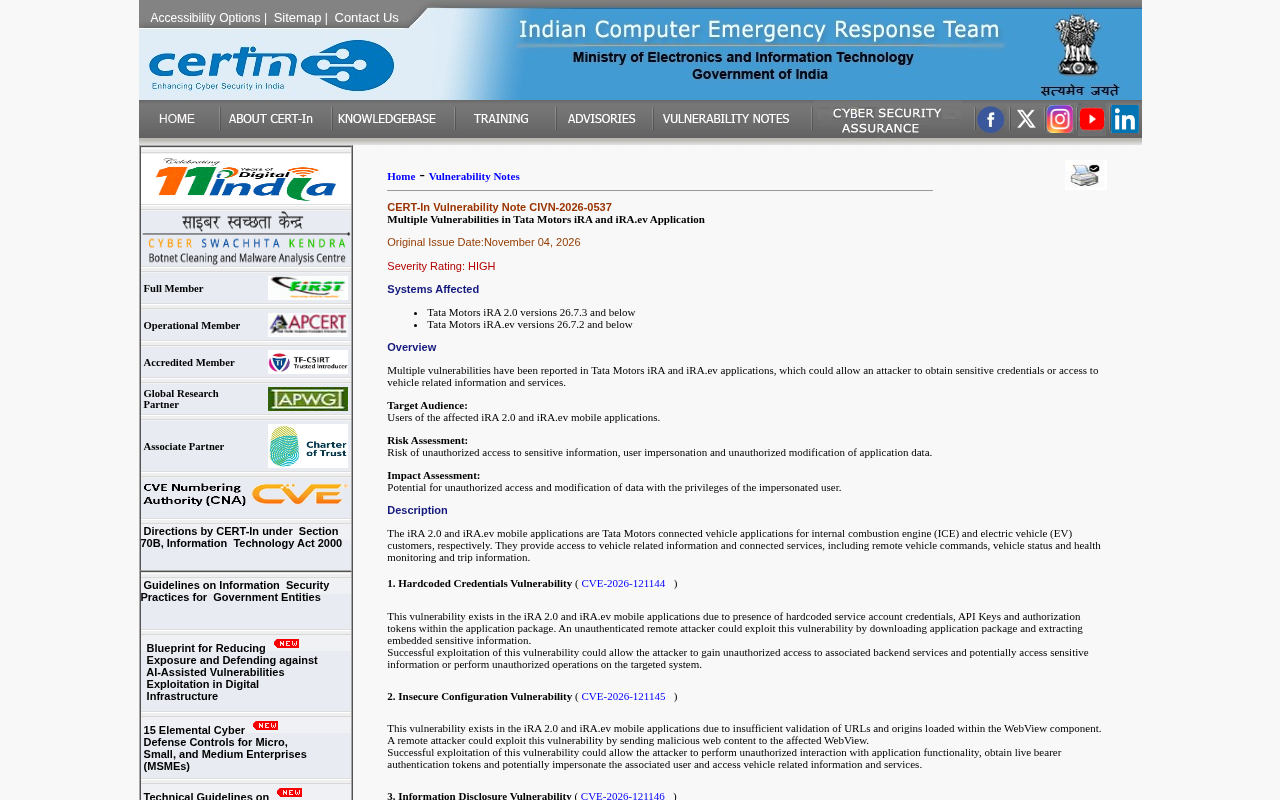
According to the Hacker News post title, the Tata Motors App contains hardcoded credentials and other security issues. Hardcoded credentials refer to developers writing sensitive information such as passwords, API keys, and tokens directly into an application's source code. This practice is not uncommon in fast-moving development cycles — developers hardcode credentials "temporarily" for debugging convenience or to meet deadlines, but often forget to remove them before release.
From a security perspective, the harm of hardcoded credentials is fundamental. Mobile application packages (APK or IPA) are essentially files that can be reverse engineered. Attackers only need to decompile the app to extract these plaintext or weakly encrypted credentials. Once credentials leak, attackers may use them to access backend services, databases, or third-party APIs, causing data breaches or even control of business systems.
Why This Problem Persists
The reason hardcoded credentials keep recurring is rooted in the lack of automated secret scanning mechanisms in development workflows. Many teams focus on functional logic during code review and lack vigilance against hardcoded sensitive information. In addition, some developers misunderstand the security boundary of mobile clients, believing that "code is invisible after the app is released" or that "obfuscation tools can block everything." In reality, professional reverse engineering tools are enough to bypass most obfuscation methods.
Reverse Engineering refers to the process of restoring source code logic or extracting resource files from a published binary program through decompilation, disassembly, and other means. For mobile applications, Android APKs are essentially ZIP archives. Attackers can easily unpack them with tools such as apktool and jadx and decompile Dalvik bytecode, sometimes even recovering code close to the original Java/Kotlin. Although iOS IPAs are compiled and optimized, tools such as Hopper and IDA can still be used for static analysis and dynamic debugging. This means that any string written into an application package — including API keys, database passwords, and third-party service tokens — has no real confidentiality. Developers often mistakenly believe that code obfuscation (such as ProGuard or R8) can prevent reverse engineering, but obfuscation only increases reading difficulty; it cannot hide plaintext string constants. Therefore, the premise of credential security is acknowledging that "the client is untrusted" and that sensitive information must be stored on the server side or delivered through secure runtime mechanisms.
Secret Scanning is an automated technology specifically used to detect whether code repositories, configuration files, or build artifacts contain sensitive information such as passwords, API keys, and tokens. Mainstream implementations include static regular expression matching (such as detect-secrets and gitleaks) and entropy-based detection, which can identify high-entropy strings that appear random but are actually secrets. Integrating secret scanning into CI/CD pipelines can automatically block commits containing hardcoded credentials during code merge or build stages, thereby intercepting the problem before release. Platforms such as GitHub also provide push protection, which alerts developers in real time when they push code containing secrets. It is important to emphasize that scanning tools can only detect secrets with known patterns and cannot cover all cases, so they must be combined with code review standards and developer security training to form a multi-layered defense.
Other Issues: The Tip of the Iceberg
Although the "other issues" mentioned in the post title are not elaborated in the available material, based on common security disclosure practices, hardcoded credentials are often not isolated. They usually appear alongside insecure network communication, missing certificate pinning, and sensitive information leakage through logs. When an app is lax in credential management, it often means there are systemic flaws in its overall security baseline.
For an automaker like Tata Motors, its official app usually carries functions such as remote vehicle control, owner information management, and service appointments, so security requirements should be higher. If credential leakage risks exist on the app side, attackers may use them to access owner data or vehicle-related service interfaces, and the consequences should not be underestimated.
The Unique Nature of App Security in the Automotive Industry
In the era of intelligent connected vehicles, automaker apps are no longer just brand showcases; they are keys connecting users and vehicles. Some apps even have remote control capabilities such as unlocking doors and starting air conditioning. This makes security vulnerabilities in automaker apps carry more physical-world risk than ordinary consumer applications. If hardcoded credentials involve vehicle control interfaces, they could theoretically be maliciously exploited, although the specific impact depends on the robustness of backend authentication design.
Certificate Pinning is a technique that strengthens TLS communication security: when establishing an HTTPS connection, the client not only verifies whether the server certificate is issued by a trusted CA, but also compares the fingerprint of the server certificate or public key with a pre-embedded value. This effectively defends against man-in-the-middle (MITM) attacks; even if an attacker installs a malicious root certificate on the device, they cannot decrypt or tamper with the communication. Mobile applications often face threats such as rooted or jailbroken user devices and packet capture through proxy tools. Without certificate pinning, attackers can easily intercept plaintext traffic and then discover interface structures, tokens, and even hardcoded credentials. Implementation methods include configuring CertificatePinner in OkHttp or verifying public key hashes in the URLSession delegate on iOS. Note that certificate pinning must be accompanied by a certificate rotation strategy; otherwise, certificate updates will prevent older app versions from connecting.
What Developers Should Learn From This
The value of this incident (or disclosure) is not in criticizing a particular company, but in reminding the entire industry: credential management must be incorporated into the DevSecOps process. Specifically, teams should introduce static code scanning tools to automatically detect hardcoded secrets and passwords in CI/CD pipelines; use secret management services (such as Vault) to dynamically issue credentials; implement code obfuscation and hardening for mobile applications; and establish security response mechanisms to ensure vulnerability disclosures are handled promptly.
From a broader perspective, mobile application security needs to shift from "remediation after the fact" to "security by design." Problems such as hardcoded credentials are not technically complex; the difficulty lies in embedding security awareness into every developer's daily habits. The Tata Motors App case, regardless of the final details, is worth every mobile development team using as a self-check.
DevSecOps is the philosophy of embedding security practices into the DevOps process, emphasizing that security is not an independent gate before release but an activity that runs through requirements, development, build, testing, deployment, and operations. Its core methods include integrating static application security testing (SAST) at the IDE and code repository levels, automatically executing dependency vulnerability scanning (SCA) and secret scanning in CI/CD, and deploying dynamic application security testing (DAST) and runtime application self-protection (RASP) at runtime. For mobile, DevSecOps also covers hardened signing of build artifacts, integration with secret management services, and automated verification of security baseline configurations. Secret management services (such as HashiCorp Vault and AWS Secrets Manager) provide dynamic generation, short-term leases, and automatic rotation of credentials, so applications do not need to persistently store any long-term secrets locally, eliminating the need for hardcoding at the architectural level. Only by combining these two can "security by design" be turned from a slogan into executable engineering practice.
Conclusion
At present, the Hacker News post provides limited information and has not disclosed specific technical details or an official response from Tata Motors. However, the keyword "hardcoded credentials" itself is enough to raise alarm. In an era of increasingly frequent software supply chain attacks, a single password hardcoded in code may be the weakest link in the entire defense line.
One-line Summary
Tata Motors App was reported to have security issues such as hardcoded credentials, warning that credential management in mobile development must be incorporated into DevSecOps processes.
Paragraph Summary
A discussion on Hacker News about hardcoded credentials and other security issues in the Tata Motors App, though limited in attention, touches on a long-neglected pain point in mobile development: credential management. Hardcoded credentials allow attackers to directly extract passwords, API keys, and other sensitive information by decompiling APKs or IPAs, endangering backend services and user data. The article analyzes that the root cause of this recurring problem lies in the lack of automated secret scanning mechanisms and developers' misunderstanding of mobile security boundaries, and notes that automaker apps, because they involve remote vehicle control and owner information, extend security risks into the physical world. It recommends incorporating secret scanning into CI/CD pipelines, using secret management services to dynamically issue credentials, implementing code obfuscation and certificate pinning, and driving mobile security from "remediation after the fact" to "security by design."
Related articles

AI Coding Enters the Team Collaboration Era: Interpreting Three Major Moves from Meta, GitHub, and Mistral
Meta acquires Conductor, GitHub Copilot Fusion becomes available, Mistral opens Large 4 weights—three moves show AI coding shifting from code generation to organizing development workflows. This article explains task orchestration, model collaboration, and cost control for developers.

Building a RAG Assistant with Dify: A Practical Guide to Knowledge Bases, Workflows, and Agent Nodes
How should knowledge bases, workflows, and Agent nodes connect in a Dify RAG assistant? We break down the division of labor and wiring logic for a shippable app.
 Tech Frontiers
The AI Industry Doesn't Lack Marketing—It Lacks Good Products
AI faces market selloffs and public skepticism—is marketing really the problem? This analysis of market signals and product experience argues the core困境 is incomplete products and a gap between promises and experience; the only way to change perceptions is to ship better products.