Vercel AI SDK Releases sandbox-vercel@1.0.119 Patch Update

Vercel AI SDK releases sandbox-vercel@1.0.119, a routine patch syncing the internal harness dependency.
Vercel AI SDK has released `@ai-sdk/sandbox-vercel@1.0.119`, a patch update that synchronizes the internal `@ai-sdk/harness` package to the same version. Following SemVer conventions, this patch introduces no breaking changes or new features, making it safe to upgrade directly. Published via GitHub Actions with GPG signature verification, the release reflects Vercel's commitment to supply chain security and the project's active, high-frequency maintenance cadence (26.9k+ GitHub stars).
Update Overview
Vercel's AI SDK project (which has accumulated over 26.9k stars and 5.2k forks on GitHub) recently released @ai-sdk/sandbox-vercel@1.0.119. This is a typical patch-level update focused on dependency synchronization. It was published via GitHub Actions automation and verified with a GitHub GPG signature (key ID: B5690EEEBB952194).
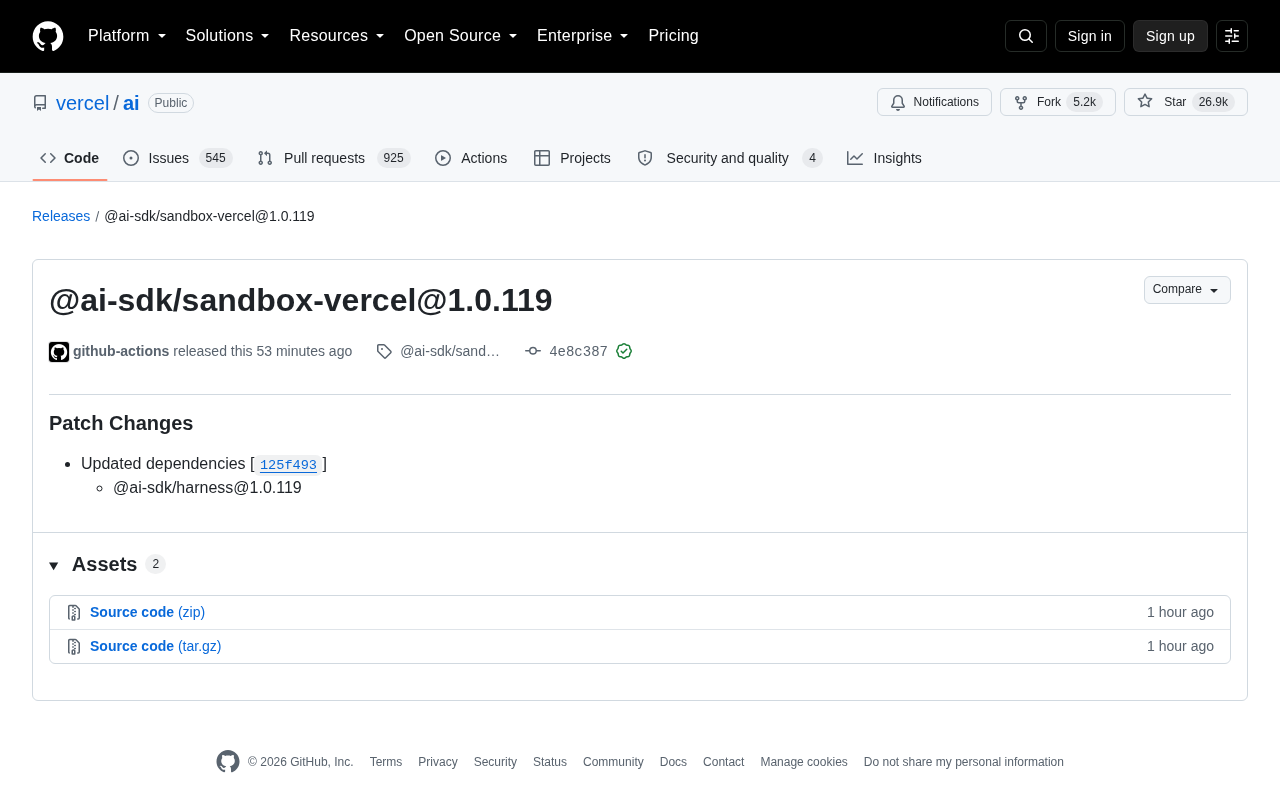
Following Semantic Versioning (SemVer) conventions, 1.0.119 represents an increment in the patch number — meaning this update introduces no breaking changes and no new features. Developers can upgrade with confidence without worrying about impact on existing code.
What Changed
The core change in this release falls under dependency updates (Patch Changes). The official changelog states:
Updated dependencies [125f493] — @ai-sdk/harness@1.0.119
In other words, the sandbox-vercel package has synced its dependency on @ai-sdk/harness to version 1.0.119. This kind of cascading version synchronization is very common in monorepo projects (where multiple packages are managed in a single repository) — which is exactly the architecture Vercel's AI SDK uses, keeping sub-packages on consistent version numbers for unified maintenance and release.
For developers building AI applications with this SDK, packages under the sandbox namespace typically deal with code sandbox execution environments. This capability plays a critical role in today's AI Agent, code generation, and code execution scenarios, enabling AI-generated code to run safely in an isolated environment.
@ai-sdk/harness is an internal foundational package within the Vercel AI SDK monorepo, primarily serving as a testing toolkit and runtime helper — functioning as a lower-level dependency for other sub-packages like sandbox-vercel. sandbox-vercel itself provides code sandboxing capabilities specifically for the Vercel platform, allowing code snippets generated by AI models to execute within controlled, isolated container environments, preventing malicious code from affecting the host system. This sandboxing mechanism is especially important in scenarios like Code Interpreter and AI Agent tool calls — for example, having an LLM generate a Python data analysis script and immediately executing it in a sandbox to return results, all transparently and safely for the user.
What This Means for Developers
While this single update record carries limited information on its own, it reflects the high-frequency, stable iteration cadence of the Vercel AI SDK project. Publishing every patch version with synchronized sub-packages indicates the team maintains a robust automated CI/CD pipeline — from GitHub Actions auto-publishing to GPG signature verification, the entire chain emphasizes supply chain security and trustworthiness.
For teams already using the AI SDK in production, it's recommended to monitor the official Releases page and stay current with patch updates to benefit from the latest dependency fixes and potential security improvements. Patch versions can generally be upgraded directly with minimal risk.
Software supply chain security has received widespread attention in recent years, with typical risks including malicious package injection (such as npm poisoning incidents) and dependency confusion attacks. GPG signature verification is an important safeguard against these threats: the publisher signs commits or releases with a private key, and downstream users can verify via the corresponding public key that a version genuinely comes from a trusted source and hasn't been tampered with. By integrating GPG signing into its automated release pipeline, Vercel ensures that even if the CI/CD pipeline were compromised, attackers would find it extremely difficult to forge a legitimate signature — providing an additional trust anchor for the entire dependency chain.
Summary
@ai-sdk/sandbox-vercel@1.0.119 is a routine dependency sync patch with no substantive functional changes. It primarily reflects the day-to-day maintenance activity of Vercel AI SDK as an active open-source project. Developers tracking this project's progress can continue following its GitHub repository for more complete change information.
Related articles

Chain of Thought Isn't Just for AI: How Humans Can Use CoT to Improve Thinking Quality
Chain of Thought isn't just a prompt trick for large models. Starting from a Hacker News discussion, this article analyzes why CoT works for human thinking too, breaks down actionable ways to transfer it, and highlights the key differences between human CoT and machine CoT.
Cloudflare Teams Up with OpenAI: Closi…
Cloudflare Teams Up with OpenAI: Closing the Loop from Vulnerability Discovery to Defense with AI
Cloudflare uses OpenAI Daybreak to investigate security vulnerabilities and generate reviewable remediation plans, while developers use Codex to boost coding efficiency and quality.

Orca Multi-Agent Orchestration in Practice: A Guide to Parallel Collaboration with Claude and Codex
Orca is Stable AI's free open-source agent workbench supporting 34 agents like Claude Code and Codex in parallel. Learn its Git worktree isolation, multi-model orchestration, and mobile management.