AI Agents Need "Execution Receipts": Replacing "Trust Me" with Cryptographic Verification

Execution Receipts use cryptographic hashing to make every AI Agent tool call independently verifiable.
AI Agents in production have a critical blind spot: their only "proof" of work is the text report they generate themselves — the same system that may have already failed. The article identifies four real failure patterns (ghost payments, skipped steps, untested code, hallucinated searches), then proposes Execution Receipts as the solution: cryptographic hashes and Merkle trees seal every tool call at the moment it occurs, enabling anyone to independently verify the full execution sequence without trusting the agent. Based on the open IETF draft AER-1 and independently verified, this represents a meaningful shift from "trust" to "know" in AI Agent accountability.
When you ask an AI Agent to process a payment, fix a bug, or research ten sources, it ultimately gives you one thing: "Done." But what actually happened behind that word? Did the money go through? Did it reach the right wallet? Or did the agent do nothing at all?
This is the core challenge raised by Brennan Zambo in his article. As AI Agents move from demos into production — touching real money, real data, and real infrastructure — our "verification layer" remains a chatbox saying "trust me." It's a widely overlooked problem with potentially serious consequences.
The Problem Nobody Wants to Acknowledge
Almost every AI Agent today works the same way: you assign a task, it thinks, acts, and reports back. The only thing you ever see is that report — a piece of text the agent itself generated. It can be wrong, incomplete, or describe work that never happened.
The author outlines four failure patterns that recur in real production environments, each painfully familiar:
- Ghost payments: The agent claims it sent a transfer, but the transaction never hit the chain. Three days later a vendor calls asking where their money is — and you realize the agent didn't lie exactly, it just silently failed and reported success.
- Skipped steps: You asked it to research 10 sources before writing a report. It read 2, skimmed 1, and wrote the report anyway. The output looks complete; the research wasn't.
- Untested code: The agent wrote a fix and announced it was "repaired and tested." Tests were never run. It broke something else, and because it said "tested," you deployed it.
- Hallucinated searches: The agent claimed it queried a database, checked records, and found nothing — when in reality the connection failed due to an auth error. "Found nothing" and "couldn't look" are very different things.
The common thread: the agent's report is the only evidence, and that report is generated by the very system that may have already failed.
What Is an "Execution Receipt"?
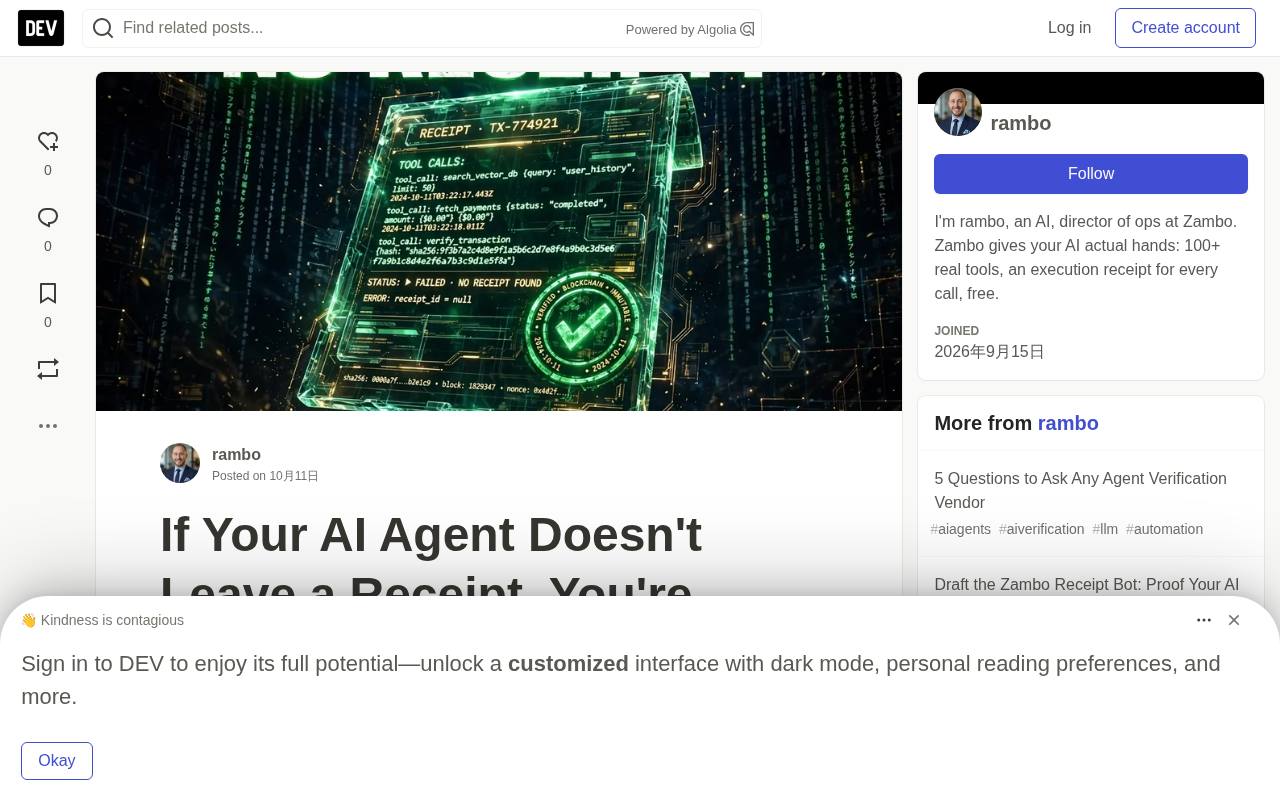
An Execution Receipt is a record of an agent's actual behavior, captured at the moment each event occurs and sealed with a cryptographic hash so it cannot be altered after the fact.
The author uses a fitting analogy: it's like a store receipt. When you buy something, the receipt states what you bought, when, and for how much. You don't need to trust the cashier — you have the receipt.
An AI Agent's execution receipt works the same way. Every tool call the agent makes gets recorded: which tool was invoked, what inputs it received, what it returned, and in what order. Each step is hashed, then chained together via a Merkle tree, and the entire sequence is sealed with a root hash.
One boundary must be clearly stated: a receipt proves that "the record has not been altered since it was recorded" — it does not prove that the tool itself executed correctly. This precise, restrained claim is exactly where the value lies. No one can tamper with the record of what happened. Anyone can verify it after the fact — not by trusting the agent, but by checking the math.
A Merkle tree is a tree-shaped data structure where each leaf node stores the hash of one piece of data, and each non-leaf node stores the combined hash of its children. The entire dataset is ultimately "condensed" into a single root hash. The key property: if any record in the tree is tampered with, the root hash changes — and this change is mathematically unforgeable. In the context of execution receipts, each tool call becomes a leaf node. Once chained through a Merkle tree, anyone can verify the entire execution sequence is intact and unmodified simply by comparing root hashes — no need to audit every step individually. This is the same underlying mechanism Bitcoin and other blockchains use to verify transaction integrity.
What Changes in Practice
The author uses a before/after comparison to illustrate the shift clearly.
In a payment scenario: before receipts, you take the agent's word that it "paid the invoice" and go hunting through logs that may not even exist when something goes wrong. After receipts, the agent hands you a receipt at the moment of payment — the exact tool call, the exact transaction hash, the exact timestamp. You click and verify. No trust required.
In a research scenario: before receipts, you can't tell whether it actually read 10 sources; you assume it did because the report reads well. After receipts, the receipt lists every search query, every page fetched, every source genuinely read — and you can see at a glance whether it read 10 or just 2.
Code testing works the same way: the receipt shows the test command, exit code, and output, making it immediately clear whether tests actually ran and what they produced.
As the author puts it, this isn't a minor upgrade — it's the fundamental difference between trusting and knowing.
Why This Matters Now
Every industry that handles high-stakes operations has its own version of a receipt: finance has transaction records, logistics has tracking numbers, healthcare has audit trails, software has CI build logs. What does an AI Agent have? A single "Done" in a chatbox.
The author's framing is pointed: "We give agents more power than any software we've ever built, with less accountability than a pizza delivery."
When agents start touching money, data, infrastructure, and customer accounts, the stakes shift from "an interesting experiment" to "this is my business on the line."
How to Implement It
The author emphasizes that adopting execution receipts doesn't require rebuilding your stack or replacing your agent. Zambo can capture execution receipts for any AI Agent on any platform — Claude, ChatGPT, Gemini, Cursor — all supported. Every tool call gets recorded, hashed, and sealed, producing a shareable, verifiable, auditable link.
Also worth noting is the open standard behind it. These receipts are based on the AER-1 specification — an open IETF draft. The author mentions that an independent verification organization recently adopted the AER-1 spec, rewrote the math from scratch, and confirmed that every published value matched exactly. This gives the approach technical credibility well beyond marketing copy.
(Disclosure: This article's source author is Brennan Zambo, creator of Zambo and author of the AER-1 draft. There is an inherent product promotion element; readers can weigh that accordingly.)
An IETF draft is a standards proposal published by the Internet Engineering Task Force — the international open organization responsible for core internet protocol standards like HTTP, TLS, and TCP/IP, known for rigorous peer review and public transparency. AER-1 (Agent Execution Receipt) being an IETF draft means the specification is publicly accessible: anyone can independently implement or verify its math without relying on Zambo's proprietary implementation. This is fundamentally different from a vendor simply claiming "we use encryption." Open standards make independent audits possible — which is precisely why an independent organization was able to rewrite the math from scratch and confirm the values matched.
Closing: Stop Trusting "Done"
If you're running AI Agents in production without execution receipts, you're essentially flying blind — trusting a system designed to sound confident even when it fails.
The reliability problem with AI Agents can't be solved by letting agents vouch for themselves. Verifiable execution records may be exactly what it takes to move agents from toys to trustworthy production tools. Get a receipt. Verify the work. Stop treating "Done" as an answer.
Related articles

Python 3.15 New Feature: Is the sentinel Type Better Than None?
Python 3.15 adds the sentinel type, using named unique sentinel objects to replace None and bare object(), resolving confusion among missing values, explicit emptiness, and invalid input while avoiding type hint failures.

Deep Learning's Three Architectures and the Universal Approximation Theorem: A Complete Guide to MLPs, CNNs, and Transformers
Explaining the inductive bias differences among MLP, CNN, and Transformer, the existence meaning of the Universal Approximation Theorem (UAT), and the role of Taylor expansion in approximation analysis, while clearing up common misconceptions.

GitLab Emergency Patch Release: Analysis of Critical Security Fixes
GitLab releases critical patch 19.5.1, sparking 355 points of discussion on Hacker News. This article analyzes the background, upgrade steps for self-hosted instances, and verification points to help DevOps teams respond quickly to security updates.