AI Can Do More Than Answer Questions: Exploring the Broader Potential of AI Tools

AI is evolving from passive Q&A to an active agent that invokes tools and orchestrates workflows.
This article explores the shift from AI as a Q&A tool to AI as an autonomous task executor, drawing on cues from a short-form video referencing "skills," "workflows," and agents like Claude and Codex. It breaks down three core agentic capabilities — tool invocation, workflow orchestration, and reusable skill modules — and highlights key selection criteria including sandbox security, auditability, model ecosystem integration, and workflow version management.
When AI Is No Longer Just a Q&A Tool
We've grown accustomed to treating AI as a glorified search engine — ask a question, get an answer, and that's that. But the direction of AI tool development has been quietly shifting in recent years: from passively responding to actively executing tasks. The central question posed by the source material — "What if your AI could do more than just answer questions?" — captures this trend perfectly.
It's worth noting upfront that the source material for this article is quite limited. The content comes primarily from a brief short-form video with poor audio transcription quality (including noise from Telugu transcription), making it difficult to extract complete product names, feature details, or demonstration flows. The analysis below draws on recognizable cues from the material, supplemented with relevant industry context.
Identifiable Clues from the Source Material
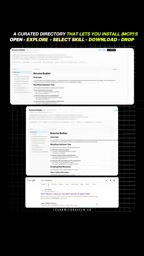
From the transcribed fragments, a few key terms are discernible: "skills," "workflows," and references to "Claude," "Codex," and "agent." These terms point in a clear direction — the video appears to introduce a website or platform that supports skill libraries, workflow automation, and AI agents.
The mention of "handing a file off to an agent like Claude or Codex to handle" suggests the tool's core value proposition lies in letting AI agents directly manipulate files and execute tasks, rather than simply holding a conversation. This is a hallmark of the current Agentic AI wave.
Agentic AI: From Conversation to Action
Regardless of which specific product is featured, the trend this material reflects is both real and significant. Traditional large language models operate on a "you ask, I answer" model. Agentic AI, by contrast, aims to enable models to:
Autonomously Invoke Tools
Agents can connect to external tools and APIs — reading and writing files, executing code, browsing the web — upgrading "answering" to "completing." The material's mention of handing files to a Claude or Codex-style agent is a direct example of this capability.
Claude is a family of large language models developed by Anthropic, known for safety and instruction-following; Codex is OpenAI's code-specialized model and the backbone of GitHub Copilot. Both have been integrated into various agentic frameworks as "reasoning cores" that interpret user intent and decide on next steps. When these models are combined with function calling / tool use capabilities within an agent framework, the model no longer just outputs text — it can output structured "action instructions" that the framework layer actually executes, such as creating files, running scripts, or calling third-party APIs. This division of labor — where the model handles reasoning and the framework handles execution — is the foundational paradigm of mainstream agent architectures today.
Orchestrate Workflows
The word "workflows" suggests the platform allows users to chain multiple steps into automated pipelines. Users simply define a goal, and the agent breaks the task into steps and executes them sequentially, minimizing manual intervention.
Workflow orchestration is one of the core challenges of agentic systems. Simple tasks can be handled sequentially by a single agent, but complex tasks often require multiple agents working in parallel: one for information retrieval, one for code generation, one for result validation. Leading implementation frameworks include LangGraph, AutoGen, and CrewAI, which provide directed graph or role-playing mechanisms to coordinate execution order and information flow across multiple agents. For users, the value of workflows lies in "define once, reuse repeatedly" — encoding domain expertise into shareable, automated pipelines rather than re-explaining the task context to an AI every single time.
Reuse Skill Modules
"Skills" typically refer to reusable capability modules. Similar to installing plugins for an AI, users can configure specific skills for their agents, enabling more specialized performance in targeted scenarios.
What to Look for in These Tools
If you're interested in AI tools that move beyond Q&A toward execution, here are the key factors worth evaluating when selecting or adopting one:
- Security boundaries: When AI can directly manipulate files and execute code, permission controls and sandbox isolation become critical.
- Controllability: Are the agent's actions transparent, auditable, and reversible at each step?
- Integration ecosystem: Does it support leading models (such as Claude, OpenAI's lineup) and common toolchains?
- Workflow reusability: Can defined workflows be saved, shared, and version-controlled?
Closing Thoughts
AI tools are undergoing a transformation from "information assistant" to "task executor" — one of the most important directions in the industry right now. While the source material is fragmented, the question it raises is highly representative of this moment. As agentic technology matures, both everyday users and developers will gain significantly stronger automation capabilities — provided we can establish the corresponding safety and controllability safeguards along the way.
Note: Due to the poor transcription quality of the source material, this article cannot confirm the specific product name or full demonstration details shown in the video. The conclusions presented here are supplemented with industry context based on identifiable cues.
Background: Key Concepts
Sandboxing refers to confining the execution of code or processes to a controlled environment, preventing access to sensitive resources on the host system. In AI agent scenarios, this mechanism is especially critical: when a model generates and executes code, the absence of isolation could allow malicious or erroneous code to delete files, leak credentials, or even laterally attack other systems. Common sandbox approaches include containerization (Docker), WebAssembly runtimes, and cloud-based sandbox services purpose-built for AI code execution (such as E2B and Modal). The principle of least privilege is equally important — agents should only be granted the minimum permissions necessary to complete the current task, and should prompt the user for confirmation before any sensitive operation, rather than executing silently.
Related articles

Amphibious Transforming Drone: Beyond 100x Power Savings, What Are the Real Needs?
Is the amphibious transforming drone just a gimmick? Starting from the 100x power difference of the M4 Morphobot, explore real application scenarios and thesis topic ideas, analyzing boundary conditions where pure drones and pure ground robots both fail.

Warhound Raises $200 Million: Genetically Engineered "War Dogs" Paired with Anduril Gear
Warhound raises $200M, backed by Ben Lamm and Palmer Luckey, to genetically engineer dogs for military and law enforcement use and equip them with Anduril gear. This article analyzes its technology direction, funding logic, and ethical controversy.

Claude API Comes to Google Cloud: IAM Integration and SDK Access Guide
Anthropic hosts the full Claude API on Google Cloud with IAM-controlled permissions and unified billing. This guide covers the Vertex AI and Anthropic-hosted entry points, IAM role configuration, and SDK access.