AI Safety by Design: European Scientists and Policymakers in Dialogue

Europe advances safe-by-design AI, embedding safety at the design stage through a science-policy coupled governance path.
Starting from a social media post, the article discusses the dialogue between European scientists and policymakers in Berlin and Zurich on safe-by-design AI. It explains the concept's core—systematically embedding safety, privacy, and ethics into model architecture, data pipelines, training, and deployment rather than post-hoc compliance—and links it to the EU AI Act's risk-tiered framework. It analyzes the symbolic choice of Berlin and Zurich as a policy hub and a research center, reflecting tight science-policy coupling. It also notes implementation challenges including missing technical standards, governance balancing difficulties, and interdisciplinary collaboration costs, and discusses implications for global AI governance and the innovation-safety tension.
European AI Safety Dialogue: From Concept to Action
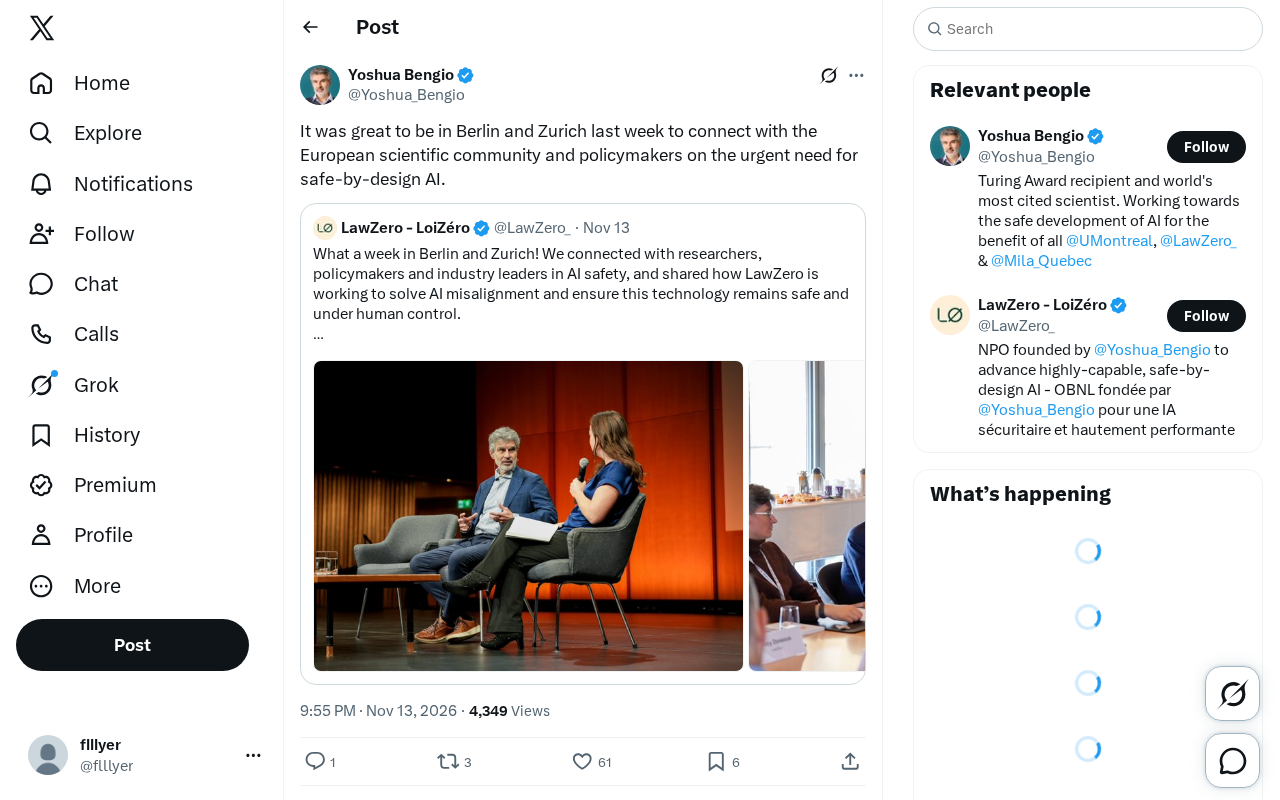
Last week, a social media post drew attention in the AI safety field. The author had been in conversation with European scientists and policymakers in Berlin and Zurich, with the core topic being the urgency of "safe-by-design AI." Behind this brief message lies a distinctive European approach to AI governance—embedding safety considerations into the technology design phase rather than remediating afterward.
Although the original material is limited, we can interpret the deeper meaning of this development by situating it within the broader context of European AI regulation.
What Is Safe-by-Design AI?
Safe-by-design is not a new concept; it has long been practiced in engineering and software, emphasizing the embedding of safety mechanisms from the very beginning of system design. In the AI context, this means systematically integrating safety, privacy, and ethical considerations into model architecture, data pipelines, training processes, and deployment.
Unlike the traditional "compliance-after-the-fact" approach, safe-by-design requires developers to proactively identify risks at every node of the product lifecycle. For example, considering bias when selecting training data, incorporating adversarial testing into model evaluation, and establishing human oversight mechanisms at the deployment stage. This front-loaded thinking is consistent with the risk-tiered framework of the EU AI Act.
The EU AI Act's risk-tiered framework is key background for understanding the policy context of safe-by-design. The Act, which formally entered into force in 2024, adopts a four-tier risk classification: unacceptable risk (e.g., social scoring systems, which are directly prohibited), high risk (e.g., medical diagnosis, recruitment screening, critical infrastructure, which must meet strict compliance obligations), limited risk (e.g., chatbots, which must fulfill transparency obligations), and minimal risk (e.g., spam filtering, which is largely unconstrained). For high-risk AI systems, the Act requires establishing a risk management system, data governance mechanisms, technical documentation, and human oversight arrangements at the design stage, and undergoing conformity assessment. This framework moves compliance obligations upstream to the development phase, aligning closely with the safe-by-design philosophy and providing a legal vehicle for translating "safety by design" from principle into enforceable standards.
Europe's Two-City Dialogue: Why Berlin and Zurich?
The choice of Berlin and Zurich is no coincidence. Berlin is a key hub for European policymaking with an active tech policy discussion culture; Zurich is home to leading European research institutions (such as ETH Zurich) with deep accumulations in fundamental AI research and safety.
Bringing scientists and policymakers together in these two cities reflects a key feature of European AI governance: tight coupling between science and policy. Policymaking requires scientific evidence, while research directions are guided by policy frameworks. This two-way interaction helps prevent regulation from drifting away from technological reality and keeps innovation from ignoring social risks.
According to the post, the focus of the exchange was "urgent need." This hints at the tension between rapidly evolving AI capabilities and lagging safety measures. European scientific and policy circles appear to be forming a consensus: safety cannot be an add-on; it must be a design prerequisite.
Practical Challenges of Safe-by-Design AI
Although consensus is coalescing, implementation faces multiple challenges.
Technical Level
How do you quantify "safety"? There is currently a lack of unified evaluation benchmarks and testing standards. Risk profiles vary enormously across AI application scenarios, making it difficult for generic frameworks to cover all cases. Moreover, safety by design may increase development costs and timelines, putting pressure on startups.
Adversarial testing is one of the core instruments of safe-by-design at the model evaluation stage. It deliberately constructs perturbed inputs—for example, adding noise imperceptible to the human eye to images, or paraphrasing text or injecting prompts—to probe whether a model will produce erroneous outputs or be bypassed past safety guardrails. In safety design, adversarial testing is used not only to discover vulnerabilities but also to verify the effectiveness of defenses, forming an iterative loop of "attack—fix—retest." The main obstacles today are that adversarial samples tend to be highly dependent on specific models and tasks, making universal benchmarks difficult to establish, and there is a lack of industry consensus on the coverage and reproducibility of red-team testing. This is precisely one concrete manifestation of the "lack of unified evaluation benchmarks" mentioned in the article.
Governance Level
Policymakers must balance regulatory intensity with innovative vitality. Overly strict design specifications may suppress experimentation, while overly loose ones cannot prevent risks. Europe attempts to find a middle ground through risk tiering and sandbox mechanisms, but implementation details are still evolving.
Regulatory sandboxes are an institutional tool Europe uses to try to balance safety and innovation. The basic idea: in a controlled environment authorized by regulators, companies are allowed to test innovative AI products for a limited period while being exempted from some routine compliance obligations, and regulators accumulate evidence and adjust rules by observing actual operation. The EU AI Act requires each member state to establish at least one AI regulatory sandbox, prioritizing startups and SMEs. The value of the sandbox mechanism lies in institutionalizing "safety validation at the design stage"—developers can test model behavior in a real but limited-risk environment rather than relying solely on static document review. However, the resource capacity, admission criteria, and cross-member-state mutual recognition of sandboxes remain difficult points in implementation, and their actual effectiveness remains to be seen.
Interdisciplinary Collaboration
Safe-by-design AI requires the joint participation of computer scientists, ethicists, legal experts, and domain experts. Such collaboration faces organizational challenges of communication costs and goal alignment.
Implications for Global AI Governance
Europe's push for safe-by-design AI has reference significance for global AI governance. It proposes a path different from "develop first, govern later," emphasizing the precautionary principle.
However, this path is also contested. Critics argue that overemphasizing safety at the design stage may delay the deployment of beneficial applications and, in the context of global competition, may weaken Europe's AI industry competitiveness. Supporters counter that trust is a prerequisite for widespread AI adoption and that safety by design ultimately benefits the sustainable development of the innovation ecosystem.
As can be seen from this brief social media post, the dialogue between European scientists and policymakers is ongoing. This dialogue itself is an important step toward building a trustworthy AI ecosystem. For practitioners concerned with AI governance, tracking Europe's practice will provide key clues for understanding global regulatory trends.
One-line Summary
Europe advances safe-by-design AI, embedding safety at the design stage, reflecting a governance path of science-policy coupling.
Paragraph Summary
The article starts from a social media post and discusses the dialogue between European scientists and policymakers in Berlin and Zurich around "safe-by-design AI." The author explains the core of the concept: systematically embedding safety, privacy, and ethical considerations into model architecture, data pipelines, training, and deployment, rather than compliance after the fact, and links it to the EU AI Act's risk-tiered framework. The article analyzes the symbolic significance of choosing Berlin and Zurich—the combination of a policy hub and leading research institutions, reflecting tight science-policy coupling. It also points out that implementation faces challenges such as missing technical standards, governance balancing difficulties, and interdisciplinary collaboration costs, and discusses the reference significance of this path for global AI governance and its controversy over the tension between innovation and safety.
Related articles

Gemini 4 Hydrogen vs Sonnet Comparison Test: Uses Only 1% of Weekly Quota, Performance on Par
Hands-on test: Gemini 4 Hydrogen vs Sonnet on the same CRUD task—Hydrogen used only 1% weekly quota with comparable performance and better UI details, while Anthropic's model used 7%. Developer says daily tasks don't require expensive models.

Gemini 4 Neon Released: Beats Opus 5.5 on Multiple Benchmarks, Google Returns to the Top Tier
Google DeepMind releases Gemini 4 Neon: 61 on the Artificial Analysis intelligence index (3rd) and 1st on the coding index, beating Opus 5.5 on multiple benchmarks. $3/$15 per million tokens; available in the Gemini API and AI Studio.
Gemini 4 Neon Review: Benchmark Scores Rival Carbon, API Cost-Performance Analysis
Full review of Google Gemini 4 Neon: benchmark scores rival Carbon, API priced at 2x Hydrogen, yet Antigravity quota consumption is only 1x (vs Carbon's 3x). Real tests show it replaces 90% of Carbon use cases. Includes channel restrictions, ban risks, and combination strategy analysis.