Cairn: Making AI-Driven Cyber Operations Transparent
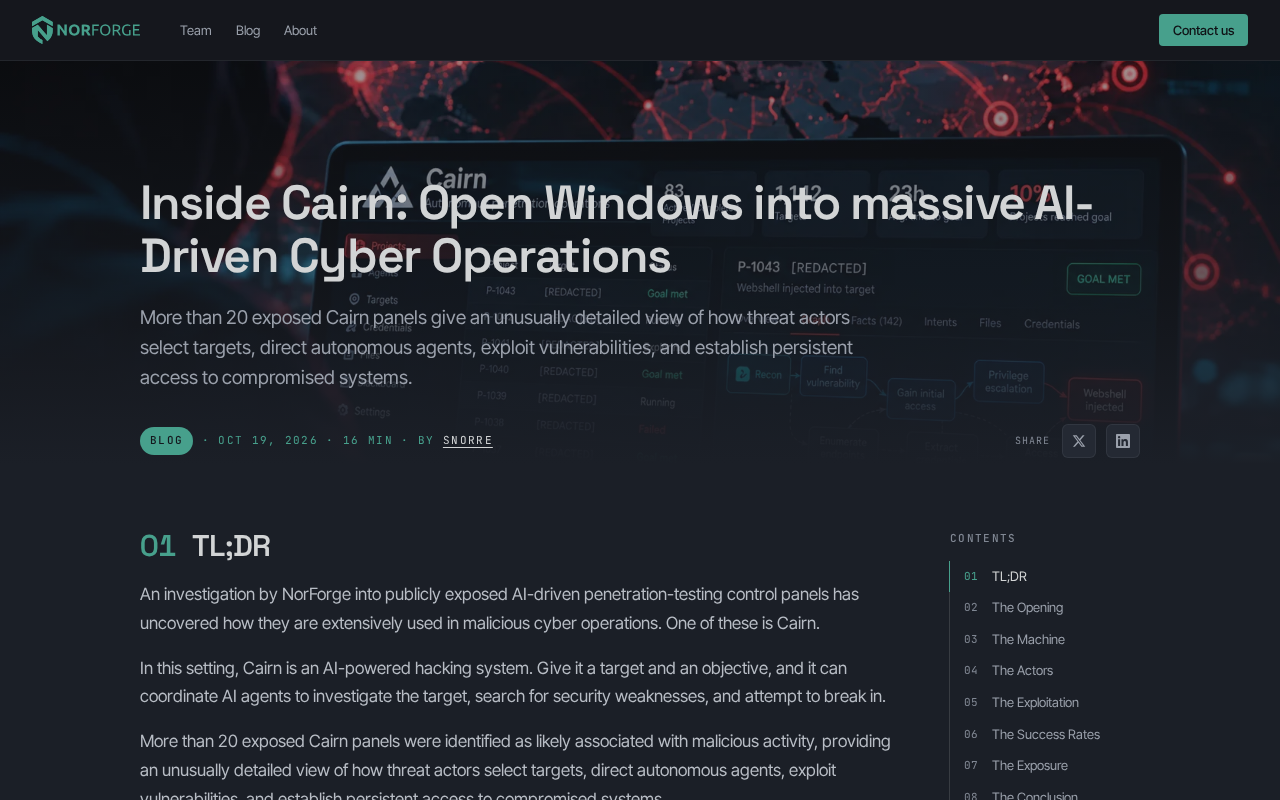
The Cairn project attempts to provide an "open window" of observability and auditing for AI cyber operations.
This article introduces Cairn, an early project on Hacker News positioned as an observation and auditing framework for AI-driven cyber operations. Its core value is making AI's decision chains, behavioral boundaries, and anomaly signals traceable and explainable, rather than showcasing AI capabilities. The article notes that traditional logs record "what happened," while Cairn focuses more on "why AI did it this way," filling the evidence chain gap after AI intervention. Transparency itself is also a constraint, and observable AI cyber operations make responsibility attribution easier. The project has low visibility, and its observation granularity, performance overhead, and standardization level remain to be verified. The article concludes that the focus of AI security tools is shifting from "capability" to "governance," and observability may become a key dimension of future product competition.
When AI Starts Participating in Cyber Offense and Defense, What Can We See?
In cybersecurity, AI applications are no longer a novel topic. But most discussions remain at the binary level of "can AI find vulnerabilities" or "will AI attack autonomously," lacking an observation window into the intermediate process. A project called Cairn that appeared on Hacker News attempts to answer a more specific question: when AI intervenes in cyber operations, can we see what's happening inside as clearly as opening a window?
The core value of this project lies in "visibility"—not showcasing how powerful AI is, but making AI's decision chains, behavioral boundaries, and anomaly signals in cyber operations traceable and explainable. For security researchers and operations personnel, this transparency has more practical significance than mere performance metrics.
What Cairn Is Actually Doing
Based on currently disclosed information, Cairn positions itself as an observation and auditing framework for AI-driven cyber operations. It doesn't directly participate in attacks or defense, but serves as a "recording layer": when AI systems execute tasks in network environments, Cairn captures state changes at key nodes, decision rationale, and output results, presenting them in some visual or structured manner.
This design approach is fundamentally different from traditional log auditing. Traditional logs record "what happened," while Cairn focuses more on "why AI did it this way." In AI-participated cyber operations, a scan, a probe, a response may involve model inference, policy selection, and confidence assessment behind the scenes. If these intermediate processes are invisible, security teams can hardly judge whether AI behavior meets expectations, let alone intervene in time when deviations occur.
Interestingly, the project received relatively low attention on Hacker News (11 points, 3 comments), which may indicate it's still in an early stage or has a relatively vertical target audience. But the "open window" metaphor itself is worth pondering—it implies an attitude: AI cyber operations should not be a black box, but a process that can be observed, questioned, and audited.
Why "Observability" Is So Critical in AI Cyber Operations
Trust Cannot Rely on Promises; It Must Rely on Records
In traditional security operations, analysts rely on firewall logs, IDS alerts, and endpoint telemetry to reconstruct event chains. When AI takes over some decisions, this evidence chain develops a gap: the model produced an action, but the reasoning behind it is often invisible. Cairn attempts to fill exactly this gap.
For enterprise security teams, this means two things. First, AI behavior can be traced and reviewed, rather than only seeing final results. Second, when AI makes unexpected operations, the team has a basis to determine whether it's a model issue, data issue, or policy configuration issue. Without this layer of observability, AI security tools can hardly truly enter production environments.
Open Windows Are Also Boundaries of Responsibility
The expression "Open windows" carries another layer of meaning: transparency itself is a constraint. When AI cyber operations are in an observable state, developers and administrators will set permissions and boundaries more carefully. Conversely, if the system is inherently unobservable, responsibility attribution becomes ambiguous—when problems arise, is it the model's fault, the data's fault, or the user's fault? The emergence of tools like Cairn is actually pushing AI cyber operations toward "accountable" engineering practices.
Observability originates from control theory, referring to the degree to which a system's internal states can be inferred solely from external outputs. In software engineering, it typically consists of three pillars: Logs, Metrics, and Traces, distinguished from traditional "monitoring"—monitoring answers "whether the system is normal," while observability answers "why the system is abnormal." For AI systems, observability also involves exposing internal signals such as model reasoning chains, confidence distributions, and feature importance. Without these signals, operations personnel can only see inputs and outputs, unable to locate the source of deviations. In cyber operation scenarios, observability requires recording the context of each probe, scan, or response, including trigger conditions, model versions, and policy rules, thereby forming a complete evidence chain.
Accountability is one of the core principles of AI governance, referring to the ability to attribute system behavior to specific responsible entities (developers, deployers, or users). In engineering practice, accountability relies on audit logs, decision records, and version tracing. For AI-driven cyber operations, if the system is unobservable, once false positives, privilege escalation, or accidental damage occur, it becomes difficult to distinguish whether it's a model defect, data bias, or configuration error. Tools like Cairn provide a basis for post-incident review and responsibility determination by recording decision rationale and operational boundaries, thereby advancing "accountable AI" from principle to operable engineering practice.
Signals and Limitations of Early Projects
Judging from the discussion heat on Hacker News, Cairn currently appears more like a proof of concept or early prototype. 3 comments mean the community has not yet formed in-depth technical discussion, and there's a lack of third-party reproduction or comparative evaluation. For readers interested in this direction, several questions deserve continuous observation:
- Observation granularity: To what level can Cairn record? Does it only record inputs and outputs, or can it capture the model's internal reasoning paths?
- Performance overhead: In cyber operation scenarios, will the additional observation layer introduce latency or affect task execution?
- Standardization level: Does it define universal data formats, and can it integrate with other security toolchains?
- Applicable boundaries: Is it aimed at red team exercises, blue team defense, or both?
These questions currently have no public answers, but they determine whether Cairn will ultimately be a "demonstration project" or "deployable infrastructure."
Hacker News points and comments are common signals for measuring community attention to early projects. Points reflect the number of votes a post receives, while comment count reflects discussion depth. Typically, projects with over a hundred points and dozens of comments enter broader technical visibility; while 11 points and 3 comments indicate the project has only been noticed within a very small scope, possibly in the proof-of-concept stage, not yet reproduced or comparatively evaluated by the community. For security tools, the lack of third-party validation means its effectiveness, performance, and applicable boundaries remain unknown, and readers should treat it as a signal rather than a conclusion.
Implications for the AI Security Tool Ecosystem
Cairn's emergence reflects a broader trend: the focus in AI security is shifting from "capability" to "governance." Over the past few years, substantial effort has been invested in making AI more accurately identify threats and respond to incidents faster; now, how to make AI behavior explainable, auditable, and controllable is becoming an equally important topic.
This shift has direct implications for product design. Future AI security tools may no longer compete solely on detection rates or response speeds, but also on "observability"—whoever can provide clearer decision trajectories, more granular audit records, and more user-friendly intervention interfaces will be more easily accepted by cautious enterprise customers. Cairn's "open window" philosophy is precisely an early exploration in this direction.
Of course, an early project is not enough to define a track. But the questions it raises are specific enough: when AI operates in cyberspace, are we prepared with tools to observe it? If the answer is no, then attempts like Cairn deserve to be recorded and discussed.
Related articles
WorkBuddy Mini Program Development in Practice: A Complete Guide to No-Code Building and Monetization
Based on a Bilibili creator's paid course, this guide covers WorkBuddy no-code WeChat mini program development: capability boundaries, five use cases, three cost calculations, three getting-started paths, and a six-element prompt template with monetization workflow data.
What Is an AI Agent? Build Your First Intelligent Agent for Free with Zero Code
What's the difference between an AI Agent and a Chatbot? Learn the four core elements of an Agent and build your first AI research assistant for free with zero code using ChatGPT and Make/n8n—safe and fully under your control.
Harness² Explained: Letting Agents Evolve Their Own Harness Without Training Models
Google Research and Northwestern's Harness² shows Agents can self-evolve their harness at runtime, letting small models beat stronger ones on default harnesses.