Datasette 0.65.6 Released: Fix for Database Route Permission Bypass Vulnerability

Datasette 0.65.6 backports a security fix for unauthorized database downloads caused by custom routes.
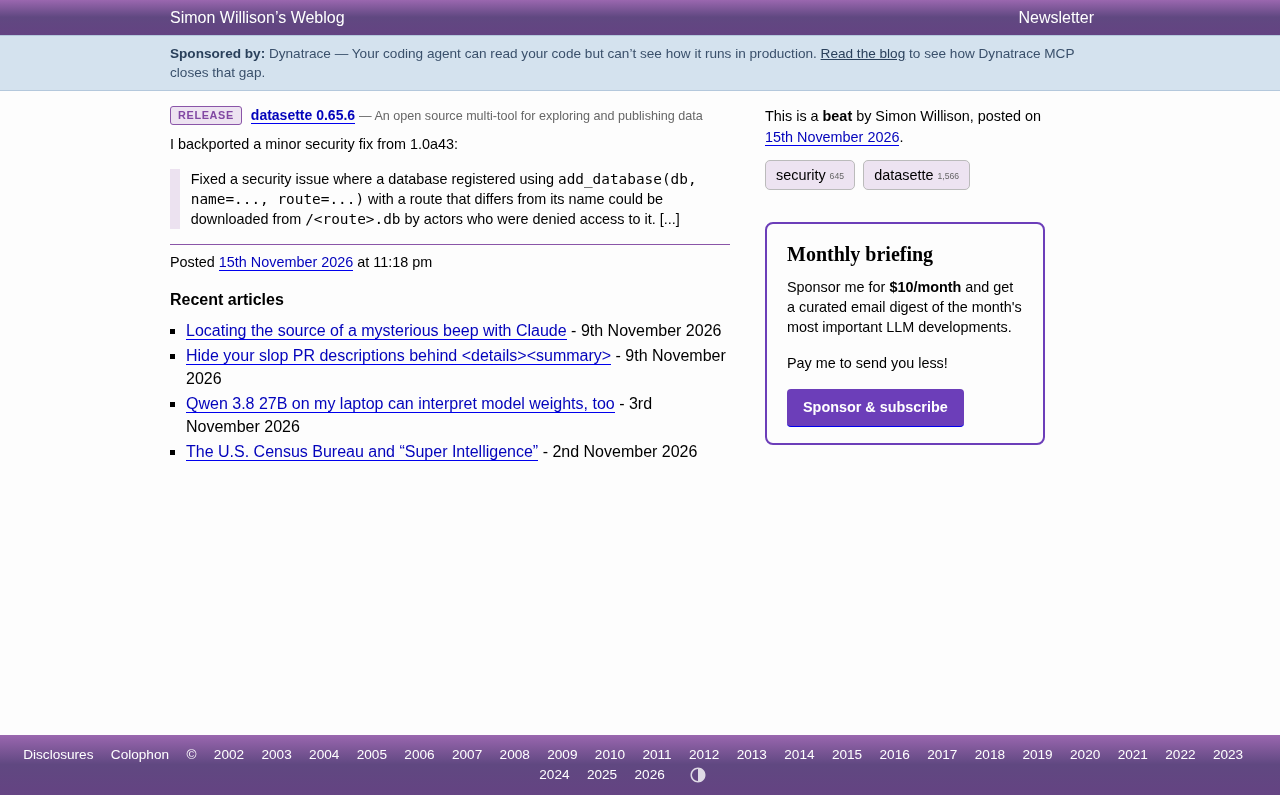
Datasette creator Simon Willison has released version 0.65.6, a minor release focused on security fixes. This version backports a minor security fix from the 1.0a43 branch, resolving an issue where databases could be downloaded without authorization under certain configurations. The vulnerability exists in the `add_database(db, name=..., route=...)` interface: when `route` and `name` do not match, permission checks are bound to the name while the download endpoint follows the route, allowing denied actors to download the full database file via `/<route>.db`. Official advice is to upgrade deployments using custom `route` to 0.65.6 immediately; after upgrading, the download endpoint will correctly follow permission decisions. This backport also reflects the maintainers' emphasis on security consistency between the stable branch and the 1.0 preview branch.
Datasette creator Simon Willison has released version 0.65.6, a minor release focused on security fixes. This version backports a minor security fix from the 1.0a43 branch, resolving an issue where databases could be downloaded without authorization under certain configurations.
Vulnerability Details: Route and Name Mismatch Leads to Permission Bypass
According to the official release notes, the vulnerability exists in the add_database(db, name=..., route=...) registration interface. When developers register a database, if the explicitly specified route parameter does not match the database's name, even if an actor is denied access to that database, it can still download the complete database file via the /<route>.db path.
In other words, permission checks are bound to the database name, while the download endpoint follows the route. Once these two are misaligned, a bypass channel is formed. For multi-tenant Datasette deployments or those requiring fine-grained permission control, this is an issue that needs to be patched as soon as possible.
Datasette's permission model is based on binding actors (i.e., authenticated request principals) to resources (databases, tables, rows, etc.). By default, a database's identifier is its name parameter, and permission checks (such as allow blocks or plugin hooks) are evaluated against that name. The route parameter, however, is used to customize the mount path of that database in the URL, for example mapping /mydb to the actual /data path. When the two do not match, the download endpoint /<route>.db looks up the database file based on the route, but permission checks still use name as the key, causing the check result to not match the database the download request points to, thus forming a bypass.
Fix and Upgrade Recommendations
0.65.6 backports the fix from 1.0a43 to the stable branch, ensuring that users still on the 0.65.x series also receive the patch. The official release notes do not disclose further exploitation details, which is consistent with standard security fix practices.
If you use add_database calls with custom route in Datasette, it is recommended to upgrade to 0.65.6 immediately. After upgrading, the download endpoint will correctly follow permission decisions and will no longer leak database contents due to differences between route and name.
In Datasette's version branch strategy, 0.65.x is the stable maintenance series, while 1.0a43 belongs to the 1.0 alpha preview branch. Backporting refers to porting a patch already fixed in the preview branch to the stable branch, ensuring that users who do not want to upgrade to the 1.0 alpha also receive security updates. This practice is common in open-source projects that maintain multiple version lines simultaneously; security fixes are typically backported first to all supported stable versions.
The Signal Behind a Minor Release
Datasette has long been known for its plugin architecture and data publishing. Such permission boundary issues often arise at the intersection of flexible configuration and the security model. This backport also shows that maintainers will maintain security consistency across both the stable branch and the 1.0 preview branch. For teams relying on Datasette to provide datasets externally, paying attention to security advisories for such minor releases is more practical than waiting for major version updates.
Related articles

RePlan-VLA: Progress-Aware Replanning Breakthrough for Long-Horizon Robotic Manipulation
The RePlan-VLA framework converts VLA models' short-horizon capabilities into reliable long-horizon execution through progress-aware adaptive replanning, improving success rates by 21.9% and 10.4% on RoboCasa365 and CALVIN, and validating real-world deployment on a Franka Research 3 robot.

Geometric Bridge Flow Matching: A New Breakthrough in Blind Rigid Motion Correction
Geometric bridge flow matching enables blind rigid motion correction in head CBCT, achieving 37.1 dB PSNR and 0.27 mm RPE on simulated data in ~9.1 minutes, outperforming existing methods.

Google Releases Gemini 4 Hydrogen: 2.5x Faster Without Sacrificing Intelligence
Google releases the lightweight Gemini 4 Hydrogen: 2.5x faster task completion, AA Intelligence Index of 54 beating its flagship sibling, 7.3s single-step on Agent Arena faster than Claude and GPT rivals, four thinking levels with pay-as-you-need pricing, now available across AI Studio and more.