Estonia's Online Voting System Source Code Release Sparks Heated Debate

Estonia's i-Voting source code release sparks Hacker News debate on security and transparency, highlighting verifiability challenges.
Estonia's online voting system source code has sparked discussion on Hacker News, with the core controversy being whether election system implementation details should be public. Supporters say open source improves auditability; opponents worry about expanded attack surface. The article notes that trust in voting systems differs from ordinary software, requiring defense against external attacks, insider abuse, and untrusted clients. Estonia uses a double-envelope cryptographic scheme to separate ballot content from identity, but open source is only the first step—real trust relies on end-to-end verifiability, independent audits, and reproducible builds. The discussion's value lies in grounding e-voting feasibility in checkable technical facts.
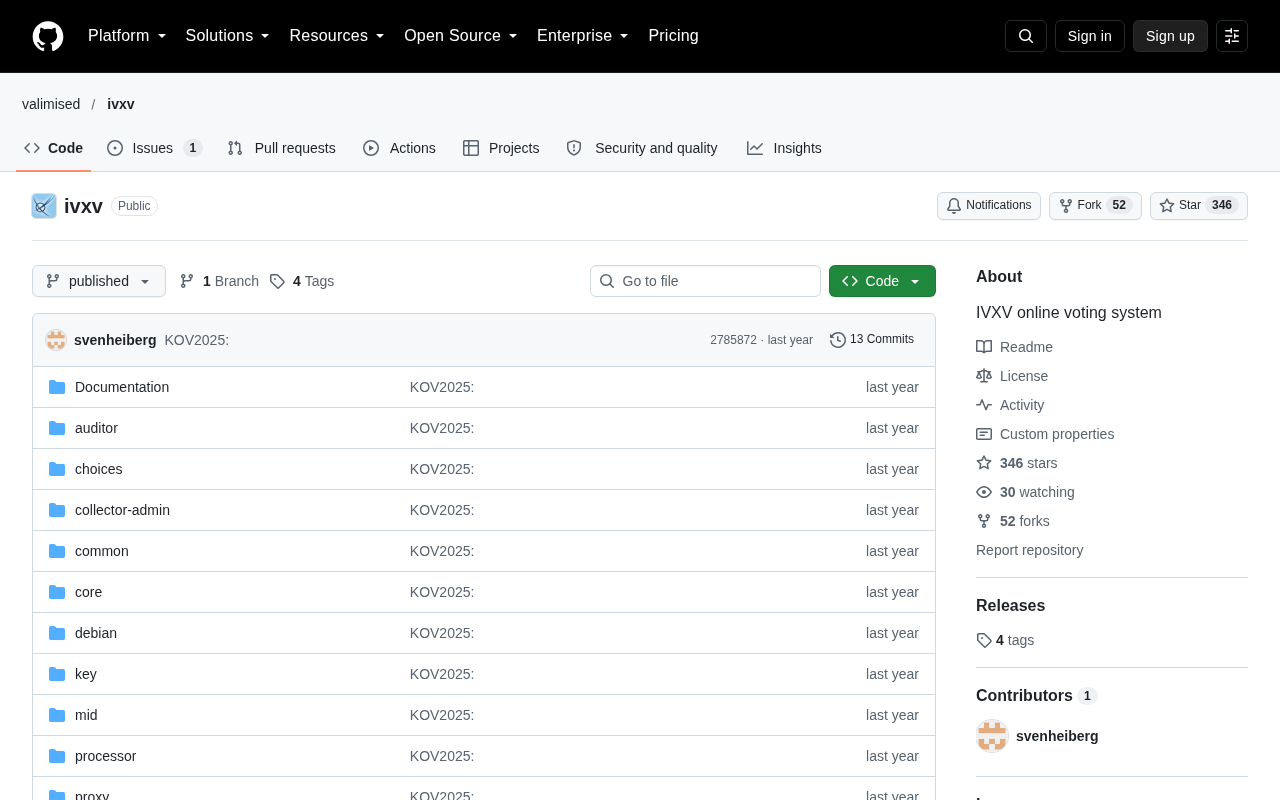
A Security Discussion Sparked by "Open Sourcing"
Estonia is known as the first country in the world to incorporate electronic voting (i-Voting) into its national election system, and its online voting system has long been a subject of observation in tech circles and public governance. Recently, content related to the system's source code was shared on Hacker News, immediately triggering intensive discussion among developers and security researchers.
The core of such discussions is not whether "Estonia has electronic voting," but a more fundamental question: should the implementation details of an election system be open to the public, and if so, how? For security researchers, auditability is the foundation of trust; for election authorities, the tension between expanding the attack surface and the tradition of confidentiality has always existed.
Why the Code of a Voting System Deserves Repeated Scrutiny
The Source of Trust for Voting Systems Differs from Ordinary Software
When ordinary software has a bug, what's lost is user experience and efficiency; when a voting system has a bug, what may be lost is the legitimacy of a government and public confidence in the system. This places the security requirements for i-Voting at an extreme level: it must simultaneously withstand external attacks, insider abuse, untrusted client environments, and long-term privacy leakage risks.
Estonia's i-Voting has used a double-envelope scheme based on public-key cryptography, separating voters' ballot content from their identity in an attempt to balance verifiability and anonymity. The significance of open source code is that it allows external researchers to independently check whether these cryptographic protocols are correctly implemented, rather than relying solely on official claims.
Double Envelope Scheme is a cryptographic voting protocol used by Estonia's i-Voting, whose core idea draws on the double-layer envelopes in traditional paper voting: voters place their ballot (inner layer) into an anonymous envelope, then place the anonymous envelope together with identity information into an outer envelope. In the electronic implementation, the ballot is encrypted with the election authority's public key to form the "inner envelope," and then signed with the voter's private key to form the "outer envelope." Before counting, the system first strips the outer signature to verify voter eligibility, then decrypts the inner ballot, thereby separating the ballot content while verifying identity, avoiding directly linking the ballot to the voter. This scheme relies on public key infrastructure (PKI) and strong identity authentication methods such as smart cards or mobile ID, and its security depends on key management, protocol implementation, and the trustworthiness of the client environment.
The Dilemma of Open Source Review vs. Expanded Attack Surface
This is precisely where the typical divergence of views on Hacker News unfolds. The faction supporting disclosure argues that the security of cryptographic systems should not be built on "no one has seen the code," and that security through obscurity is especially unacceptable for national-level systems; open source code allows researchers worldwide to participate in auditing, improving system resilience in the long run.
The faction with reservations points out that disclosing the complete implementation allows attackers to study the flaws of the specific implementation at low cost — the protocol itself may be secure, but details in the engineering implementation such as timing, random number sources, memory handling, and log remnants are often the real突破口. This divergence has no simple right or wrong; it reflects the ongoing game between "transparency" and "attack cost" in security engineering.
Reproducible Builds refers to the ability to reproduce, byte for byte, the same binary artifact from the same source code, build environment, and dependencies. In the context of electronic voting, its significance lies in the fact that even if the source code is public, if it cannot be confirmed that the binary actually running was indeed compiled from that source code, the value of open source auditing is greatly diminished. Reproducible builds allow independent third parties to verify the consistency between the officially released voting software and the public source code, thereby closing the loophole of "clean source code but tampered distribution." Achieving reproducible builds requires fixing the compiler version, eliminating uncertainties such as build paths and timestamps, and disclosing the complete build toolchain. Audit reports of Estonia's i-Voting have repeatedly emphasized the importance of reproducible builds, but full implementation still faces challenges of engineering complexity and supply chain transparency.
Verifiability: The Real Hard Nut of Electronic Voting
Even if the source code is fully public, ordinary voters cannot confirm that their vote was correctly counted by reading the code. What truly underpins trust is the end-to-end verifiability mechanism: voters can verify that their vote was recorded, correctly aggregated, and that the final result is consistent with all valid votes, without revealing the ballot content.
The complexity of this mechanism determines that publishing the source code is only the first step; the accompanying verification tools, independent observer reports, and audit processes understandable to non-experts together form a complete chain of trust. Publishing code alone without providing reproducible builds and verification paths would greatly diminish its transparency value.
From a broader perspective, Estonia's i-Voting source code and design documents have become indispensable reference material for global discussions on the feasibility of electronic voting. It proves that national-level electronic voting can work in engineering terms, and also exposes the long-term challenges of this approach in verifiability and trust communication. The value of continued scrutiny of this code lies not in reaching a conclusion of "secure or not," but in grounding the discussion in checkable technical facts.
End-to-End Verifiability (E2E-V) is a security property of electronic voting systems that requires the election process to be independently verifiable at three levels: cast-as-intended, meaning voters can confirm that their encrypted ballot content matches their intent; recorded-as-cast, meaning voters can confirm that their ballot was correctly recorded by the system; and tallied-as-recorded, meaning anyone can verify that the final result was correctly aggregated from all recorded ballots without revealing the content of any individual ballot. Implementing E2E-V typically requires cryptographic techniques such as zero-knowledge proofs, mix-nets, or homomorphic encryption, along with verification tools available to voters (such as mobile apps or paper tracking codes). Estonia's i-Voting did not fully implement E2E-V in its early versions and gradually introduced related mechanisms later, but the academic community continues to discuss the scope of its verification coverage.
Frequently Asked Questions
Is Estonia's online voting system source code public? Yes, the system's source code has been made public for researchers and the public to review, which is also why it continues to be discussed in the tech community.
Does publishing the source code make the voting system less secure? This is the focus of the controversy. Disclosure improves auditability and long-term resilience but also lowers the cost for attackers to study implementation details. Most security researchers tend to believe that for cryptographic systems, the benefits of auditability outweigh the risks.
What does trust in electronic voting rely on? Not only on open source code, but also on end-to-end verifiability mechanisms, independent audit reports, reproducible builds, and transparent observation processes.
One-line Summary
Estonia's i-Voting source code release sparks debate on Hacker News about security and transparency, highlighting verifiability challenges.
Paragraph Summary
Estonia's online voting system source code has sparked discussion on Hacker News, with the core controversy being whether the implementation details of an election system should be made public. Supporters argue that open source improves auditability, while opponents worry about expanding the attack surface. The article points out that trust in voting systems differs from ordinary software and must withstand risks such as external attacks, insider abuse, and untrusted clients. Estonia uses a double-envelope cryptographic scheme to separate ballot content from identity, but publishing source code is only the first step; real trust depends on end-to-end verifiability mechanisms, independent audits, and reproducible builds. The value of the discussion lies in grounding the feasibility of electronic voting in checkable technical facts.
Related articles

Automate Job Search with AI Agents and Residential Proxies for Precise Matching
Build an AI Agent with MCP and residential proxies to bypass recruitment site anti-scraping and geo-restrictions, scrape thousands of DevOps jobs, then have Claude score and rank each against your resume. Includes proxy comparison experiments, project structure, and cost analysis—filtering only, no auto-submission.

The AI Task Assistant That Knows When to Back Off: A Cure for Activation Struggles
One Small Step is an AI assistant for task initiation struggles, using agentic decisions for guilt-free reminders, timely retreat, and cross-platform task management. The developer shares real test results on 13 tasks and architectural trade-offs.

FastAPI: A High-Performance Python Framework and a Production-Ready API Development Powerhouse
FastAPI is a high-performance web framework based on Python type hints, supporting async and automatic OpenAPI docs. With over 100k GitHub stars, this article analyzes its core strengths, production readiness, and selection advice.