Fake Claude Code Plugin Infiltrates Cursor Marketplace: A Wake-Up Call on AI Editor Supply Chain Risks
A malicious plugin impersonating Claude Code was listed on Cursor for 11 hours, exposing AI editor plugin supply chain risks and the need for pre-installation verification.
A malicious extension impersonating Claude Code was listed on Cursor's official marketplace for about 11 hours, planting a remote login key and scripts that persisted after uninstallation. Cursor said the stranger's remote login would generally fail, but the plugin still exfiltrated information such as the computer name. The core issue is that same-name camouflage exploited users' default trust in marketplace names. The article further notes that Claude Code plugins can also execute code locally, and that Hooks and MCP servers can run programs autonomously. Before installation, users should review the Will Install list, audit commands in hooks.json and .mcp.json, and cross-check with NVIDIA SkillSpecter; if it is still unclear what the plugin will run, skip it. The AI editor extension ecosystem is replicating traditional software supply chain problems, but with higher permissions and greater risk.
Title
Fake Claude Code Plugin Infiltrates Cursor Marketplace: A Wake-Up Call on AI Editor Supply Chain Risks
Meta Description
A malicious plugin impersonating Claude Code was listed on the Cursor marketplace for about 11 hours, planting a remote login key and persistent scripts. This article reconstructs the incident and provides pre-installation checks for Claude Code plugins: review the Will Install list, audit hooks.json and .mcp.json, and scan with NVIDIA SkillSpecter.
Article Content
A malicious plugin impersonating Claude Code was listed on Cursor's official marketplace for about 11 hours. The attacker used a same-name extension to plant a remote login key and scripts that persist even after uninstallation. Although the incident did not cause widespread account compromise, it brought the plugin supply chain risks of the AI editor ecosystem into the spotlight.
Incident Recap: An 11-Hour Same-Name Trap
According to a YouTube video, on October 29, an editor extension with the same name as the official plugin appeared in the Cursor marketplace. The publisher was not Anthropic but a third-party attacker. The extension remained in the marketplace for about 11 hours.
The plugin did two things: first, it added a key that allowed a stranger to log in remotely; second, it planted scripts that remained even after uninstallation. Cursor's response was that the stranger's remote login "would generally fail," but the plugin still exfiltrated details such as the computer name. In other words, even if the login step was blocked, information leakage had already occurred.
For users who installed the extension in Cursor that day, the video's advice was straightforward: regardless of anything else, follow Cursor's security advisory and perform a cleanup.
Why a Same-Name Plugin Can Fool Users
The core issue in this incident is not how sophisticated the attack was, but that it exploited a blind spot everyone takes for granted: a familiar name in the marketplace does not tell you what the plugin actually does.
As an AI code editor, Cursor's extension marketplace follows the trust model of traditional IDEs—users see the name, icon, and description and assume it is official. The attacker used "same name" as camouflage, trading minimal cost for installation volume. An 11-hour window is not long, but for a developer-facing tool marketplace, it is enough to complete a round of distribution.
One detail worth noting: this incident targeted a Cursor editor extension, not a Claude Code plugin. But the video specifically warns that the risk boundaries between these two categories are becoming blurred.
Trust Model refers to the fundamental assumptions in system design about "who is trusted" and "how trust is established and transmitted." Traditional IDE plugin marketplaces and mobile app stores generally adopt a "platform review + user identification" trust model: the platform is responsible for vetting before listing, and users rely on signals such as name, icon, and download count to judge authenticity. This model implies a premise—listed content has undergone basic security review. But AI editor marketplaces are expanding rapidly, and review often lags behind plugin growth. Attackers therefore use "same name" to bypass the user's identification step at low cost. Once the trust model is silently broken, users still act according to old habits, and risk arises.
Claude Code Plugins Can Also Execute Code
Anthropic's documentation clearly states that Claude Code plugins can also run code on the user's computer. This breaks the illusion held by many that "plugins are just configuration files."
In Claude Code, users can view details by entering the slash command plugin and selecting a plugin. Before installation, the interface displays a section titled "Will Install," listing what the installation will bring.
Three types of content are key to watch:
- Skills: used to guide Claude's behavior;
- Hooks: can run programs on their own;
- MCP servers: also have the ability to execute programs autonomously.
What truly warrants vigilance is Hooks and MCP servers. The video's assessment method is: check whether the installation preview lists Hooks, or whether there is no list at all. If there is, open the plugin's code repository and read the commands in hooks.json and .mcp.json one by one. These two files are where the plugin's actual execution logic resides.
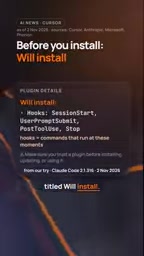
Hooks are lifecycle hook mechanisms in Claude Code plugins that allow plugins to automatically execute preset programs when specific events occur (such as before or after tool calls, or at session start or end). The essential difference from ordinary configuration files is that configuration files only describe behavior, while Hooks directly run local commands, thus possessing the same file and network access permissions as the user account. If an attacker writes malicious commands into hooks.json, the plugin can execute them in the background once installed, without the user actively triggering anything. This is also why Hooks should be prioritized in security review—it turns a "plugin" from a passive descriptor into an active executor.
MCP (Model Context Protocol) is an open protocol proposed by Anthropic for letting AI assistants connect to external tools, data sources, and services in a standardized way. An MCP server is the server-side program implementing this protocol; it can run locally or remotely and exposes callable tool interfaces to Claude. The problem is that an MCP server is itself an independent process with the ability to execute programs autonomously. Plugins declare which servers to start and what parameters to pass via .mcp.json. If the declaration contains a malicious server or tampered startup commands, the plugin gains a channel to run arbitrary code on the user's machine. Therefore, reviewing .mcp.json is as important as reviewing hooks.json.
Three Checks Before Installation
For plugins that cannot be fully trusted, the video offers three layers of verification, from light to heavy.
The first layer is the installation preview. Use Claude Code's "Will Install" list to first confirm which components the plugin will introduce, especially whether Hooks and MCP servers are present.
The second layer is source code review. Open the repository directly and read the command contents in hooks.json and .mcp.json. This step requires some technical judgment, but it is the only way to see what the plugin "actually does" rather than what it "claims to do."
The third layer is automated scanning. NVIDIA's free tool SkillSpecter can scan plugin files for risk patterns as an additional cross-check.
If after all three steps you still cannot clearly explain what the plugin will run, the video's advice is: skip it. This criterion may seem conservative, but for a tool with access to your local code and credentials, caution is a reasonable default.
Supply Chain Trust Needs Recalibration
Looking at the Cursor incident together with Claude Code's plugin mechanism reveals a common trend: the extension ecosystem of AI programming tools is replicating the old problems of the traditional software supply chain, but with higher risk factors.
Traditional IDE plugin permissions usually have relatively clear boundaries, whereas AI editor plugins often need to read project context, call external services, and even execute commands on behalf of the user. Once a malicious plugin is installed, what it obtains may not just be file read access, but a trust level equivalent to that of the AI assistant.
Cursor's 11-hour window and the result that "remote login would generally fail" were, to some extent, the combined result of luck and defense mechanisms. But the pre-listing review gap it exposed will not disappear automatically. For developers, what they can do is not wait for marketplace platforms to perfect their review, but make "pre-installation checks" muscle memory—read the list, read the configuration, and use scanning tools as a fallback when necessary.
Names in plugin marketplaces can be forged; commands in repositories cannot. Checks are only meaningful if they happen before execution.
Software supply chain attacks refer to attacks in which the attacker does not directly attack the target system but instead compromises or forges components the target relies on (plugins, libraries, update packages, etc.), delivering malicious code into the target environment through normal distribution channels. The frightening aspect of such attacks is that they bypass perimeter defenses—the user actively installs, the platform distributes normally, yet malicious code enters along with it. The AI editor plugin ecosystem is especially vulnerable: plugins need to read project context, call external APIs, and execute commands on behalf of users, with permission boundaries far broader than traditional tools. In the Cursor incident, the attacker only needed "same name" to complete distribution—a typical example of supply chain trust being exploited. The focus of defense therefore shifts from "whether the platform reviews" to "whether the component's actual behavior is verified before installation."
One-line Summary
A malicious plugin impersonating Claude Code was listed on the Cursor marketplace for 11 hours, exposing AI editor plugin supply chain risks and the need for pre-installation verification.
Paragraph Summary
A malicious extension impersonating Claude Code was listed on Cursor's official marketplace for about 11 hours, planting a remote login key and scripts that persisted after uninstallation. Cursor said the stranger's remote login would generally fail, but the plugin still exfiltrated information such as the computer name. The core of the incident is that same-name camouflage exploited users' default trust in marketplace names. The article further points out that Claude Code plugins can also execute code locally, and that Hooks and MCP servers can run programs autonomously. Before installation, users should review the Will Install list, audit commands in hooks.json and .mcp.json, and cross-check with NVIDIA SkillSpecter; if it is still unclear what the plugin will run, skip it. The AI editor extension ecosystem is replicating traditional software supply chain problems, but with higher permissions and greater risk.
Related articles
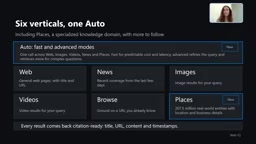
Microsoft WebIQ: Verifiable Real-Time Web Grounding for AI Agents
Microsoft WebIQ gives AI Agents real-time, citable web grounding across web, news, images, videos, and Places—164ms P95 latency, 50% fewer tokens, Scopes source control, and MCP integration.
Augmentable Gaussian Splatting: Building Photorealistic Simulation Environments for Robot Training
Team combines Gaussian Splatting with meshes to build photorealistic robot simulation environments, integrating MuJoCo Warp physics and Franka Panda for augmentable, relightable real-site simulation.
Gemini 4 Carbon Released: The Leap from Gemini 3 to Gemini 4 in Under a Year
Google releases Gemini 4 Carbon, less than a year after Gemini 3. In the official demo, Carbon reverse-engineered the Theme Park binary, added a new DeepMind-themed ride, and ported it to the web in one shot.