FBI Crime Database Reportedly Hit by Hackers; Trump Says 'Not Good'

FBI investigates reports of NCIC hack; Trump gives brief response saying it's 'not good.'
The FBI is investigating reports that the National Crime Information Center (NCIC), a core database for federal, state, and local law enforcement to query criminal records, warrants, and missing persons, was hacked. Such a breach could impact law enforcement integrity and public trust. President Trump responded briefly with 'not good,' without technical details, indicating the incident is still in an information consolidation phase. Attacker identity, intrusion path, and any data exfiltration remain unconfirmed. The article notes centralized law enforcement databases are high-value targets due to rich data, many access points, and complex permissions, highlighting dual challenges of data security and privacy protection.

The U.S. Federal Bureau of Investigation's (FBI) National Crime Information Center (NCIC) is reportedly the subject of an investigation into a hacking incident. The news quickly gained traction after being reported by media outlets, and U.S. President Trump publicly commented that the situation is "not good," without disclosing further details. The incident remains under investigation, and officials have not yet confirmed the specific scope and impact of the attack.
The Core Issue: What NCIC Is and Why It Matters
NCIC is one of the most critical databases in the U.S. law enforcement system, long providing federal, state, and local law enforcement agencies with access to criminal records, wanted persons lists, missing persons information, and more. What makes it unique is that it serves both as infrastructure for inter-agency collaborative investigations and as a repository for large volumes of sensitive personal and case data.
Because of this, once such a system is compromised, the impact does not stop at the level of "data breach"—the integrity of the law enforcement chain, the credibility of case investigations, and even public trust in judicial information systems could all be affected. Reports indicate that the FBI has launched an investigation into the hacking incident, but the identity of the attackers, the intrusion pathway, and whether any actual data exfiltration occurred have not been officially confirmed.
NCIC falls under the FBI's Criminal Justice Information Services Division, operating under the interstate law enforcement information-sharing mechanism established in 1965, with its legal basis traceable to the U.S. Department of Justice's authorization of interstate criminal information exchange. The system's data is not collected from a single source; rather, approximately 18,000 law enforcement agencies across the country enter and update records in real time using a unified format, with query response times typically in the range of seconds. This architecture—"federal platform, local data"—enhances investigative efficiency while blurring the boundaries of data responsibility. If a record is erroneous or a stale warrant is not promptly cleared, an individual could be wrongly detained without any warning. The U.S. Government Accountability Office has repeatedly pointed out that NCIC record accuracy depends on self-auditing by each entering agency, and that there is no mandatory periodic verification mechanism at the federal level. This structural deficiency, compounded by external intrusion risks, constitutes a long-standing governance challenge for the system.
Trump's Response: A Conclusion Without Details
According to media reports, Trump used the brief assessment "not good" when responding to the matter. This manner of statement is noteworthy: on one hand, it confirms that the incident has drawn attention at the highest decision-making level; on the other hand, the presidential level did not provide technical details or describe response measures, reflecting that the incident remains in a phase of information consolidation.
In sensitive incidents involving national security and law enforcement data, officials typically disclose information only after investigations reach preliminary conclusions. The current "under investigation" status means it will be difficult for the outside world to obtain a complete factual account in the short term, and any claims about the scale of the attack should be treated as unverified speculation.
Long-Standing Data Security Problems and New Pressures
The security challenges facing systems like NCIC are not isolated. Centralized law enforcement databases are inherently high-value targets: they contain rich data dimensions, serve numerous access points, and involve complex permission systems—any weak link in protection at a single access node could become a point of entry.
On the other hand, controversies surrounding such databases extend beyond security. Issues such as data accuracy, the boundaries of access permissions, and citizen privacy protection have long been debated. This suspected intrusion incident objectively adds a new real-world footnote to these discussions—the more sensitive the information a system carries, the greater the cost of a single security failure.
Centralized law enforcement database permission systems typically use a tiered authorization model: federal agents, state police, local patrol officers, and even some court and prison personnel can access information at different levels. This broad access is a prerequisite for collaborative investigations, but it also means the attack surface expands linearly with the number of access nodes. Historically, NCIC has repeatedly seen cases of insider abuse of query privileges—for example, law enforcement personnel querying records of celebrities or acquaintances for personal purposes. Such "insider" risks are as serious in consequence as external hacker intrusions but are harder to defend against through technical means. In addition, law enforcement data often involves information about suspects who have not been convicted, and retention periods, correction mechanisms, and cross-agency sharing scope are not uniform across U.S. state regulations. Privacy advocates have long criticized such systems for lacking effective individual appeal and correction channels, leaving data subjects in a passive position when their information is misused or leaked.
What to Watch Going Forward
For readers following this matter, several key information points are worth tracking: the FBI's official investigation conclusions, evidence of whether data was accessed or exported, and whether relevant systems will adjust their security policies as a result. Before officials provide a clear statement, it is advisable to remain cautious about various "inside information" claims.
The incident once again reminds us: the security of critical information infrastructure is not a one-time project but a continuous adversarial process. For law enforcement agencies, how to balance investigative efficiency with data security will be a long-term challenge.
One-line Summary
FBI investigates reports of NCIC hack; Trump responds briefly that the situation is not good.
Paragraph Summary
The U.S. Federal Bureau of Investigation is investigating reports that the National Crime Information Center (NCIC) was hacked. NCIC is the core database through which federal, state, and local law enforcement agencies query criminal records, wanted persons lists, and missing persons information, storing large amounts of sensitive data; a breach could affect the integrity of the law enforcement chain and public trust. President Trump responded briefly with "not good," without disclosing technical details, reflecting that the incident remains in an information consolidation phase. The identity of the attackers, the intrusion pathway, and whether data exfiltration occurred have not been officially confirmed. The article notes that centralized law enforcement databases are inherently high-value targets due to their rich data dimensions, numerous access points, and complex permissions, and that this incident once again highlights the dual challenges of law enforcement data security and privacy protection. Going forward, attention should be paid to the FBI's official conclusions and adjustments to system security policies.
Related articles
US SEC Investigates Nvidia: Possible A…
US SEC Investigates Nvidia: Possible Accounting Issues
The US SEC's investigation into Nvidia focuses on potential accounting issues, not products. The news sparked heated discussion on Hacker News, with the market watching the AI chip giant's financial disclosure quality and regulatory signals.
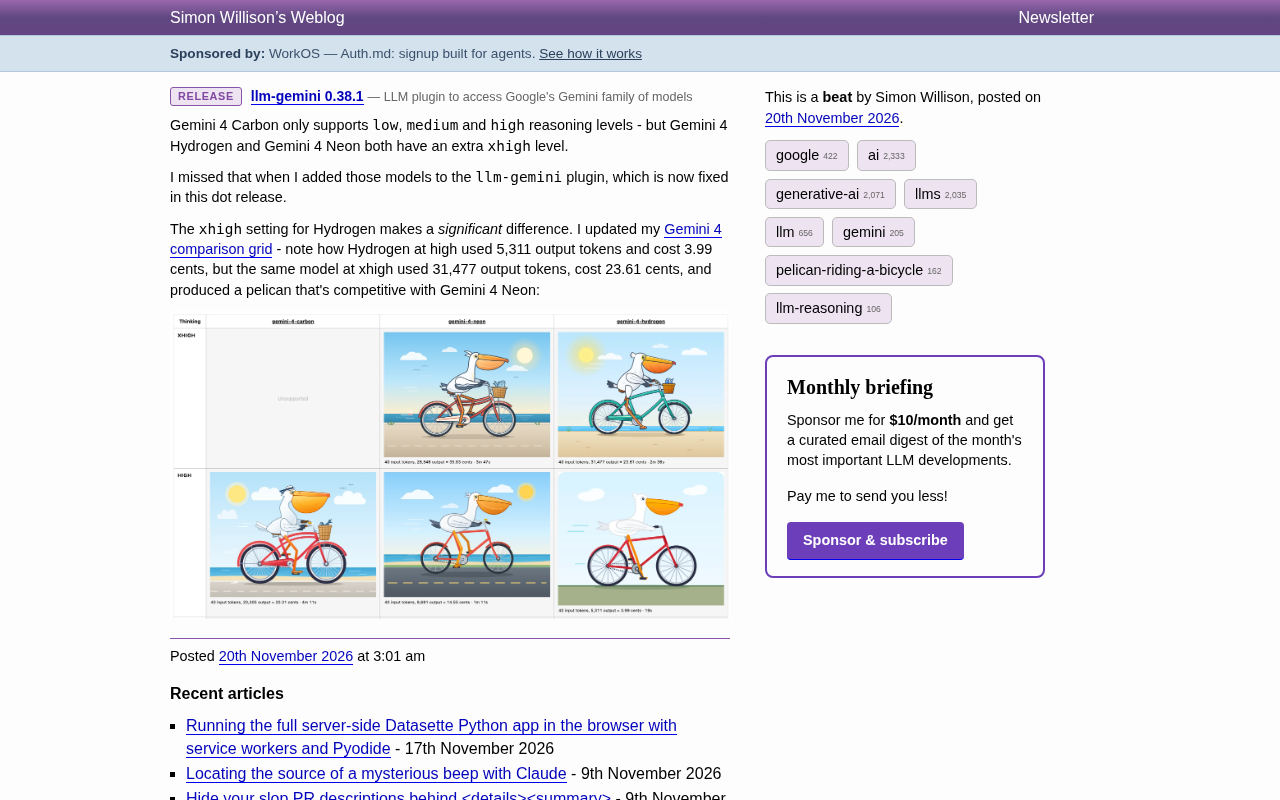
llm-gemini 0.38.1 Fix: Gemini 4 Hydrogen and Neon Gain xhigh Reasoning Level
llm-gemini 0.38.1 fixes the missing xhigh reasoning level for Gemini 4 Hydrogen and Neon. Comparison data shows xhigh sharply raises Hydrogen's output tokens and cost while clearly improving image quality to a level competitive with Neon.
Detonating a Large Pile of Lead Azide: A Dangerous Chemical Experiment
Science blog records an experiment detonating a large pile of lead azide, sparking Hacker News debate. This article analyzes lead azide's dangerous properties, experimental risk boundaries, and the scale of reporting dangerous experiments in science communication.