FBI Warns About AI Hacking Tool Artex: Systems Breached in Three Hours
FBI warns open-source AI hacking tool Artex is being abused; attacks accelerate but fundamentals still work.
The FBI has warned about open-source AI hacking tool Artex, designed for authorized security testing but abused by criminals and state-sponsored groups to attack banks, hospitals, governments, and tech companies. Its core capability is automation: users describe targets in natural language, and the AI agent handles scanning, weakness discovery, and intrusion. In some cases, attackers gained full privileged access in under three hours; one supply chain attack affected over 2,000 Microsoft 365 organizations and multiple South Korean banks, stealing data from about 67,000 people. The developer took the tool offline in October, but copies, forks, and a paid professional edition remain in circulation. The article notes Artex didn't invent new attack techniques—it accelerates existing processes and hunts unmonitored legacy systems. Therefore, fundamentals like timely patching, enabling MFA, and understanding internet exposure remain effective; the key is execution speed must keep up with automated attacks.
Incident Overview: FBI Names AI Attack Tool
The U.S. Federal Bureau of Investigation (FBI) has recently issued a warning about an AI hacking tool called Artex. Originally designed for authorized security testing, this open-source tool has been abused by criminals and state-sponsored hacking groups to launch cyberattacks against banks, hospitals, government agencies, and tech companies.
Unlike traditional attack tools, Artex's core capability lies in automation. Users simply describe the attack target in natural language, and the AI agent takes over the rest of the process—scanning the target, discovering weaknesses, and carrying out the intrusion. The FBI notes that since last August, the tool has appeared in multiple real-world attack incidents.
AI Agent refers to a software system capable of perceiving its environment, making autonomous decisions, and invoking tools to execute multi-step tasks. Unlike traditional scripts or single-function tools, AI agents typically use large language models as their reasoning core, breaking down a user's high-level goal into subtasks and sequentially invoking external programs such as scanners, exploit frameworks, and credential theft tools. Artex is a typical application of this architecture: users describe the target in natural language, and the agent plans its own path and chains tools together, closing the loop from reconnaissance and enumeration to exploitation—steps that previously required human judgment—thereby drastically compressing the time and expertise required by attackers.
Attack Speed and Real Damage
The most alarming feature of Artex is its speed. According to the FBI, in some attack cases, attackers obtained full privileged access in under three hours using the tool.
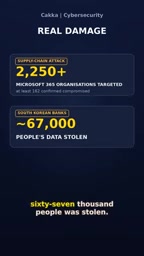
Gaining access is only the beginning; real damage follows. Reports mention a supply chain attack that affected over 2,000 Microsoft 365 organizations and multiple South Korean banks, with data from approximately 67,000 people stolen in the process. These numbers outline a clear attack chain: automated tools shorten intrusion time, the leverage effect of the supply chain amplifies the scope of impact, and ultimately large-scale data breaches occur.
Supply chain attack refers to attackers not directly targeting the final victim, but first compromising a third party the target depends on—software vendors, managed service providers, partner portals, or identity and cloud service platforms—then using that trust relationship to pivot laterally into numerous downstream organizations. Since a single upstream node often serves hundreds or thousands of customers, a single intrusion can produce a "one breach, many victims" leverage effect. The incident affecting over 2,000 Microsoft 365 organizations described in this article exemplifies this amplification mechanism: attackers only need privileged access at a weak link in the supply chain to reach downstream tenants' data with legitimate credentials.
After Takedown: Copies Still Circulating
Following abuse reports, Artex's developer took the tool offline in October. But the move came too late—copies, forked versions, and a paid professional edition are still circulating online.
Once an open-source tool is released, it can hardly be truly recalled. Code can be copied, modified, and redistributed, and the circulation of a paid version further indicates commercial interests are driving it. For defenders, this means they cannot hope to reduce risk by waiting for the tool to disappear.
Artex Didn't Invent New Attacks—It Just Accelerated Old Ones
It is worth noting that Artex itself did not create any new attack techniques. Its role is to accelerate existing attack processes and specifically seek out systems that no one is watching—legacy applications, partner portals, forgotten services.
This assessment has direct implications for defense strategy. If the nature of attacks hasn't changed, then the basic principles of defense don't need to change either. What has truly changed is the speed at which attacks occur and the scale effects brought by automation. Attackers have already automated; defenders must be faster.
Attack surface refers to the sum of all entry points in an organization that can be accessed externally and potentially exploited, including internet-facing applications, open ports, APIs, remote access services, and third-party integrations. The challenge of attack surface isn't quantity but "visibility"—many legacy applications, shadow IT, and partner portals are not included in asset inventories and remain unpatched or unmonitored for extended periods. The value of automated tools lies precisely in traversing these entry points at machine speed, specifically seeking out corners forgotten by defenders. Therefore, the first step in reducing attack surface is asset discovery and continuous inventory, not stacking more detection devices.
Defense Recommendations: Fundamentals Still Work, But Must Be Faster
The FBI's defense recommendations are not new: patch promptly, enable multi-factor authentication, and maintain clear visibility of internet-exposed assets. These measures are consistently emphasized precisely because they are effective.
The problem is execution speed. When attackers can complete the entire process from scanning to intrusion within hours, defenders' security processes operating on quarterly or monthly cycles appear far too slow. Artex hunts systems that are "unwatched," suggesting organizations need to prioritize inventorying legacy applications and external services that have long lacked maintenance. Automated attacks don't require a more complex defensive philosophy to counter—they require making known-effective fundamentals more timely and thorough.
For security teams, the core lesson of this incident may be simple: attackers' automation is advancing, but the breach points remain the forgotten corners. Patching, multi-factor authentication, asset visibility—if these basics are done fast enough, they can still stop attacks driven by automated tools.
Multi-factor authentication (MFA) requires users to provide one or more independent credentials beyond a password (such as one-time codes, hardware tokens, push confirmations, or biometrics) to reduce the risk of credential compromise being directly exploited. Against automated tools, MFA's significance is particularly prominent: even if attackers obtain account passwords through scanning or phishing, logging in is still difficult without the second factor. It should be emphasized that SMS verification codes and simple push confirmations are vulnerable to real-time phishing and fatigue attacks; where conditions permit, phishing-resistant FIDO2/hardware keys should be prioritized and enforced for high-privilege accounts.
One-line Summary
FBI warns open-source AI hacking tool Artex is being abused; attacks accelerate but fundamentals still work.
Paragraph Summary
The FBI has issued a warning about open-source AI hacking tool Artex, originally designed for authorized security testing but abused by criminals and state-sponsored hacking groups to attack banks, hospitals, government agencies, and tech companies. Its core capability is automation: users describe targets in natural language, and the AI agent takes over the entire process from scanning and weakness discovery to intrusion. In some cases, attackers obtained full privileged access in under three hours; one supply chain attack affected over 2,000 Microsoft 365 organizations and multiple South Korean banks, with data from approximately 67,000 people stolen. The developer took the tool offline in October, but copies, forks, and a paid professional edition remain in circulation. The article notes that Artex didn't invent new attack techniques—it merely accelerates existing processes and hunts unmonitored legacy systems. Therefore, fundamentals like prompt patching, enabling MFA, and understanding internet exposure remain effective; the key is that execution speed must keep pace with automated attacks.
Related articles
FBI Warns: Hackers Weaponize AI Agent ARTEX to Attack 200+ Organizations
FBI warns that AI penetration framework ARTEX is being used to attack 200+ organizations, with CrowdStrike tracking the VaporPanda group. We break down ARTEX's agent orchestration architecture, the real attack chain, loss data, and the FBI's five defense recommendations.
FBI Warns: Free AI Hacking Tool Artex Spirals Out of Control, Breaches Cloud Systems in Three Hours
FBI warns that the free open-source AI penetration tool Artex is being abused by criminals and state-backed hackers to breach cloud systems in as little as three hours. This article analyzes real attack cases, overlooked side-door risks, and defense measures enterprises and individuals can take immediately.

Verse Engine: Turn Blender/Unity/Unreal Scenes into Browser 3D Links in One Click
Verse Engine by Ctruh is a browser-native 3D and XR engine that publishes Blender, Unity, and Unreal scenes as browser links in one click. View-based streaming opens a 1.03 billion-triangle city scene on a laptop. It offers embeds, API, and SDK for developers, 3D artists, architecture, and e-commerce teams.