Google Pressures OEMs: GrapheneOS and Bootloader Unlocking Face Tightening Restrictions
GrapheneOS accuses Google of pressuring OEMs to restrict Bootloader unlocking, threatening the survival of third-party ROMs
GrapheneOS officially alleges that Google is pressuring device manufacturers to restrict or even block users from unlocking the Bootloader, thereby undermining the room for survival of third-party Android systems; the news sparked heated discussion on Hacker News with 332 points and 86 comments. The article points out that Bootloader unlocking is a prerequisite for GrapheneOS's security model, which relies on hardware security features of devices such as Pixel and on users' full control of their devices. Google's motives include reducing the attack surface for malicious firmware, protecting payments and DRM content, and maintaining ecosystem consistency, but critics argue this effectively erodes device ownership. Community opinion is clearly divided: one side believes mechanisms such as Play Integrity have already indirectly punished unlocked devices, while the other questions whether the allegation is exaggerated. The core trend is that Android's openness is shrinking from the system layer to the app layer.
Background: An Allegation from GrapheneOS's Official Social Media
According to a post from the official GrapheneOS Mastodon account, Google is pressuring device manufacturers (OEMs) to restrict or even block users from unlocking the Bootloader, thereby undermining the room for survival of privacy- and security-focused third-party Android systems like GrapheneOS. The news quickly sparked discussion on Hacker News, reaching 332 points and 86 comments (source: Hacker News item 50570479).
GrapheneOS is currently one of the Android-derived systems most highly regarded by security researchers, and its core selling point is precisely the hardened protection built on official hardware security modules—all of which presupposes that users can unlock the Bootloader and flash a custom system. If OEMs broadly follow Google's direction and tighten unlocking policies, the hardware adaptation path for GrapheneOS will narrow significantly.
GrapheneOS is a non-profit third-party Android system based on AOSP (Android Open Source Project), known for hardened security and privacy. It does not preinstall Google services, but instead offers an optional sandboxed Play services compatibility layer. Its security hardening includes a hardened memory allocator, a stricter permission model, and deep utilization of the Titan M security chip on Pixel devices.
It is worth noting that GrapheneOS is mainly adapted for Google's own Pixel series, precisely because Pixel provides custom key support for re-locking the Bootloader—after flashing GrapheneOS, users can re-lock with their own keys and restore the full Verified Boot chain. If OEMs broadly prohibit unlocking, this kind of security model that relies on a hardware root of trust will have no way to be implemented.
Why Bootloader Unlocking Is So Critical
The openness of the Android ecosystem is to a large extent reflected in Bootloader unlocking. After unlocking, users can flash third-party ROMs such as GrapheneOS and LineageOS, and can continue to receive security patches after the system stops receiving updates. For privacy-sensitive users, security researchers, and those reusing old devices, this is an irreplaceable capability.
GrapheneOS's entire security model is built on "the user fully controlling the device": it relies on hardware-level security features of devices such as Pixel (such as the Titan M security chip and hardened Verified Boot), but requires users to first remove the manufacturer lock. In other words, Bootloader unlocking is not an option for GrapheneOS—it is the prerequisite for its existence.
Bootloader is the first piece of code that runs after a device is powered on, responsible for verifying and loading the operating system kernel. Manufacturers usually lock it so that the device can only boot system images signed by the official authority, which is the starting point of the Verified Boot chain. Unlocking the Bootloader means disabling or bypassing this mandatory verification, thereby allowing system images with any signature to be flashed.
It is important to distinguish that unlocking the Bootloader and obtaining root privileges are not the same thing: the former is boot control at the system level, while the latter is the highest privilege within the operating system. Unlocking usually requires tools such as fastboot and wipes device data, and some manufacturers also require waiting a period of time or submitting an application. After unlocking, the device's Verified Boot state changes to an "orange" or "yellow" warning state, which is precisely the basis used by later authentication mechanisms such as Play Integrity to determine device integrity.
Google's Motives and the OEMs' Dilemma
From Google's perspective, tightening Bootloader unlocking has a clear commercial and security narrative: reducing the surface exposed to malicious firmware attacks, protecting payments and DRM content, and maintaining the consistency of the Android ecosystem. But critics point out that the side effect of this logic is to transfer "device ownership" from users to manufacturers.
OEMs, meanwhile, are in a dilemma. On the one hand, they depend on Google's GMS licensing and Android compatibility commitments; on the other hand, unlocking policy is an important consideration for geek users when purchasing devices, and being too strict will damage brand reputation. Many comments in the Hacker News discussion argue that the real pressure point lies in Google's control over authentication mechanisms such as Play Integrity—even if the Bootloader can still be unlocked, unlocked devices will be restricted in applications such as banking and payments.
Play Integrity API is a device and app integrity verification service provided by Google, succeeding the earlier SafetyNet Attestation. Apps (especially banking, payment, DRM, and games) can call this interface to obtain signals such as whether the device has passed Google certification, whether the system has been tampered with, and whether the Bootloader is unlocked, and decide whether to provide services based on these signals.
Its determination relies on hardware-backed key attestation: devices have keys pre-provisioned in the TEE (Trusted Execution Environment) at the factory, and only devices running an officially certified system can generate compliant and unrevoked attestation. This means that even if a user successfully unlocks and flashes a third-party ROM, the app layer can still identify and restrict the device through this mechanism. This is precisely the core of the community's concern—the right to unlock and the usable experience are decoupled, and restrictions shift from the system layer to the app layer.
Community Reaction and Potential Impact
The discussion on Hacker News shows clear divisions. Some comments argue that GrapheneOS's allegation is reasonable, and that in recent years Google has indeed indirectly punished unlocked devices through mechanisms such as the Play Integrity API and SafetyNet; other comments question whether GrapheneOS's statement exaggerates the degree of "pressure," arguing that OEM unlocking policies have always been decided by each manufacturer itself.
Regardless of the specific form of pressure, this controversy reveals a deeper problem: Android's "openness" is shrinking from the system level to the app layer. When unlocking the Bootloader no longer brings a fully usable device experience, the room for survival of third-party ROMs will be systematically compressed. For users who value device autonomy, this may be a trend more worth watching out for than a failed flash.
What It Means for Ordinary Users
In the short term, devices that have already been unlocked will not be immediately affected, but when buying new phones in the future, the availability of Bootloader unlocking may become an increasingly scarce attribute. For users who rely on GrapheneOS, the community consensus is to prioritize models that still explicitly support unlocking and to watch for changes in Play Integrity certification policies.
This contest over the right to unlock is essentially a tension between two values: "security" and "autonomy." Every step of tightening by Google and OEMs will trigger backlash in the community, and the final outcome will likely depend on whether regulators regard Bootloader unlocking as part of consumer rights.
Related articles
US SEC Investigates Nvidia: Possible A…
US SEC Investigates Nvidia: Possible Accounting Issues
The US SEC's investigation into Nvidia focuses on potential accounting issues, not products. The news sparked heated discussion on Hacker News, with the market watching the AI chip giant's financial disclosure quality and regulatory signals.

FBI Crime Database Reportedly Hit by Hackers; Trump Says 'Not Good'
FBI's NCIC reportedly hit by hackers; FBI has launched an investigation and Trump said it's 'not good.' This article covers the incident, NCIC's importance, and law enforcement data security challenges.
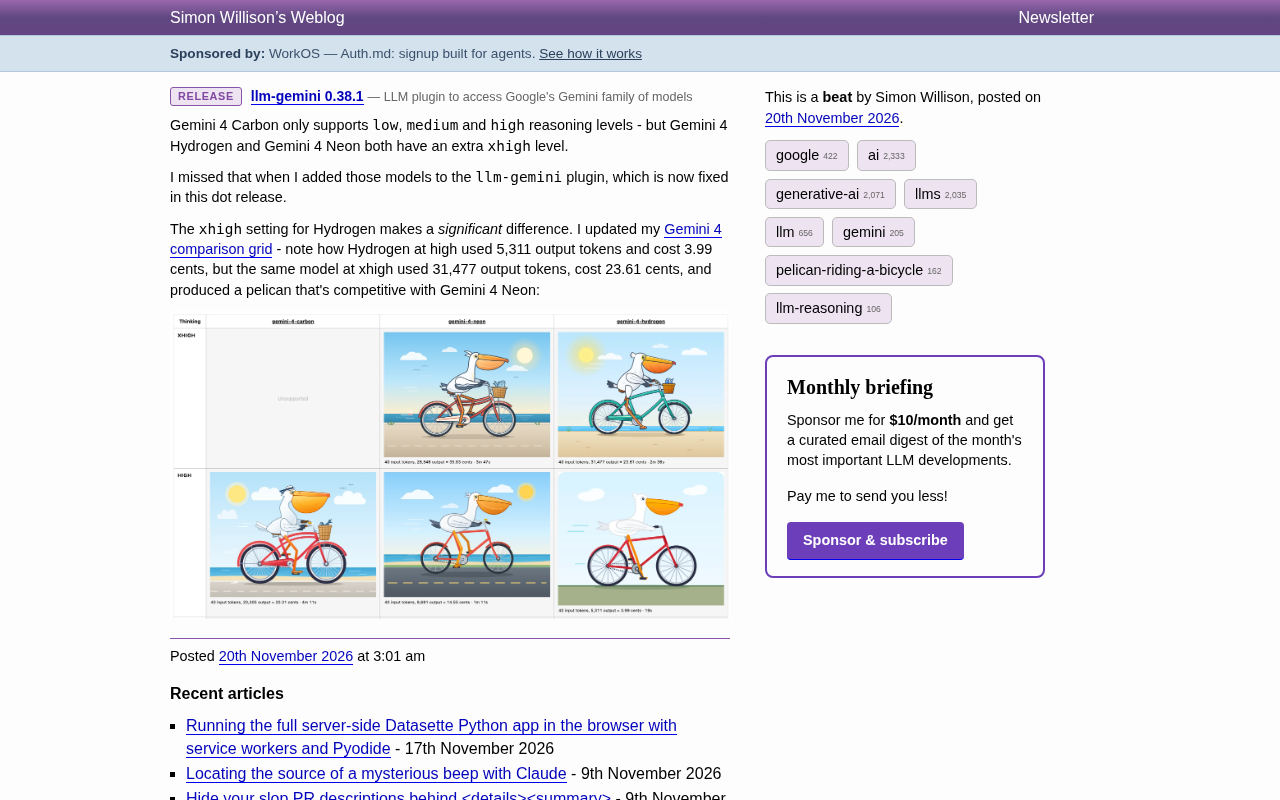
llm-gemini 0.38.1 Fix: Gemini 4 Hydrogen and Neon Gain xhigh Reasoning Level
llm-gemini 0.38.1 fixes the missing xhigh reasoning level for Gemini 4 Hydrogen and Neon. Comparison data shows xhigh sharply raises Hydrogen's output tokens and cost while clearly improving image quality to a level competitive with Neon.