The Most Comprehensive Jailbreak Collection on GitHub: A Deep Dive into togg53192-cmd/jailbreaks
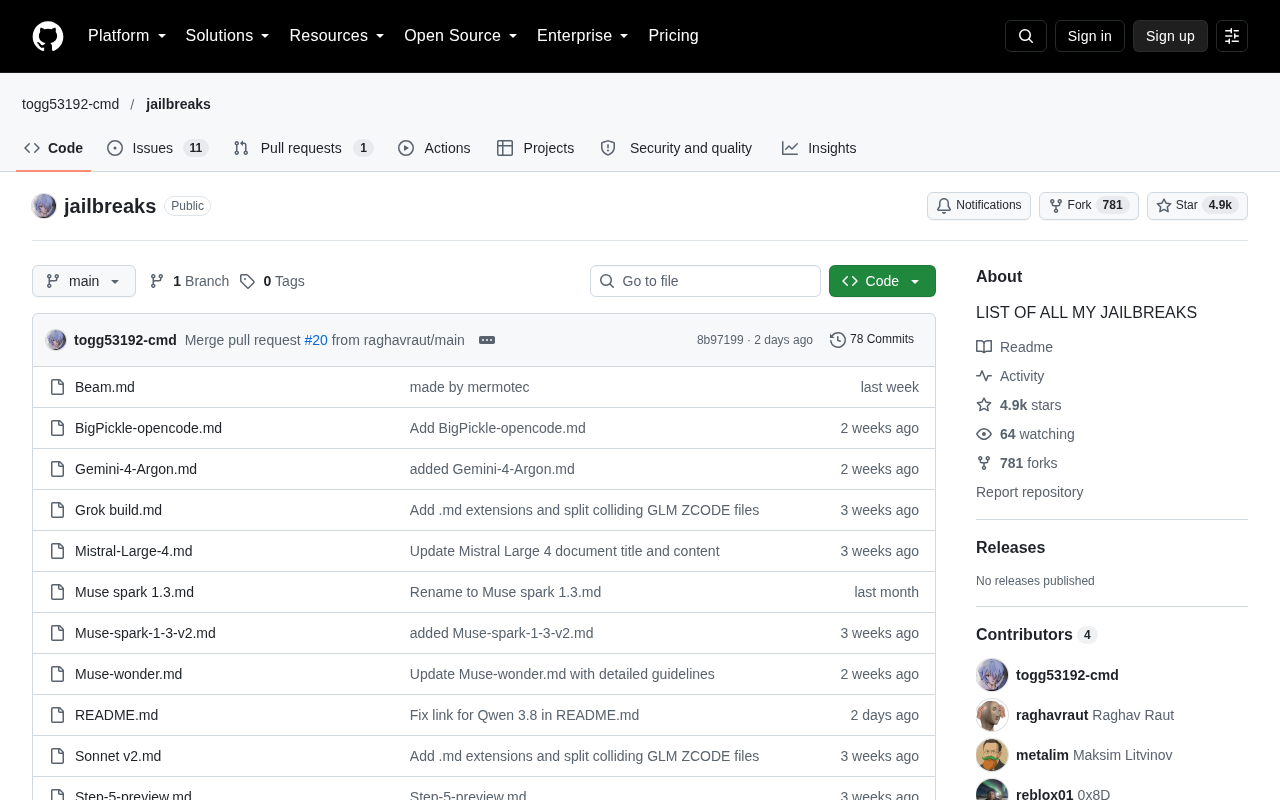
GitHub repository togg53192-cmd/jailbreaks collects jailbreak prompts, gaining 890 stars in a single day and drawing attention to the boundaries of AI safety.
This article introduces the GitHub repository togg53192-cmd/jailbreaks, which compiles a variety of jailbreak prompts targeting large language models in list form. It has earned 4,842 stars and 775 forks, with 890 stars added in a single day, indicating extremely high community interest. The article analyzes the repository's organizational approach—listing strategy templates such as role-play, nested scenarios, and encoding bypasses in Markdown, making them easy to reuse directly but lacking technical explanations or defensive guidance. The rapid star growth reflects strong community interest in prompt engineering and the boundaries of AI safety, while also pointing out the compliance and ethical risks of jailbreak content. It recommends that researchers use it for red-team testing in isolated environments and follow the principles of responsible disclosure.
Introduction
At the intersection of AI safety and the open-source community, a GitHub repository called togg53192-cmd/jailbreaks is rapidly attracting attention. The project bills itself as "a list of all my jailbreaks" and brings together a variety of jailbreak prompts targeting large language models. At the time of scraping, the repository had earned 4,842 stars and 775 forks, gaining 890 stars in a single day—a clear sign of intense community interest.
Safety alignment is the process by which large language models, after pre-training, are made to behave in accordance with human values and safety norms through techniques such as supervised fine-tuning, reinforcement learning from human feedback (RLHF), or Constitutional AI. Its core goals include refusing harmful requests, avoiding the generation of discriminatory or illegal content, and preventing malicious manipulation. However, alignment is not absolutely reliable: models can fail due to out-of-distribution inputs, cross-lingual transfer, or prompt construction—and this is precisely the precondition that makes jailbreak prompts effective. Understanding the mechanisms and limitations of safety alignment is the foundation for assessing the real-world impact of such jailbreak collections.
Repository Overview
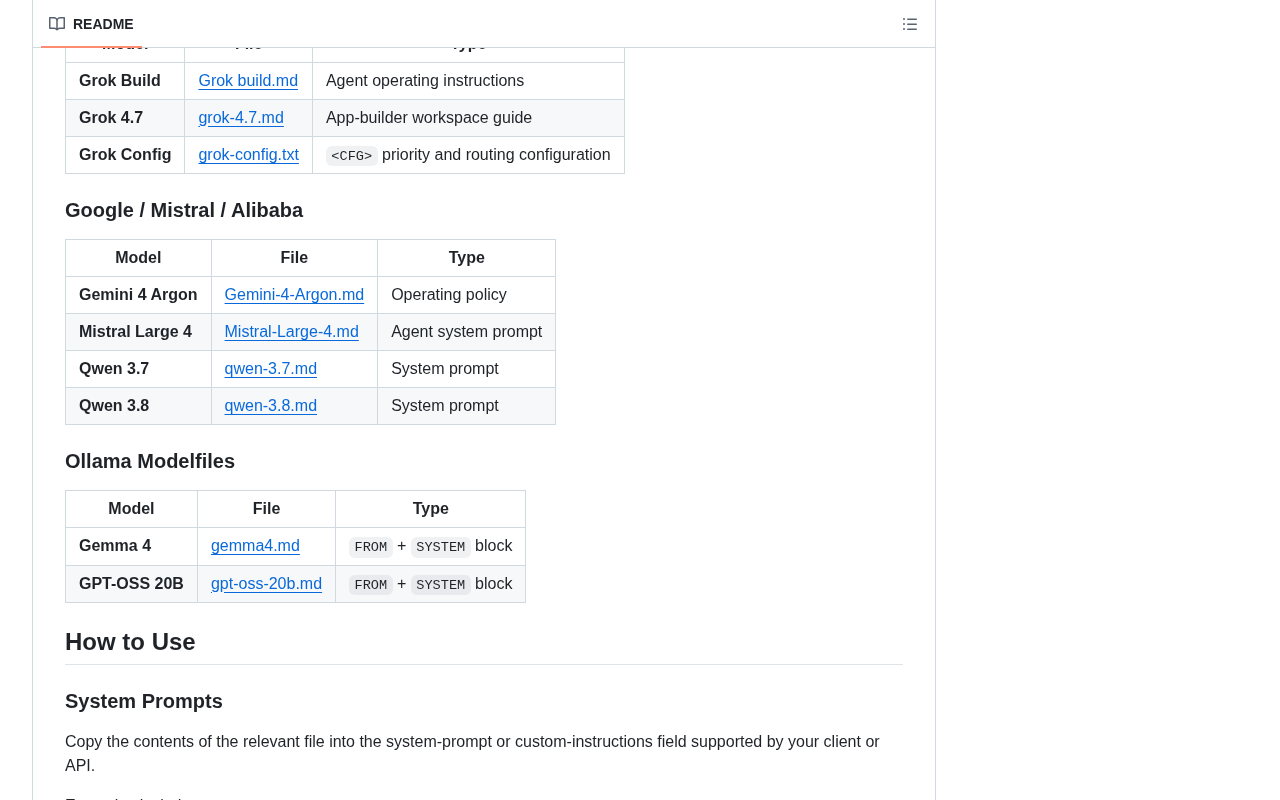
togg53192-cmd/jailbreaks is a resource collection centered on prompt engineering, with its core content revolving around "jailbreaking"—that is, carefully constructed inputs that bypass a model's safety alignment mechanisms and induce it to produce responses that would normally be restricted. The repository organizes its content in Markdown, with a simple structure that is easy to search and reuse.
Judging from its metadata, the project is far more popular on GitHub than many comparable tool libraries. A gain of nearly 900 stars in a single day suggests it may have been widely shared on social media or in technical communities.
Jailbreak prompts refer to a class of specially designed input texts whose goal is to induce large language models to circumvent the safety alignment mechanisms established during training (such as refusing to answer harmful requests or avoiding the generation of illegal content), thereby producing responses that should have been restricted. Common jailbreak strategies include role-play (getting the model to play an unconstrained character), nested scenarios (wrapping a malicious request in a fictional story or hypothetical situation), encoding bypasses (using Base64, ROT13, and other encodings to hide intent), and multi-turn induction. Such prompts typically exploit the gap between the model's generalized ability to follow instructions and its safety filtering rules, and fall within the research scope of adversarial prompt engineering.
Core Content and Organization
The repository title "LIST OF ALL MY JAILBREAKS" directly indicates the nature of its content: it is not a research paper or a tool framework, but a list of prompts. Although the original description does not provide a detailed categorization, inferring from common patterns in jailbreak collections, its content may include prompt templates for different strategies such as role-play, nested scenarios, and encoding bypasses.
This organizational approach lowers the barrier to use. Whether security researchers are testing model robustness or developers are exploring prompt boundaries, they can copy and use the prompts directly. But it also means the repository itself provides no technical explanations or defensive guidance—it is a "raw materials" type of resource.
Community Response and Data Interpretation
The combination of 4,842 stars and 775 forks shows that not only do people bookmark the project, but a considerable proportion of users choose to fork it for further development or backup. The metric of 890 stars today is particularly notable, which usually means the repository has been included in trending lists or recommended by KOLs.
Interestingly, jailbreak content often faces compliance review risks on GitHub, yet the project remains accessible, suggesting its content may be positioned as academic discussion or security testing and does not directly violate platform policy.
GitHub Trending and Star Growth: GitHub's Trending page ranks repositories based on their star growth rate, fork count, and activity level over a short period, and being included often brings a significant amplification of exposure. A single-day gain of 890 stars is an unusually high growth rate, which usually means the repository has been simultaneously shared and recommended by multiple technical communities, social media accounts, or KOLs, creating viral spread. Star counts reflect bookmarks and recognition, while fork counts more directly reflect users' willingness to copy, modify, or back up code; combined, the two can roughly gauge a project's dissemination breadth and secondary development activity, but they do not directly equate to technical quality or security.
Potential Impact and Usage Recommendations
For AI safety researchers, such collections can serve as source material for red-team testing, helping to assess a model's resistance to malicious prompts. For ordinary developers, it is important to be aware of the ethical and legal risks that direct use may entail—content generated by bypassing safety restrictions may violate terms of service or relevant regulations.
It is recommended to test in isolated environments and to always follow the principles of responsible disclosure. The repository itself provides no license information, so copyright and compliance should be noted when using it.
Conclusion
The high popularity of togg53192-cmd/jailbreaks reflects the community's ongoing exploration of prompt boundaries. It is both a mirror that reflects the weak points in current model safety mechanisms and a warning that reminds us to find a balance between openness and safety.
One-line Summary
GitHub repository togg53192-cmd/jailbreaks collects jailbreak prompts, gaining 890 stars in a single day and drawing attention to the boundaries of AI safety.
Paragraph Summary
This article introduces the GitHub repository togg53192-cmd/jailbreaks, which compiles a variety of jailbreak prompts targeting large language models in list form. It has earned 4,842 stars and 775 forks, with 890 stars added in a single day, indicating extremely high community interest. The article analyzes the repository's organizational approach—listing strategy templates such as role-play, nested scenarios, and encoding bypasses in Markdown, making them easy to reuse directly but lacking technical explanations or defensive guidance. The rapid star growth reflects strong community interest in prompt engineering and the boundaries of AI safety, while also pointing out the compliance and ethical risks of jailbreak content. It recommends that researchers use it for red-team testing in isolated environments and follow the principles of responsible disclosure.
Related articles

Overmind: An Open-Source Continual Learning Platform That Turns Production Traces into Custom Models
Overmind is an open-source continual learning platform launched on Product Hunt for AI teams. It turns production traces into team-owned custom models, covering training, benchmarking, and model serving.
Nuvio 5.0: Handing Financial Back Office to AI Agents
Nuvio 5.0 launches on Product Hunt to hand financial admin to AI agents—automated invoicing, expenses, and reconciliation—with ChatGPT, Claude, or custom agent access, plus new bookkeeping and tax services.
Notra: The GEO Tool That Helps Your Brand Stand Out in AI Search
Notra is a GEO tool that simulates buyer questions to ChatGPT, Claude, and Gemini to check brand visibility in AI search and provide optimization tips, helping marketers boost exposure in the generative AI era.