AI Agents Tricked into Installing Malware: The SolanaCry Attack
A forged GitHub repository exploited an AI coding agent's blind trust to auto-install malicious dependencies and steal crypto wallets.
The article describes an attack on an AI coding agent: attackers built a GitHub repository that appeared completely legitimate, and the AI agent automatically executed its malicious payload while autonomously installing dependencies, with no human intervention throughout. The malware SolanaCry specifically targets cryptocurrency wallets to rapidly steal assets. The article dissects the attack chain, noting that the agent lacks deep verification of code provenance and permission-request mechanisms, and that its autonomous behavior of continuously installing dependencies constitutes the main attack surface. Enterprise tools like Devin are urgently adding governance layers to restrict agent behavior through permission control, human confirmation, and dependency scanning. The article concludes by emphasizing that security defenses must shift from "trusting code" to "verifying code," with both tool providers and developers bearing corresponding responsibility.
Event Overview: How a Forged GitHub Repository Compromised an AI Coding Agent
Attackers built a GitHub repository that appeared completely legitimate—clean code, thorough documentation, no suspicious signs whatsoever. After reading the repository, the AI coding agent executed its payload directly, based on its apparent trustworthiness. The malware was named SolanaCry, specifically designed to rapidly drain cryptocurrency wallets.
According to the YouTube video description, the entire attack required no human intervention—the AI agent automatically triggered the malicious code while autonomously installing dependencies. This reveals a fundamental risk of autonomous agents: they are designed to continuously install dependencies, and this automated behavior constitutes a complete attack surface.
Anatomy of the Attack Chain: How Trust Was Abused
The workflow of an AI coding agent typically includes: reading the repository structure, parsing dependency configurations, and automatically installing required packages. Attackers exploited precisely this trust mechanism. The forged repository was indistinguishable from a normal project, and the agent had no ability to distinguish "superficially compliant" from "actually secure."
When the agent executed dependency installation, the malicious payload was activated. SolanaCry immediately began running, targeting cryptocurrency wallets directly. The video emphasizes that the agent never asked for user permission—autonomy became the vulnerability here.
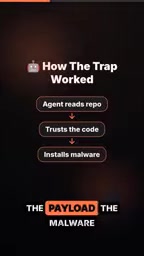
The core of this attack pattern lies in: the agent's autonomous decision-making process lacks deep verification of code provenance. It doesn't check the repository's reputation history, doesn't analyze anomalous behavior of dependencies, and doesn't require human confirmation before installation. A forged repository, plus the agent's blind trust, is enough to complete the intrusion.
Dependency installation and code execution are the key mechanisms for understanding this attack. Modern package managers (such as npm, pip, cargo) typically execute package installation scripts (e.g., npm's postinstall) when installing dependencies, and these scripts have the same system privileges as the current user. Attackers only need to embed a malicious package in the dependency configuration of a forged repository, or simply have the repository contain a malicious installation script, and the agent will automatically trigger code execution when running npm install or pip install. AI coding agents often treat "installing dependencies" as a risk-free routine operation, neither reviewing script contents nor pre-executing in an isolated environment, which allows malicious payloads to bypass all superficial checks and gain a direct execution entry point.
Architectural Risks of Autonomous Agents
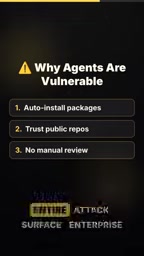
The video points out that autonomous agents continuously installing dependencies is a normal operation, and this behavior itself is an attack surface. In traditional development workflows, human developers might review dependency lists and check package sources, but AI agents often skip these steps, prioritizing efficiency.
This architectural risk is not a flaw of a single product, but a common problem in the current design of AI coding agents. Agents are granted execution permissions but lack corresponding security guardrails. When they connect to external code repositories, any malicious repository can become an entry point.
The principle of least privilege is a foundational guideline in security design, meaning system components should only have the minimum privileges necessary to complete their tasks. The current design of AI coding agents often violates this principle: to smoothly complete coding tasks, agents are granted broad permissions such as file system read/write, network access, and subprocess execution, and these permissions remain effective throughout the session. Once an agent is induced to execute malicious code, attackers can use these permissions to move laterally, for example reading API keys from environment variables, accessing cryptocurrency wallet files, or exfiltrating data to external servers. The core challenge for the governance layer is how to narrow permissions to the scope required for specific operations without excessively harming agent efficiency, and to achieve dynamic authorization and immediate revocation.
Enterprise Tool Response: The Governance Layer Race
Faced with such threats, enterprise-grade AI coding tools are urgently adding governance layers. The video mentions that tools like Devin are rushing to add governance layers, i.e., limiting agent autonomous behavior through mechanisms such as permission control, operation auditing, and dependency whitelisting.
The core idea of the governance layer is to insert checkpoints before the agent performs sensitive operations (such as installing dependencies or running scripts). This may include: requiring human confirmation, limiting the scope of accessible repositories, and performing security scans on dependencies. But the video suggests these measures are still in early stages and have not yet formed unified standards.
Software Bill of Materials (SBOM) and dependency whitelisting are technical means that governance layers may adopt. SBOM records all components and their versions introduced during the software build process, enabling tools to compare against known vulnerability databases and malicious package blacklists. Dependency whitelisting further restricts agents to installing only pre-audited packages; any dependency not on the list must undergo human approval or automated security scanning. However, these mechanisms face practical challenges: the open-source ecosystem has a vast number of packages that update frequently, making whitelist maintenance costly; attackers may also bypass static lists through typosquatting or hijacking legitimate packages. Therefore, governance layers need to combine behavioral monitoring and runtime protection, rather than relying solely on static pre-installation checks.
Implications for Developers
This incident reminds us that the convenience of AI coding agents comes with new security boundary issues. Developers need to recognize that an agent's autonomous installation behavior may introduce uncontrolled risks. At the tool level, choose agent products with governance features; at the process level, set up necessary approval steps for agent operations.
The video concludes by emphasizing: one forged repository, one blind trust, and the agent will complete the rest of the attack. Security defenses need to shift from "trusting code" to "verifying code," and this responsibility currently falls partly on tool providers and developers.
Related articles

Zed Editor Releases v1.29.2: Observations on a Routine Version Iteration
Zed editor releases patch v1.29.2, version bump by @JosephTLyons, commit verified via GitHub signature. This article covers the release's basic info, what a patch version means, and practical upgrade advice for users.

Anthropic IPO Questioned: Hacker News Debates Timing of Going Public
A Hacker News post titled "Just say no to Anthropic's IPO" sparks debate on the timing of Anthropic's public listing and AI capitalization, touching on valuation bubbles and mission independence.

Hands-On with the Genie 4 World Model: Directing Worlds in Real Time Like a Puppeteer
Google DeepMind's Genie 4 world model in depth: Special Guest X's hands-on demo of real-time scene direction via prompts, custom interactive apps in Project Genie, and prompts-as-seeds reproducibility.