AI Security Updates: OpenAI Partnership, Agent Auditing, and ONLYOFFICE 10.0
AI capability expansion and security defense advance in parallel across enterprise, open-source, and national fronts.
This article covers four recent AI industry developments highlighting two parallel trends: capability expansion and security protection. On the capability side, Birlasoft became an OpenAI Select Partner to build enterprise AI solutions, while ONLYOFFICE 10.0 embedded context-aware AI across all editor components. On the security side, Tenable began using OpenAI's cybersecurity model to scan open-source AI agents for prompt injection risks before deployment, and South Korea's KISA launched its second AI security competition. The core conclusion: as generative AI accelerates into production environments, integrating security reviews into deployment workflows has shifted from optional to essential.
AI technology is rapidly infiltrating enterprise software, cybersecurity, and office collaboration. A cluster of recent industry developments — from Birlasoft's strategic partnership with OpenAI, to Tenable's AI-powered agent security review, to the intelligent upgrades in ONLYOFFICE 10.0, and South Korea's KISA AI security competition — collectively outline two defining themes in today's AI adoption: capability expansion and security protection.
Birlasoft Becomes an OpenAI Select Partner
IT services firm Birlasoft has officially become an OpenAI Select Partner, earning the credentials to build and sell AI solutions based on OpenAI models. This partnership enables Birlasoft to integrate OpenAI's foundational model capabilities into its enterprise-facing service portfolio.
For traditional IT service providers, establishing a formal relationship with a top-tier large model vendor is a critical move for competing in the enterprise market during the generative AI wave. These partnerships typically span technical integration, joint solution development, and channel sales — helping enterprise clients access cutting-edge AI capabilities at lower cost and without bearing the burden of developing underlying models in-house.
OpenAI's partner ecosystem is tiered, with Select Partner typically sitting in the middle tier — above standard certified partners but below top-level strategic partners. Companies earning this designation must meet certain technical competency and business scale requirements, and receive specific commercial licensing and technical support for API and model usage. For mid-sized IT service firms like Birlasoft — which focuses on vertical industries such as manufacturing, healthcare, and financial services — official partner status serves both as a trust signal to enterprise clients and as an opportunity to gain early access to new models and joint marketing programs. This creates a differentiated competitive edge in the increasingly crowded AI integration services market.
Tenable Uses AI Models to Audit Open-Source AI Agents
Cybersecurity vendor Tenable announced it is now using OpenAI's cybersecurity model to audit open-source AI agents, scanning for potential prompt injection risks before deployment.
Prompt injection is one of the most prominent security threats facing AI agents today. Attackers craft malicious inputs to manipulate AI systems into performing unintended actions — such as leaking sensitive data or bypassing established restrictions. As more open-source AI agents are introduced into production environments, these risks are moving from theoretical to real-world.
Tenable's approach is notably emblematic: using AI to defend against AI. By leveraging large models' comprehension capabilities to automatically identify anomalies and vulnerabilities in agent behavior, this method can cover more complex and covert attack patterns compared to traditional rule-based scanning. It reflects a broader trend: AI security is becoming an indispensable prerequisite in the AI deployment pipeline.
Prompt injection attacks fall into two categories: direct and indirect. Direct injection involves an attacker embedding malicious instructions within user input to override the system's preset behavior rules. Indirect injection is more subtle — malicious content is hidden in external data sources that an AI agent reads (such as web pages, documents, or databases), and the embedded instructions trigger when the agent retrieves and processes that content. For AI agents with tool-calling, file access, or internet connectivity capabilities, indirect injection can lead to data exfiltration, privilege abuse, or lateral movement — far more dangerous than traditional input validation vulnerabilities. This is precisely why keyword filtering or rule engines alone are insufficient: attack payloads often masquerade as legitimate instructions at the semantic level, requiring a language-understanding model to effectively detect them.
ONLYOFFICE 10.0: Context-Aware AI Across All Editors
Open-source office suite ONLYOFFICE has released version 10.0, adding context-aware AI capabilities to every editor component while patching 35 security vulnerabilities.
Context-aware AI means the intelligent assistant can understand the content and context of the current document, providing more relevant assistance — whether writing a document, working with spreadsheets, or building a presentation. Embedding AI capabilities natively into every editor, rather than offering them as standalone plugins, reflects a product philosophy of deep AI integration in office software.
Also notable is that this update simultaneously patches 35 vulnerabilities. Office software handles vast amounts of sensitive documents and is a high-value target for attackers. Strengthening the security foundation while introducing new AI features represents the dual imperative that open-source projects must address as they move toward enterprise-grade adoption.
South Korea's KISA Launches Second AI Security Competition
South Korea's Korea Internet & Security Agency (KISA) has opened registration for its second AI cybersecurity competition, with applications closing on October 26.
A national-level agency organizing an AI security competition sends a clear signal: governments are increasingly prioritizing the development of AI system security capabilities. These competitions not only identify and cultivate security talent, but also expose real vulnerabilities in AI systems through hands-on exercises, providing valuable reference points for industry and regulators alike.
From Tenable's agent auditing to KISA's security competition, it's clear that AI security has formed a complete chain — from enterprise practice to national strategy.
Industry Observation: Capability and Security in Parallel
These seemingly disparate developments all point toward a single core proposition: the rapid expansion of AI capabilities must be accompanied by an equivalent investment in security.
Birlasoft's partnership with OpenAI and ONLYOFFICE's AI upgrade represent the capability side of the equation; Tenable's prompt injection scanning, KISA's security competition, and the vulnerabilities patched alongside ONLYOFFICE's new features collectively represent the defensive response. For enterprises and developers, proactively incorporating security reviews into deployment workflows — while embracing the efficiency gains of generative AI — is no longer optional. It's a requirement.
Related articles
Anthropic IPO Countdown: The Compute Cost Ledger Behind a $2 Trillion Valuation
Anthropic's IPO targets up to $2 trillion — double its Series H valuation. We break down the timeline, compute cost logic, and the key question investor day must answer.
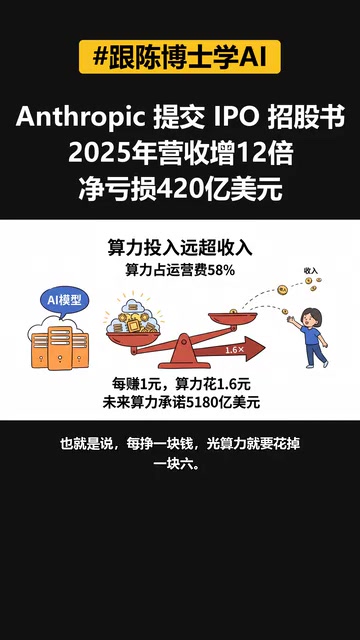
Anthropic IPO Prospectus Revealed: Behind 12x Revenue Growth, the Twin Tests of Compute Costs and Customer Concentration
Anthropic filed its IPO prospectus: 2025 revenue up 12x to $4.6B, net loss $42B including $34B non-cash. Breaking down compute costs, $2T valuation logic, customer concentration risks, and founder control.
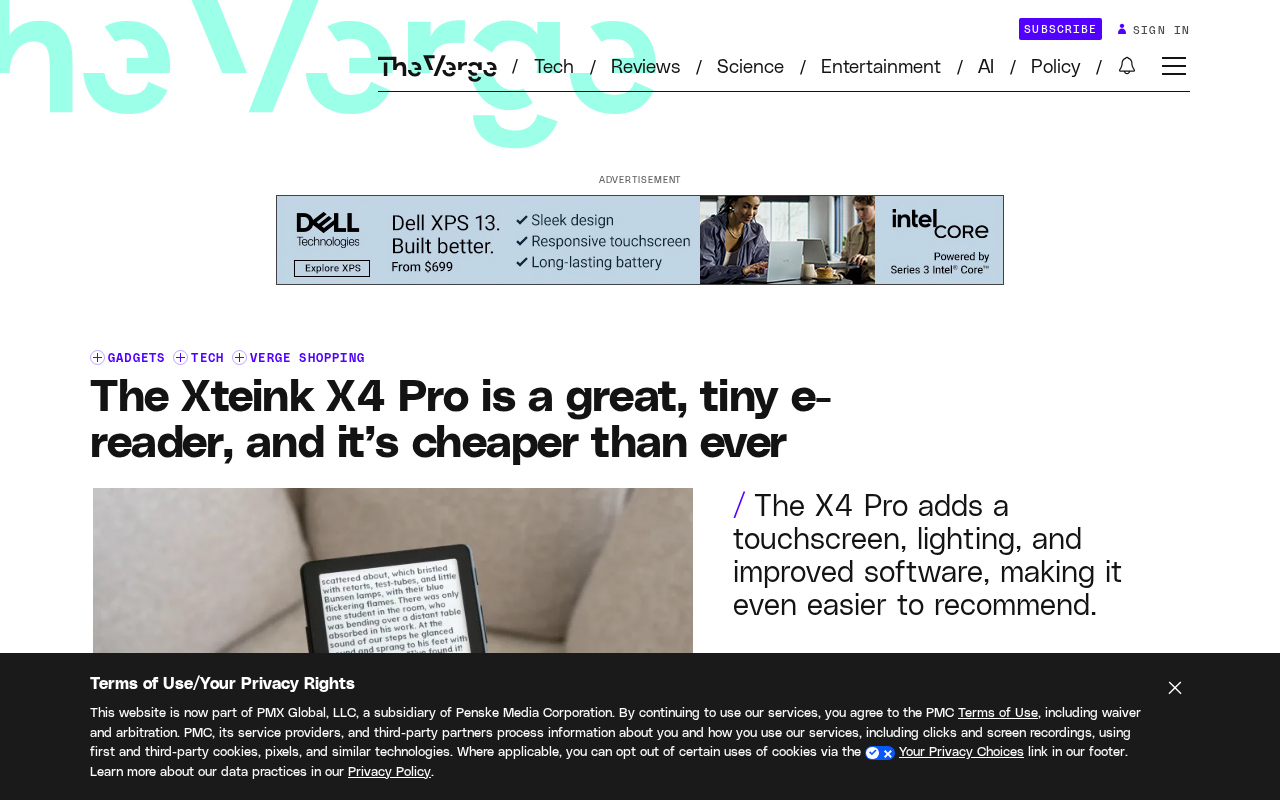
Xteink X4 Pro Review: A Mini E-Reader That Fits in Your Pocket, Now More Affordable
Xteink X4 Pro is a 4.26-inch mini e-reader, smaller and thinner than a 6-inch Kindle, magnetically attachable to phones, and cheaper than ever. We analyze its screen, design, use cases, and value.