Humble Bundle Redesign Removes Two-Factor Authentication Settings, Raising Security Concerns
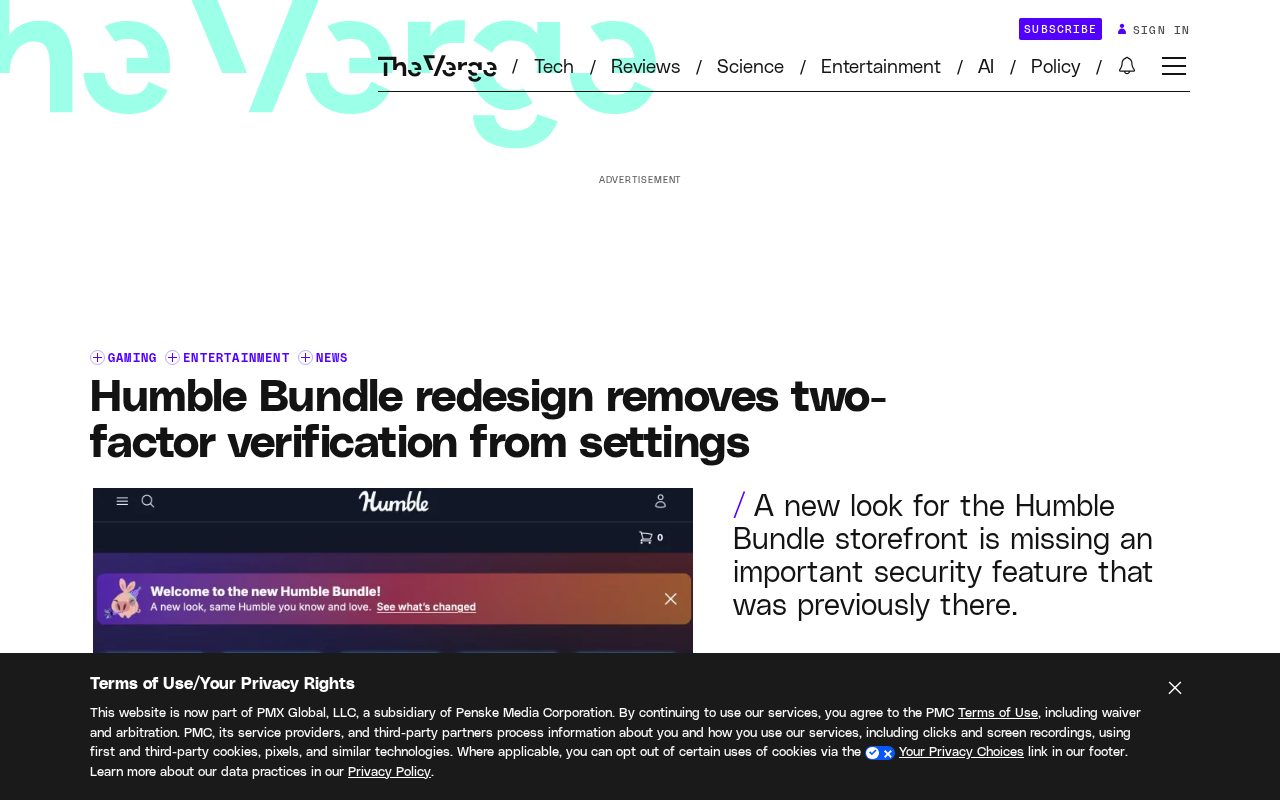
Humble Bundle's redesign removes the 2FA settings entry, raising user concerns about account security.
After the Humble Bundle store's interface redesign, users found that the settings page no longer offers the option to add or update two-factor authentication (2FA), raising widespread concerns about account security. 2FA is a key measure for protecting linked payment information and game libraries; the entry's disappearance means users cannot enable, update, or revoke verification methods themselves. Community users worry this may force them to choose less secure passwords or abandon the platform. Humble Bundle has not yet publicly explained the change, possibly due to a redesign oversight or an ongoing security process redesign. The incident reminds digital stores that accessibility of security features is crucial for maintaining user trust, and platforms should ensure security settings are not sacrificed during redesigns and communicate changes promptly.
Event Overview
The Humble Bundle store recently underwent an interface redesign, but users have discovered that the settings page no longer offers the option to add or update two-factor authentication (2FA). According to Kotaku, this change has raised concerns about account security. PC Gamer further notes that Humble Bundle's support page still contains discussions about two-factor authentication, but the disappearance of the settings entry makes it difficult for users to manage this security feature.
The Importance of Two-Factor Authentication
Two-factor authentication is a critical measure for protecting the security of online accounts, especially on gaming platforms and digital stores where user accounts are often linked to payment information and game libraries. The removal of the settings entry does not mean that the 2FA functionality is completely disabled, but users cannot enable or update their verification methods on their own, which may reduce account security.
Two-factor authentication (2FA) typically combines two types of credentials: something the user knows (a password) and something the user has (a device or one-time code, such as a dynamic code generated by a TOTP app, an SMS verification code, or a hardware security key). Even if a password is stolen in a data breach, an attacker lacking the second factor will struggle to log in. For digital stores, 2FA can also reduce the success rate of credential stuffing attacks—where attackers use account credentials leaked from other platforms to attempt bulk logins. It is worth noting that the strength of 2FA depends on the type of second factor: SMS verification codes are vulnerable to SIM swapping attacks, while time-based one-time passwords (TOTP) or FIDO2 security keys offer higher security. If a platform hides the management entry, users may be unable to rotate compromised authenticators or revoke bindings to lost devices, thereby weakening the protective effect of 2FA.
User and Community Feedback
This change has sparked discussion in the community. Some users worry that if they cannot conveniently manage 2FA, they may be forced to choose less secure passwords or abandon the platform altogether. Reports from both Kotaku and PC Gamer emphasize users' expectations for transparency and security controls.
The Platform's Silence and Possible Reasons
As of now, Humble Bundle has not publicly explained this change. Possible reasons include an oversight during the redesign, or the platform is redesigning its security settings flow. However, the lack of communication has exacerbated user unease.
Implications for Digital Store Security Practices
This incident serves as a reminder to digital stores and gaming platforms that the accessibility of security features is crucial. Even small interface changes can have a significant impact on user trust. Platforms should ensure that security settings are not sacrificed during redesigns and should communicate changes to users in a timely manner.
Credential stuffing is one of the primary threats facing digital stores: attackers use email and password combinations leaked from other services to automate login attempts on the target platform. Because many users reuse passwords across different websites, once a data breach occurs on one platform, accounts on other platforms are also at risk. Two-factor authentication can effectively block such attacks because attackers lack the second factor even if they have the correct password. Therefore, the discoverability and manageability of security features directly relate to a platform's overall account security baseline. Additionally, industry practice shows that burying security settings deep in multiple menu layers or temporarily removing entries can lead to lower adoption rates, thereby expanding the attack surface. Platforms should treat security settings as a core feature rather than an optional configuration during interface redesigns, and proactively inform users through changelogs or in-site notifications.
Conclusion
Although the removal of the two-factor authentication settings entry in Humble Bundle's redesign may not be an intentional reduction in security, it has indeed caused inconvenience and concern for users. We hope the platform will respond promptly and restore the relevant functionality.
One-line Summary
Humble Bundle's redesign removes the 2FA settings entry, raising user concerns about account security.
Paragraph Summary
After the Humble Bundle store's interface redesign, users discovered that the settings page no longer offers the option to add or update two-factor authentication (2FA), raising widespread concerns about account security. Two-factor authentication is a critical measure for protecting linked payment information and game libraries, and the disappearance of the entry means users cannot enable, update, or revoke verification methods on their own. Community users worry this may force them to choose less secure passwords or abandon the platform. Humble Bundle has not yet provided a public explanation; possible reasons include a redesign oversight or an ongoing redesign of security processes. This incident reminds digital stores that the accessibility of security features is essential for maintaining user trust, and platforms should ensure security settings are not sacrificed during redesigns and communicate changes in a timely manner.
Related articles
FBI-Warned AI Hacking Tool ARTEX: Cost Disruption and Defensive Restructuring
The FBI-warned AI hacking tool ARTEX reduces penetration testing costs to $150-$1,500, causing financial data breaches and supply chain attacks. Learn how it works, real cases, and a five-step defense strategy.
FBI Warns: ARTEX AI Hacking Tool Breaches Systems in Three Hours
FBI warns the open-source AI pentesting framework ARTEX is being abused, with some intrusions gaining privileged access in under three hours, over 1,600 consoles exposed, and links to South Korean financial data breaches and the ConnectWise supply chain attack.
FBI Warns About Artex: AI-Driven Attack Framework Threatens Cloud Identity Security
FBI warns that the AI penetration testing framework Artex is being used for automated attacks: written in Go and driven by AI agents, it covers the full chain from reconnaissance to data exfiltration. This article analyzes its real threat to cloud identity and privilege security and key defense priorities.