Physics-Constrained Digital Twins: Defending Urban Pedestrian Counting Systems Against Stealthy Data Attacks
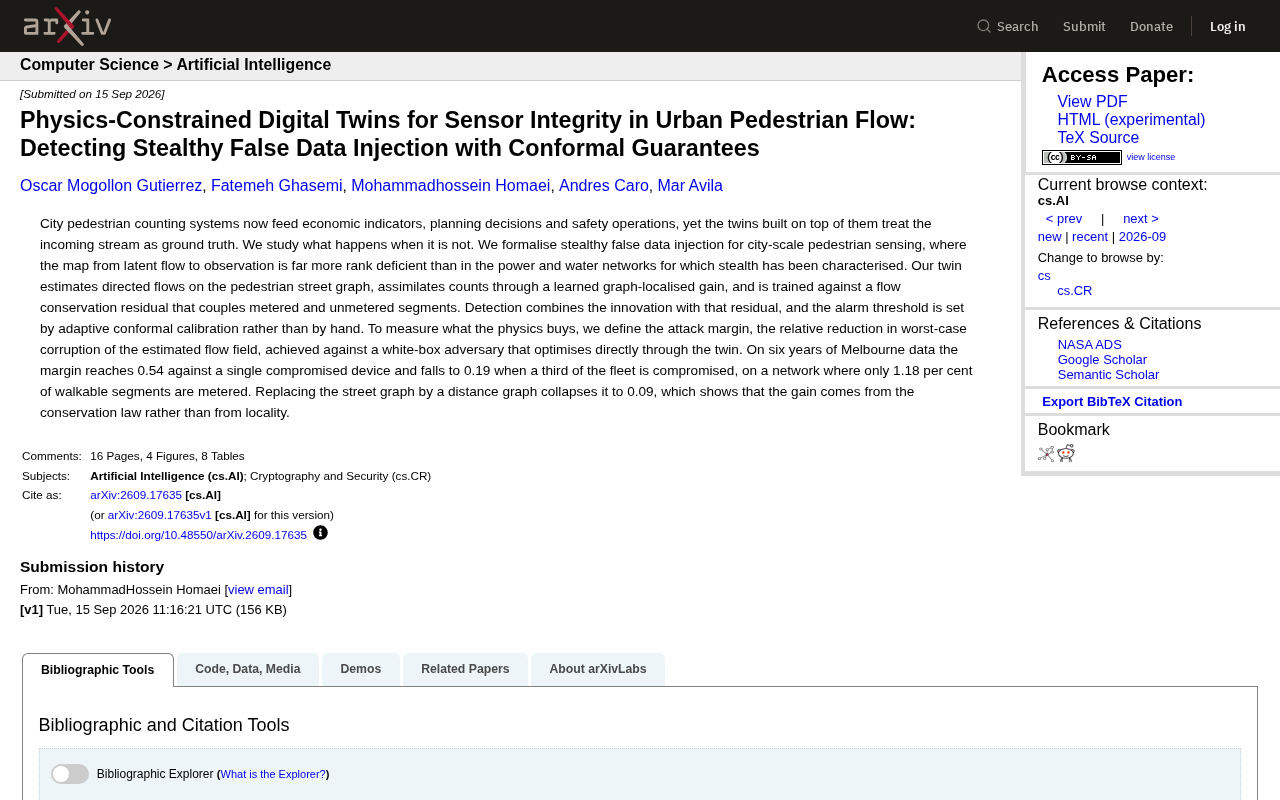
Flow conservation laws embedded in digital twins effectively counter stealthy false data injection attacks on urban pedestrian systems.
This arXiv study proposes a defense framework for urban pedestrian counting systems against stealthy false data injection attacks, embedding flow conservation laws into a digital twin that couples metered and unmetered street segments. Adaptive conformal calibration automatically sets alarm thresholds with quantifiable false alarm control. On six years of Melbourne data, the attack margin reaches 0.54 under single-device white-box compromise, and comparison experiments confirm that protection derives from the conservation law itself rather than spatial locality assumptions.
Urban pedestrian counting systems have long outgrown their original purpose of simply tallying passersby. Their data now feeds economic indicators, supports planning decisions, and drives security operations. Yet the digital twins built on top of these data streams often treat their inputs as ground truth beyond question. A recent paper published on arXiv poses a sharp question: what happens when that data has been maliciously manipulated?
The Stealthy Attack Threat Facing Urban Pedestrian Sensing
"Stealthy False Data Injection" refers to attacks where an adversary carefully crafts tampered data to slip past conventional anomaly detection, allowing the system to accept false information without raising any alarms. While this class of attacks has been systematically studied in power and water networks, the researchers argue that urban pedestrian sensing presents a far thornier problem.
The key difficulty lies in rank deficiency. The mapping from latent true pedestrian flows to actual observations is far more information-poor in pedestrian networks than in electrical or water networks. In other words, observable sensor data falls far short of fully characterizing the flow state across the entire network — in the Melbourne dataset used in this study, only 1.18% of walkable street segments are equipped with counting devices. This extreme sparsity makes attack detection enormously challenging, and gives adversaries more room to hide their tracks.
Building a Smarter Digital Twin Using Conservation Laws
The digital twin designed by the research team does not passively receive data — it actively estimates directed flows on a pedestrian street graph. It absorbs counting data through a "learned graph-localised gain" and is trained with a "flow conservation residual" as a constraint objective.
The core idea borrows from physics: the total flow entering a node should equal the total flow leaving it. This constraint couples metered segments (those with counting devices) to unmetered segments (those without), enabling the system to infer the state of directly unobserved segments. It is precisely this physical constraint that gives the digital twin its resilience against tampering.
Detection Mechanism and Adaptive Calibration
For detection, the system combines the "innovation" (the deviation between observation and prediction) with the conservation residual to form a composite decision criterion. Notably, alarm thresholds are no longer set by hand — instead, adaptive conformal calibration is used to determine them automatically.
The inclusion of Conformal Prediction provides statistically rigorous guarantees for detection, allowing false alarm rates to be tightly controlled. This matters enormously in real deployments — a security system that cries wolf too often will quickly be ignored by operators.
Conformal Prediction is a framework rooted in statistical learning theory. Its core idea is to use the residual distribution over a historical "calibration set" to construct confidence intervals for new predictions with finite-sample coverage guarantees, without requiring strong parametric assumptions about the data distribution. Unlike traditional fixed-threshold or Gaussian-assumption-based detection methods, conformal calibration dynamically adapts to shifts in the statistical properties of data streams — when urban pedestrian patterns shift due to holidays, weather, or unexpected events, thresholds adjust accordingly rather than staying frozen at training-time standards. The word "adaptive" further refers to the use of sliding windows or forgetting factors on non-stationary data streams to maintain a target false alarm rate (e.g., 5%) over long operational periods. This statistical rigor is especially important in safety-critical systems: if the detection system's own false alarm rate cannot be quantified and controlled, operators cannot distinguish real attacks from normal fluctuations, and the system's credibility collapses.
Attack Margin: Quantifying the Value of Physical Constraints
To measure exactly how much protection the physical constraints provide, the researchers define a metric called the attack margin — the relative reduction in worst-case disruption to the estimated flow field. This metric is computed against a "white-box adversary" who has complete knowledge of the system's internals and optimizes attacks directly through the digital twin. This is an extremely demanding evaluation setting.
On six years of real Melbourne data, the results are compelling:
- When a single device is compromised, the attack margin reaches 0.54, meaning physical constraints substantially blunt the attack's effectiveness;
- When one-third of devices are compromised, the margin drops to 0.19 — protection degrades as the scale of attack grows, which is intuitive;
- When the street graph is replaced with a simple distance graph, the margin plummets to 0.09.
The last comparison is particularly significant. It demonstrates that the protective benefit comes primarily from the conservation law itself, not merely from spatial locality. In other words, what actually matters is modeling physical reality — not simply the empirical assumption that neighboring nodes behave similarly.
A "white-box adversary" is one of the most stringent threat models in security evaluation: the attacker is assumed to have full knowledge of the defense system's internal structure, parameters, and inference logic, and uses this to craft maximally damaging attacks. By contrast, a "black-box adversary" can only observe the system's input-output behavior and has comparatively limited attack capability. The value of adopting a white-box setting is that it establishes a theoretical lower bound on protection — if the system maintains meaningful resistance against the strongest possible attacker, it will only perform better against real-world adversaries with incomplete information. This also means that the attack margins of 0.54 and 0.19 are conservative estimates under worst-case conditions; actual protection gains in deployment may be considerably larger.
What This Research Means
As smart city infrastructure grows increasingly dependent on sensor data, data integrity is becoming an underappreciated security vulnerability. This work reveals an important truth: treating sensor data as absolute ground truth is dangerous, especially in urban pedestrian networks where observations are extremely sparse.
Embedding physical conservation laws into digital twins, combined with the statistical guarantees provided by conformal prediction, offers a practical path toward trustworthy urban sensing systems. For city planners, infrastructure operators, and security researchers alike, this framework sends a clear message: against carefully designed stealthy attacks, purely data-driven approaches may be fundamentally blind, while hybrid approaches that incorporate domain physical knowledge represent a far more robust choice.
It is worth noting that this research remains at the academic stage, with conclusions grounded in data from a single city — Melbourne. Its generalizability to different urban network structures and attack scenarios remains to be validated.
Related articles

The Open Source Dilemma: A Non-Autoregressive Architecture Pioneer Overshadowed by Frontier Labs
An indie developer claims a frontier lab repackaged his year-old open-source non-autoregressive RL architecture as a breakthrough. We compare PPO sequence embeddings vs. RLCD parallel sampling and examine open source attribution gaps.

AI Plans an Entire Vineyard: A Real-World Experiment with 100 Grapevines
A Spokane hobbyist let Muse AI plan his entire vineyard — variety, spacing, irrigation, even the logo. He planted 100 Cabernet Franc vines and is documenting everything publicly.
Iceland's Treble Raises $18M to Bet on Voice Simulation Platform
Iceland-based voice simulation company Treble raises $18M. Its platform serves voice AI developers, AI wearables, and robotics firms. A deep dive into the technology and what the funding signals.