Police Transcription Firm Data Leak: Naked Cloud Server Exposes Law Enforcement Sensitive Information

A transcription service provider exposed sensitive data such as police interrogations and bodycam footage due to a cloud server without a password.
A company providing transcription services to police, prosecutors, and tech giants exposed highly sensitive data, including transcripts of police interrogation recordings and bodycam videos, on the public internet due to a cloud server lacking password protection. The incident was exclusively reported by the media. The vulnerability itself is a basic cloud misconfiguration, yet it reflects a systemic lack of security management at third-party service providers. The article analyzes the reliance of law enforcement and the tech industry on transcription services and points out that clients have difficulty directly supervising outsourcers' security practices, thereby amplifying supply chain risks. It concludes by calling on enterprises to extend security assessments beyond contracts, require independent audits, clarify data rules, and use automated configuration checks and continuous monitoring as a basic line of defense.
A Basic Mistake Exposes the Most Sensitive Data
According to an RSS source, a company that provides transcription services to police, prosecutors, and tech giants exposed a large amount of customer data on the public internet due to a simple security oversight. Specifically, a cloud server without a password stored transcripts of police interrogation recordings and bodycam videos. This incident, exclusively reported by the media, once again thrusts the security management problems of third-party service providers into the spotlight.
Who Relies on Transcription Services?
Law enforcement agencies and tech companies have long needed transcription services. Police need to convert interrogation recordings, emergency calls, and bodycam videos into text for archiving, retrieval, and use as evidence. Prosecutors similarly rely on transcribed text to prepare case materials. Tech giants may use transcription for content moderation, voice assistant training, or meeting notes.
This cross-sector dependency means that a security breach at one transcription company can simultaneously affect public safety, judicial proceedings, and corporate privacy. The data exposed in this incident includes police interrogations and bodycam content, which is extremely sensitive—such materials often involve open cases, personal privacy, and investigative details.
The Vulnerability Itself Is Not Complex
The report points out that the problem was a cloud server lacking password protection. In other words, anyone who knew the server address could potentially access the data directly. This type of "misconfiguration" vulnerability is not uncommon in cloud environments, but for service providers handling highly sensitive data, basic access control should be the baseline.
From a technical perspective, incorrectly setting public access permissions on cloud storage buckets or servers has been a common cause of multiple data breach incidents in recent years. Companies often overlook security configuration reviews under pressure to deploy quickly and cut costs, and customers of third-party service providers have difficulty directly supervising their security practices.
Cloud Storage Buckets and Access Control Lists (ACLs)
A "cloud server without a password" in most cloud platforms (such as AWS S3, Azure Blob Storage, Alibaba Cloud OSS) usually refers to a storage bucket mistakenly configured as "public-read" or "public-read-write." Cloud object storage is private by default, but users can open objects to anonymous access via Access Control Lists (ACLs) or Bucket Policies. Once set to public-read, anyone who knows the URL can download files directly without authentication. Such misconfigurations occur frequently because cloud consoles provide many shortcuts to lower the barrier to entry, and "one-click public" is often misused for temporary sharing and then forgotten. Automated scanning tools (such as AWS Config, the open-source project PMapper) and Cloud Security Posture Management (CSPM) products are designed to continuously detect such misconfigurations.
Third-Party Risk: The Weak Link in the Trust Chain
The core warning of this incident lies in third-party risk. Law enforcement agencies and tech companies choose to outsource transcription services usually for efficiency, but this also means they partially hand over control of sensitive data to external companies. Once a service provider has a security oversight, the client can hardly detect it immediately.
For law enforcement agencies, the leak of interrogation recordings and bodycam videos could affect case investigations, witness safety, and even judicial fairness. For tech companies, the exposure of customer data could lead to compliance issues and reputational damage. The report did not disclose the specific amount of data affected or the list of customers, but the combination of "police, prosecutors, and tech giants" itself indicates the broad scope of impact.
Third-Party Risk and Supply Chain Security
Third-Party Risk refers to the potential security exposure an organization introduces by outsourcing business to vendors, contractors, or service providers. In the data supply chain, even if the commissioning party has adequate security measures, sensitive data can still leak if the service provider fails. Regulatory frameworks such as GDPR Article 28, HIPAA Business Associate Agreements (BAAs), and SOC 2 reports in the financial industry all require commissioning parties to conduct due diligence and ongoing oversight of third parties handling their data. However, in reality, commissioning parties often lack visibility into the service provider's cloud environment, and security clauses in contracts are often mere formalities. Supply chain attacks (such as the SolarWinds incident) further illustrate that attackers tend to start from less protected downstream suppliers and infiltrate core targets indirectly.
Why Do Old Cloud Security Problems Keep Recurring?
Cloud servers without passwords exposing data is not a new problem. Over the years, similar incidents have been common, involving medical records, user photos, internal corporate documents, and various other types of data. The root cause of recurring problems lies partly in the complexity of cloud service configuration and partly in some companies' insufficient investment in security processes.
From industry practice, cloud service providers typically offer tools such as access control, encryption, and log auditing, but the ultimate responsibility for configuration falls on the user. For small and medium-sized service providers, the lack of a dedicated security team may exacerbate risks. In this incident, a company serving law enforcement agencies had such a basic oversight, indicating that there is still significant room for improvement in supply chain security reviews.
CSPM and Cloud Misconfigurations
Cloud Security Posture Management (CSPM) is a category of tools specifically designed to continuously monitor cloud environment configurations and identify deviations from security baselines. It can automatically detect issues such as public storage buckets, unencrypted databases, and overly permissive security group rules, and issue alerts. Gartner lists CSPM as one of the key technologies for cloud security. Research shows that the vast majority of cloud data breaches are not caused by sophisticated attacks but by misconfigurations. The value of CSPM lies in shifting left the review of "configuration as code" and embedding policy checks (Policy as Code) in the deployment pipeline, thereby blocking public exposure at the resource creation stage. For small and medium-sized service providers lacking dedicated security teams, adopting managed CSPM or the compliance check features built into cloud providers is a pragmatic choice to compensate for manpower gaps.
Implications for the Industry
This incident reminds all enterprises and institutions that rely on third-party data processing: security assessments cannot stop at contract terms. Customers should require service providers to provide independent security audit reports, clarify specific rules for data storage and access, and stipulate breach notification obligations in contracts. For law enforcement agencies, data classification and data minimization principles should also be considered to avoid handing unnecessary sensitive materials to external parties for processing.
At the same time, automated checks and continuous monitoring of cloud service configurations should become standard. A server without a password may be just the tip of the iceberg, reflecting a lack of security management processes behind it. In the context of rising data breach costs, the value of basic security measures cannot be underestimated.
Conclusion
Transcription services may seem peripheral, but they connect to the core data flows of law enforcement, judicial, and tech industries. A simple password omission is enough to expose the most sensitive information on the public internet. This incident involved no sophisticated attack techniques, yet it is enough to sound the alarm: in the data supply chain, the security level of every link determines the success or failure of overall protection.
One-line Summary
A transcription service provider exposed sensitive data such as police interrogations and bodycam footage due to a cloud server without a password.
Paragraph Summary
A company providing transcription services to police, prosecutors, and tech giants exposed highly sensitive data, including transcripts of police interrogation recordings and bodycam videos, on the public internet due to a cloud server lacking password protection. The incident was exclusively reported by the media. The vulnerability itself is a basic cloud misconfiguration, yet it reflects a systemic lack of security management at third-party service providers. The article analyzes the reliance of law enforcement and the tech industry on transcription services and points out that clients have difficulty directly supervising outsourcers' security practices, thereby amplifying supply chain risks. It concludes by calling on enterprises to extend security assessments beyond contracts, require independent audits, clarify data rules, and use automated configuration checks and continuous monitoring as a basic line of defense.
Related articles
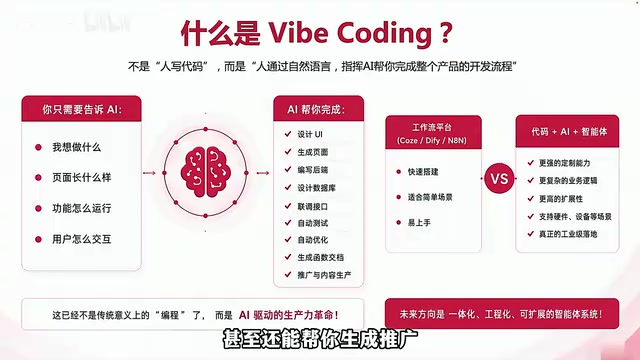
Vibe Coding for Absolute Beginners: A Practical Guide to AI-Assisted Programming
A beginner's practical guide to Vibe Coding: how AI-assisted programming lets people direct AI to write code, covering tools like Claude Code and Cursor, AI collaboration, multi-platform development, and automated operations for the full-chain one-person company.
Gemini 4 Neon Hands-On: Google's Mid-Size Model Takes On Opus 5.5
Hands-on with Gemini 4 Neon: Google's mid-size model rivals Opus 5.5 on coding tasks with strong coherence and long-task performance at lower cost, though 3D generation and architecture analysis remain weak.

AuthKit Custom Subdomains Go Free: Product Identity Starts at the Login Entry
WorkOS launches free custom subdomains for AuthKit, letting developers replace system-generated domains with product-matched authkit.app addresses—no DNS configuration, effective on save. We analyze the impact on brand trust, authentication infrastructure productization, and developer tool competition.