Revival Guide for an Old Beam+ Robot: Bypassing Server Dependencies and Retrofitting with ROS

The Beam+ robot can't authenticate after its server shut down; the community explores revival paths like ROS retrofits and server emulation.
This article covers the dilemma of a second-hand Beam+ telepresence robot that fails authentication because the manufacturer's server is offline, and maps community retrofit resources—an arXiv paper, two ROS-related GitHub repos, and a YouTube video—that point to software reverse engineering and exposed hardware interfaces. It breaks down the hardware and software stack, proposes three retrofit paths (server emulation, custom firmware, hardware-level controller replacement), and weighs risks like battery safety, missing documentation, and secure boot, highlighting community collaboration's role in giving old smart hardware a second life.
From a Second-Hand Marketplace to the Workbench: The Challenge of Reviving a Beam+
Recently, a Reddit user scored an Awabot/Suitable Tech Beam+ telepresence robot on FB Marketplace. The battery was dead, but the device booted successfully when powered via an external DC supply. However, he soon ran into a classic problem with old smart hardware: the device couldn't authenticate, likely because the server its software points to has long been shut down.
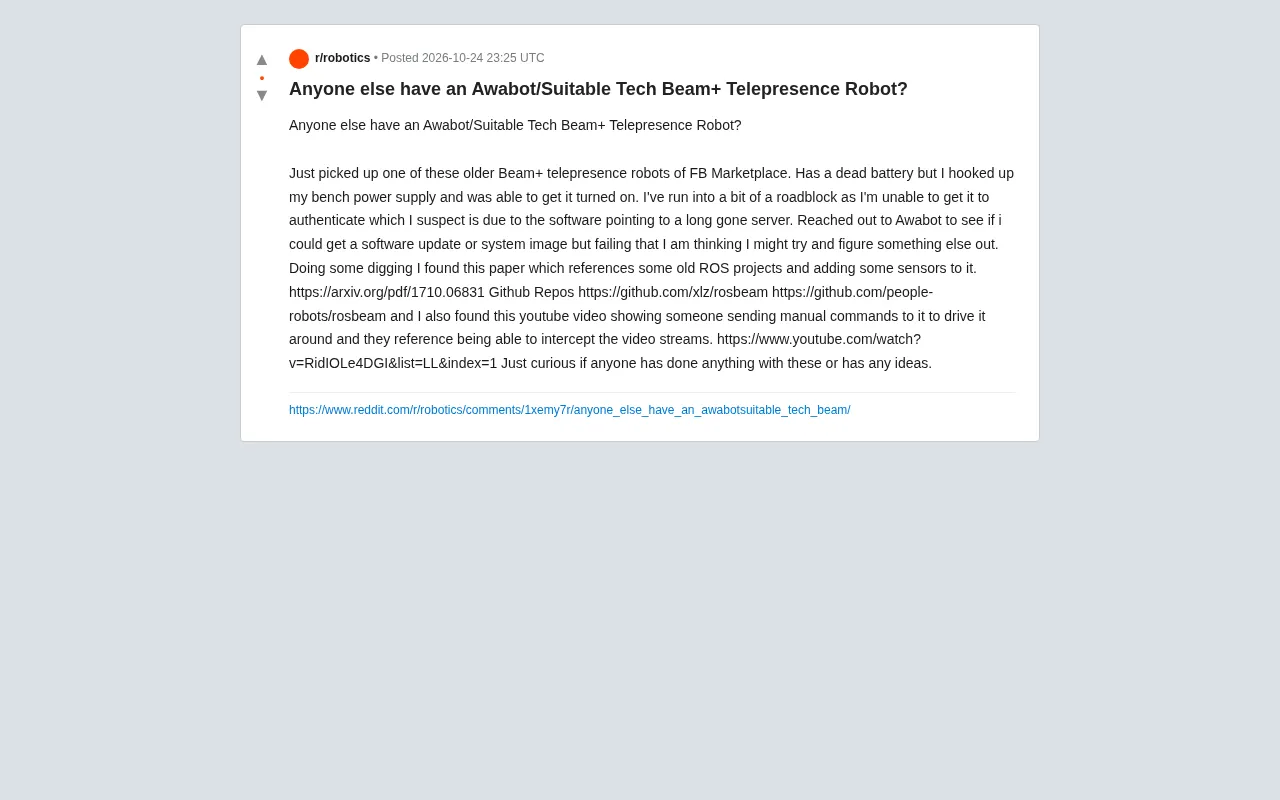
This is not an isolated case. As IoT devices cycle through generations, a large number of cloud-dependent devices turn into "electronic bricks" once manufacturers end support. The Beam+'s predicament is that its core functions—remote control and video streaming—rely heavily on backend services. Once the server goes offline, the device loses its soul.
Official Support Is Absent, Community Solutions Emerge
The user contacted Awabot (Suitable Tech's successor) for a software update or system image, but has yet to receive a positive response. So he began digging into open-source community resources.
Academic Papers and ROS Projects
He found an arXiv paper (1710.06831) that mentions adding sensors to the Beam+ and a ROS (Robot Operating System)-based retrofit. Following the paper's leads, he discovered two GitHub repositories: xlz/rosbeam and people-robots/rosbeam. These projects provide the code foundation for communicating with the Beam+'s low-level systems and may help bypass official server authentication.
ROS (Robot Operating System) is not an operating system in the traditional sense, but a middleware framework for robot development that provides hardware abstraction, inter-process communication, device drivers, and common algorithm libraries. It uses a distributed node architecture, where each functional module (such as motor control, sensor reading, and video stream processing) runs as an independent node and exchanges data via topics or services. For a device like the Beam+, running ROS on it would mean replacing the official closed cloud control with a localized node network that developers can freely compose and extend. The retrofit described in the arXiv paper uses ROS to take over the Beam+'s low-level hardware interfaces, thereby bypassing dependence on the manufacturer's servers.
Feasibility of Intercepting the Video Stream
Additionally, a YouTube video shows how to send manual commands to the Beam+ to control movement and mentions that the video stream can be intercepted. This suggests that the device itself may expose low-level interfaces that are merely blocked by the official software layer.
Multi-source cross-validation: The arXiv paper and GitHub repositories both point to ROS as the retrofit path, while the YouTube video provides a practical command-injection method. Together, the three indicate that the Beam+'s hardware is not completely locked down and that the community already has a foundation for reverse engineering.
Technical Breakdown: The Beam+'s Hardware and Software Architecture
To understand the possibilities for revival, we first need to understand what makes up a Beam+.
Hardware
The Beam+ is essentially a tablet on wheels, equipped with a microphone, camera, display, and motor drivers. Its compute unit may be based on an Intel Atom or ARM platform running a custom Linux system. The battery is a 24V lithium pack, which is relatively easy to replace or to substitute with an external power supply.
Software
The official software stack includes:
- Device-side client: connects to the cloud, handles audio/video streams, and executes movement commands.
- Cloud services: handle device authentication, session management, and media relay.
- User-side application: a PC or mobile control interface.
After the server shut down, the device-side client can no longer complete authentication at startup, limiting functionality. However, the low-level hardware and drivers are usually still usable.
Retrofit Roadmap: From Bypassing Authentication to Full Autonomy
Based on community leads, several viable retrofit paths can be planned.
Path 1: Intercept and Emulate the Official Server
By analyzing the network requests the device makes at startup, determine the authentication server address and protocol. Then use a local server to emulate responses and trick the device into completing authentication. This requires packet capture analysis and reverse engineering, but the ROS projects on GitHub may already contain relevant protocol information.
Packet capture analysis refers to intercepting network traffic between the device and the server using tools such as Wireshark or tcpdump, then analyzing the protocols, ports, authentication fields, and encryption methods used. For devices like the Beam+ that rely on cloud authentication, packet capture can help identify the authentication request URL, token format, and possible certificate validation mechanisms. If the communication does not use strong encryption or certificate pinning, a local emulation server can be set up to return a forged authentication-success response and trick the device into normal operation. This process usually requires DNS hijacking or modifying the device's hosts file to point the original server domain to a local IP. The ROS projects on GitHub may have documented some communication protocol details, which can significantly lower the barrier to reverse engineering.
Path 2: Flash a Custom System Directly
If root access can be obtained or the device can be flashed via recovery mode, a lightweight Linux distribution can be installed and a custom remote-control stack built on ROS. The rosbeam repositories may provide driver code for hardware interfaces, such as motor control and sensor reading.
Root access and recovery mode are two key entry points for retrofitting embedded Linux devices. Root access means obtaining the highest administrative privileges on the device OS, allowing software installation, system file modification, or boot script replacement. Recovery mode is a maintenance channel reserved by the manufacturer, usually triggered by a specific key combination or by shorting motherboard contacts, and it allows system images to be flashed via USB or network. For the Beam+, if recovery mode can be entered or a known vulnerability exploited for privilege escalation, the original firmware can be wiped, a lightweight Linux distribution (such as Ubuntu Core or Debian) installed, and a remote-control stack built on ROS. The driver code in the rosbeam repositories may include implementations of hardware interfaces such as motor control and camera capture, which can be reused or ported directly. Note that some devices use secure boot or hardware binding, so the boot chain must be confirmed as bypassable before flashing.
Path 3: Hardware-Level Retrofit
For hands-on tinkerers, the device can be disassembled, keeping the chassis, motors, camera, and screen while replacing the main controller with a Raspberry Pi or Jetson Nano to build a robot from scratch. Although this is more work, it completely escapes the manufacturer's software constraints.
Risks and Challenges
Retrofitting old hardware is not easy. First, the lack of official documentation and schematics increases debugging difficulty. Second, aging batteries can pose safety hazards, so replacing them with new ones or using a regulated power supply is recommended. Finally, some devices may use secure boot or hardware binding, requiring more advanced cracking methods.
The Value of Community Collaboration
This user's exploration demonstrates the power of the open-source community. By sharing papers, code, and videos, he not only found a direction for himself but also provided a reference for other Beam+ owners. If you own a similar device, consider joining the discussion and helping refine the retrofit solutions.
Single-source note: The video stream interception method mentioned in the YouTube video has not been verified by other sources, and its practical feasibility requires further testing.
Conclusion: A Second Life for Old Hardware
The Beam+ case is a microcosm of the rapid iteration of smart hardware. When manufacturers end support, users are not necessarily helpless. With open-source tools and community knowledge, these devices can be given new life and may even gain more flexible capabilities than the original. For tech enthusiasts, this is both a challenge and a source of fun.
One-line Summary
With the Beam+ robot unable to authenticate after its server shut down, the community is exploring revival paths such as ROS retrofits and server emulation.
Paragraph Summary
This article describes the plight of a second-hand Beam+ telepresence robot that cannot authenticate because the manufacturer's server has been shut down, and outlines the community's existing retrofit resources: an arXiv paper, two ROS-related GitHub repositories, and a YouTube video, which point to the possibilities of software-layer reverse engineering and exposed hardware interfaces. It breaks down the Beam+'s hardware composition and software stack, proposes three retrofit paths—emulating the official server, flashing a custom system, and hardware-level main controller replacement—and analyzes risks such as battery safety, lack of documentation, and secure boot. Finally, it emphasizes the value of community collaboration in reviving old smart hardware, noting that open-source tools can give devices that have lost official support a second life.
Related articles
64-Microphone Acoustic Camera Hands-On: Seeing Sound for $800
Hands-on review of the $800 TD2E acoustic imaging camera: a 64-microphone array localizes sound in real time, covers 2000–100000 Hz including ultrasound, and suits industrial inspection—though the software ecosystem is thin.

Manufacturing Accelerator Re:Build Raises $2.1B, Spins Out Slate Auto
Manufacturing accelerator Re:Build closes $2.1B funding, calling itself "America's answer to Shenzhen," and spins out Slate Auto. Known facts, positioning, and information gaps.
OpenAI's Public Breakthroughs Draw Academic Criticism: Research Transparency in the Spotlight
OpenAI announces math, CS, and physics breakthroughs and claims improved communication, but researchers tell The Verge dissatisfaction is mounting, criticizing selective disclosure and lack of reproducible details as the tension between corporate research and open science resurfaces.