Treat Your AI Agent Like an Intern: The Right Mindset for Agent Design

Treat AI Agents as interns rather than versatile colleagues, managing them with job descriptions, tools, permission boundaries, and checkpoints.
The article uses the "intern" metaphor to redefine the capability boundaries of AI agents: they are not versatile colleagues who can independently complete complex projects, but executors who need clear task instructions, appropriate tools, and restricted permissions. The author emphasizes that interaction itself is a state, and the agent must decide based on the task definition and historical context, checking results after each tool call to determine whether to continue or stop. In design, treat it like an intern: provide a clear job description (system prompt), tools matched to the task, minimized permissions, and human checkpoints at key milestones. This expectation management reduces the risk of the agent overstepping and losing control.
Why Is an AI Agent More Like an Intern Than a Colleague?
When building AI agents, many people instinctively imagine them as a versatile colleague who can independently complete complex projects. But a tech presenter on YouTube offers a more precise analogy: treat an AI Agent as a highly capable intern. Interns have a clear job description, available tools, and well-defined permission boundaries. They can handle specific tasks, but they need guidance, supervision, and feedback. This shift in perspective can help you avoid many pitfalls in agent design.
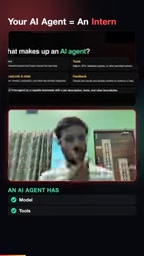
The Essence of Agent Interaction: State Machines and Task Definition
The video emphasizes that interaction itself is a state. An agent needs to understand the current task definition, the context (what has already happened), and the available tools. This is like assigning a task to an intern—you must clearly state the goal, the background, and the resources at hand. Without a clear task definition, the agent will flail around like a headless fly.
"interaction is a state, define the task, construction and what has already happened" — this sentence captures the core of how an agent operates: it is always deciding its next step based on the task definition and existing history.
Tool Calls and Result Checking
The agent needs to call tools such as search, APIs, and database queries, and after each call check the result to decide whether to continue or stop. The video specifically mentions: "check tools result and decide whether the continue or stop"—this means you need to design explicit stopping conditions for the agent. Just like an intern reports back to you after completing a step and you decide whether to proceed based on the result, you shouldn't let it run indefinitely.
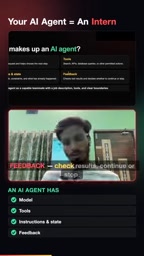
State Machine is a fundamental model in computer science that describes a system that can only be in one of a finite number of states at any given moment and transitions between states based on input events. Modeling an agent's interaction process as a state machine means that after each round of dialogue or tool call, the agent is in a well-defined "state"—for example, "waiting for user input," "retrieving," "waiting for tool return," or "task complete." The value of this modeling approach is that it forces designers to clearly define the entry conditions, available actions, and exit conditions of each state, thereby preventing the agent from looping endlessly under vague instructions. In practical engineering, frameworks such as LangGraph and AutoGen explicitly adopt state graph structures to orchestrate agent workflows, rather than relying solely on the free reasoning of large models.
ReAct (Reasoning + Acting) is a widely cited paradigm in the field of agent tool calling, proposed by Shunyu Yao et al. in 2022. Its core idea is to have a large language model alternately generate "reasoning traces" and "action instructions": the model first outputs a thought (Thought), then selects a tool action (Action), the environment returns an observation (Observation), and the model continues reasoning based on that. This is highly consistent with the article's description of "checking tool results and deciding whether to continue or stop." The significance of ReAct lies in combining pure language reasoning with external tool feedback, significantly reducing the probability of the model fabricating facts out of thin air. However, ReAct itself does not come with a stopping mechanism; in practice, systems usually need to set a maximum number of iterations, timeout limits, or explicit termination judgments—otherwise the agent may wander back and forth between tool calls.
How to Design an "Intern-Level" AI Agent?
1. Provide a Clear Job Description
When interns join, they receive a job description that clearly defines the scope of their responsibilities. An AI agent likewise needs a "job description"—that is, a system prompt or task specification—that defines what it can and cannot do. This effectively prevents the agent from overstepping into irrelevant operations.
2. Equip It with the Right Tools
Giving an intern a computer, accounts, and software is equivalent to providing an agent with tool interfaces. The video lists tool types such as search, APIs, and database queries. The number of tools and their permissions should match the task requirements; giving too many actually increases risk.
3. Set Clear Boundaries
The video has a key reminder: "जैसे कि हम सब कुछ access नहीं देते हैं intern को"—just as we don't give interns access to everything, an agent should not have unrestricted access either. The principle of least privilege applies here as well.
The Principle of Least Privilege originates from the field of information security and was first systematically articulated by Jerome Saltzer and Michael Schroeder in 1975. It requires that any subject (user, program, or agent) should only be granted the minimum access permissions necessary to complete its task, and only for as long as necessary. Applying this principle to AI agents means concretely: API keys given to agents should be scoped, database accounts should be granted only read-only or specific table permissions, and operations involving payments or deletions should require human secondary confirmation. Because large models are vulnerable to manipulation via prompt injection, over-authorization directly amplifies the attack surface—the consequences of a fully privileged agent being induced are far greater than those of an agent that can only read public data.
From "Colleague" to "Intern": The Value of the Mindset Shift
If you treat an agent as a colleague, you'll expect it to plan autonomously, report proactively, and handle vague requirements. But if you treat it as an intern, you'll more naturally provide detailed instructions, set checkpoints, limit permissions, and correct it promptly when it makes mistakes. The video's author believes that agents excel at handling "चुटे-चुटे task" (small, granular tasks) rather than end-to-end complex projects. This expectation management can significantly improve collaboration efficiency and reduce the risk of losing control.
Practical Advice: Manage Your Agent Like an Intern
- Task decomposition: Break large goals into small steps an intern can understand
- Regular check-ins: Check tool call results at key milestones rather than letting things run unchecked
- Permission tiers: Give sensitive operations read-only access only or require human confirmation
- Feedback loop: Feed erroneous results back as input to help the agent adjust its next step
These practices aren't new, but stringing them together with the "intern" metaphor helps teams reach consensus on the capability boundaries of AI agents. After all, a properly managed intern is often more reliable than an unsupervised "versatile colleague."
One-line Summary
Treat your AI Agent as an intern rather than a versatile colleague, managing it with job descriptions, tools, permission boundaries, and checkpoints.
Paragraph Summary
Using the "intern" metaphor, the article redefines the capability boundaries of AI agents: they are not versatile colleagues who can independently complete complex projects, but executors who need clear task instructions, appropriate tools, and restricted permissions. The author emphasizes that interaction itself is a state, and the agent must make decisions based on the task definition and historical context, checking the result after each tool call to decide whether to continue or stop. In design, you should treat it like an intern: provide a clear job description (system prompt), tools matched to the task, minimized permissions, and human checkpoints at key milestones. This expectation management reduces the risk of the agent overstepping and losing control, and helps teams form a shared understanding of its capability boundaries.
Related articles

AI Can Read Neural Network Weights Directly: Do Models Already Exceed Expectations?
A Reddit developer experiment shows language models can directly read neural network weights and infer their function. Astra, Opus 5.5, and Muse Spark 1.3 all passed the test, sparking discussion on model generalization and training sources.

India's Microdrama Market Explodes: EloElo Secures $80M Investment from NBCUniversal
EloElo secures $80M from NBCUniversal to boost StoryTV, its microdrama platform with over 33M monthly active users, as India's microdrama market draws global capital.

Acoustic Detection of Multi-Rotor UAVs: Fusing Handcrafted Features with Pre-Trained Embeddings
Study reveals data leakage from random splits in UAV acoustic detection, proposes source-disjoint protocol with stacked ensemble of handcrafted features and YAMNet embeddings, achieving 95.29% accuracy for low-cost drone detection.